Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
portal-moonshot-hx5.netlify.app is low-trust and potentially risky.
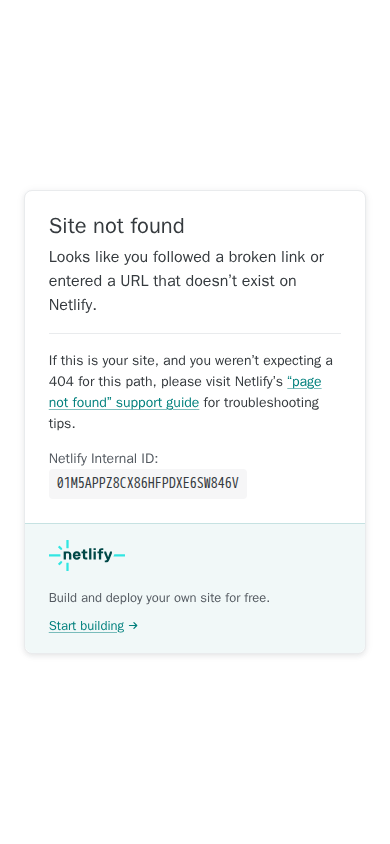
| What this site appears to be | Netlify-hosted 404 error page indicating the requested site/path does not exist. No forms, no solicitations, no financial or credential requests. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 5 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 1% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | 15 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 2026134 snapshots | Clear |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website presents a Netlify-hosted 404 “Site not found” page rather than an identifiable operating business, product, or service. Its visible content contains no solicitation, financial offer, credential request, or functioning site interface, so its apparent purpose cannot be established from the rendered page.
Scam/Impersonation Risk
The site has a high-risk interaction profile because external threat intelligence has confirmed malicious detections and a blacklist hit. This is the decisive contradiction, even though the visible page is only a generic Netlify error page and contains no overt financial or credential solicitation. Behavioral testing also observed hidden forms across all three successful runs, including password-form activity, while the visible page remained a 404; that mismatch materially increases concern about content or interaction surfaces not represented in the initial rendering. Abuse reports associated with the observed Amazon shared-infrastructure IP should be treated as contextual rather than proof that the hosting provider or infrastructure owner is responsible. No conflicting legal identities or confirmed brand-impersonation finding is established by the supplied evidence.
- The homepage rendered a “Site not found” Netlify 404 page with no visible forms, solicitations, or financial requests.
- Behavioral testing detected hidden forms in 3 of 3 runs and recorded 3 password forms, despite the visible 404 content.
- External reputation checks recorded 5 malicious detections and a confirmed blacklist status.
- The domain was first seen in 2026, with an age of 0.04 years (14 days); archival coverage records 134 snapshots across 2026, with 1 year tracked.
Regulatory Verification Notes
The rendered site does not provide an identifiable operator, legal entity, licensing statement, registration number, or governing terms, leaving identity and regulatory status unverified. This is a material disclosure gap for any site that might later request credentials, payments, or other sensitive interaction; it is distinct from the confirmed external threat findings described above. The transport certificate is technically valid and organization-validated, but certificate validity does not establish that the site operator is legitimate or authorized. No matching broker-reputation record was supplied.
- The available homepage is a generic hosting error page and contains no operator, legal, licensing, or registration disclosure.
- TLS uses an OV certificate issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 for Netlify, Inc., valid to 2027-03-19.
- The supplied regulatory assessment records identity verification as unverified and the on-page disclosure state as unclear.
What to Verify Next
Before any sensitive interaction, an independent determination should be made that the intended service is actually hosted at this domain and that its operator can be connected to a verifiable legal entity. Any claimed license should be checked directly against the relevant regulator’s public register, and contact channels should be confirmed through an independently sourced route rather than through the site alone. Until those checks are complete, activity should remain limited to passive observation; credentials, payment details, and financial transactions should not be submitted.
- The rendered page does not identify a functioning business or service to which an operator or license can be matched.
- The site’s visible 404 state conflicts with the hidden-form and password-form activity observed during behavioral testing.
- External threat detections and the confirmed blacklist status require independent validation of the domain before sensitive use.
Summary Verdict
The website is assessed as low trust with elevated sensitive-interaction risk. Its benign visible error page and valid transport encryption do not offset the confirmed external threat findings, unverified operator identity, and behavioral mismatch.
Infrastructure Integrity
The site is served through Amazon infrastructure using AWS CDN/WAF protection, and all observed addresses were edge servers; no origin candidate was identified. This provides an infrastructure-level mitigation against direct origin exposure, but it does not validate the site’s ownership, content, or safety.
- Served from AS16509 (AMAZON-02 - Amazon.com, Inc., US); 4 observed IP addresses were classified as CDN edge addresses.
- The observed edge addresses were 2a05:d014:58f:6200::258, 2a05:d014:58f:6200::259, 35.157.26.135, and 63.176.8.218.
- No likely origin IP was identified in the infrastructure analysis.
Closing Assessment
Prospective users should not proceed beyond passive inspection until the domain, operator, licensing position, and intended service have been independently validated; credentials, payment information, and financial activity should remain off-limits pending that validation.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, hosting and network, page content.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- The page contained a form a visitor cannot see.Behaviour in a sandbox
rule:BEHAV_HIDDEN_FORMS - Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
03 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
04 Page content
- The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2a05:d014:58f:6200::258 (Amazon Data Services Ireland Ltd, Content Delivery Network), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of portal-moonshot-hx5.netlify.app.
- The request stayed on portal-moonshot-hx5.netlify.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-10-05. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:58f:6200::258 |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | 0.04 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-10-05 |
| Archive snapshots | 134 |
| Reputation | VirusTotal: 5 flagged | AbuseIPDB: 1% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about portal-moonshot-hx5.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.