Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
proposals-firelight.finance shows high-risk / scam indicators.
| What this site appears to be | Firelight is a DeFi protocol that lets users stake XRP, bridged through Flare FAssets, to receive a liquid staking token and earn rewards. It also sells on-chain cover for DeFi risks. The page cites two audits and a bug bounty but gives no verifiable audit links, legal entity, or reward rate. It also includes a wallet-signed governance vote. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 14 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
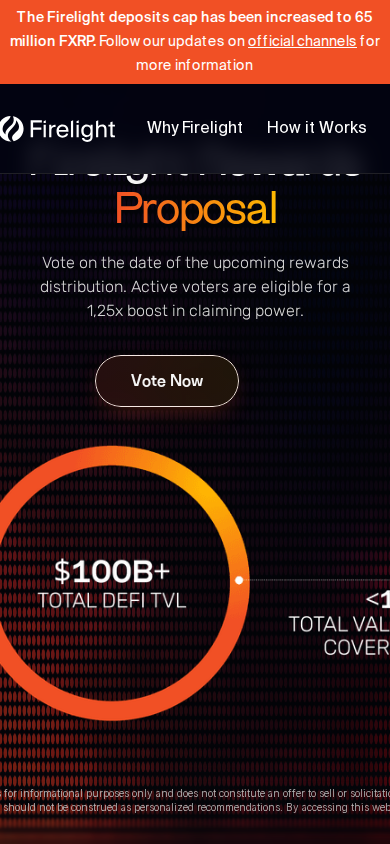
The site at proposals-firelight.finance is a single landing page for "Firelight – The Protection Layer for Digital Assets," a DeFi staking and cover protocol. It invites visitors to stake XRP, bridged through Flare FAssets, in return for a liquid staking token and "Firelight Rewards." It also offers on-chain cover against DeFi risks. The stated business model is that fees paid by third-party cover buyers are shared with stakers, and a governance proposal asks visitors to vote on a rewards-distribution date.
Scam/Impersonation Risk
Contradictory signals are present, and they are severe. Several independent threat-intelligence sources currently flag the domain as malicious, and a critical-severity threshold was crossed, so the domain is blacklisted. Three of the leading security vendors are among those flagging it. Infrastructure reputation cannot offset this. The domain was registered only weeks ago, yet the homepage asserts "$2B deployed" and "institutional-grade" readiness. Neither claim is backed by any verifiable history. The domain name combines the project's brand with the word "proposals". Brand impersonation was not positively detected, but the page cannot be confirmed as the project's official deployment. The homepage pushes a wallet-signed governance vote and offers voters a "1,25x boost in claiming power," which is an incentive to sign. The browser also recorded a wallet-signature request. The sandbox observed three outbound POST requests to non-whitelisted external destinations, a very high share of external traffic, and repeated console errors. Those behaviours are consistent with a deposit-before-service model and with wallet-interaction abuse. The staking model itself is high-yield DeFi: users must deposit XRP before any service is received, and no reward rate is stated. Because the deposit cap was "increased to 65 million FXRP," the page implies large pooled deposits with no verifiable controls. The protocol is also not recognised in the major DeFi protocol directory. No conflicting legal identities were found, so there is no identity contradiction in the strict sense. Evidence:
- Homepage and domain: registered 2026-09-16 (about 34 days, ~0.09 years old) through NICENIC INTERNATIONAL GROUP CO., LIMITED, expiring 2027-09-16.
- Web archive: 2 snapshots spanning 2026-09-16 to 2026-09-17 (1 year tracked), so the domain has no meaningful history behind the claims on the homepage.
- Homepage behaviour: 14 console errors, three non-whitelisted external POSTs and 83.7% peak external traffic during three sandbox runs, plus a wallet-signature request.
- Homepage claims: "$2B deployed," "Ultimate Risk Protection" and a raised deposit cap of 65 million FXRP, with no supporting evidence.
Regulatory Verification Notes
The homepage names no legal entity, jurisdiction, license or registration number, and no team members are identified. Its only legal text is a generic disclaimer that the content is informational and not an offer. Cover sales and yield-bearing staking would normally call for such disclosures. Ownership opacity is also present: the registration data does not connect the domain to an identifiable operator. The page cites two audits (OpenZeppelin and Coinspect), an Immunefi bug bounty and an incubator (Sentora). It links to none of them, so none of these assurances can be treated as corroboration. A quote attributed to a Sentora co-founder is likewise unverifiable. No third-party broker or regulator record was matched for this domain. Those absences are verification gaps and are secondary to the confirmed threat detections. Evidence:
- Homepage disclaimer: generic "informational purposes only" language with no operator, license or jurisdiction.
- Security section: audits and bug bounty are named but not linked.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: DV certificate issued by YE1, valid to 2026-12-15, which shows only that the domain is encrypted, not who runs it.
What to Verify Next
The first step is to establish whether this domain is the project's official site. That means reaching the project through channels known independently of this page, such as the project's established social accounts or a trusted aggregator, and checking whether the governance vote and staking interface are published there. The audit claims should be checked on the auditors' own sites and the bug-bounty program on its own platform. The operating legal entity, and whether any regulator oversees the cover or staking activity, should be confirmed through the relevant registries. Because the page asks for a wallet signature, no signing, approval or deposit should be attempted until official provenance is confirmed. Support and contact channels should likewise be confirmed independently. Evidence:
- Governance proposal: voting requires a wallet signature and rewards a 1,25x claiming boost.
- Security section: audit and bug-bounty claims are unlinked.
- Staking section: the page gives no reward rate, no legal entity and no team identities.
Summary Verdict
The assessment is a critical, high-risk posture. Confirmed adverse threat intelligence combines with a brand-new domain, unverifiable assurances and a deposit-first staking model. Sensitive interaction on this site is unsafe.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF on a trusted network, and every observed address is a CDN edge address. The origin server was not observable. This is a mitigating factor only. It shows that the domain is correctly fronted, but it says nothing about the operator's intent, and it does not offset the external threat detections.
Closing Assessment
The page should be viewed at most for passive reading. No wallet should be connected, no transaction or governance message signed, and no XRP or FXRP deposited. Any funds or approvals already linked to this site should be reviewed and revoked.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of proposals-firelight.finance.
- The request stayed on proposals-firelight.finance. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-16. Noted
- The earliest public archive of this site is from 2026-09-16. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3031::6815:11f6 |
| Name servers | kyree.ns.cloudflare.com, josephine.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-15 |
| Domain age | 0.09 years (continuous registration) |
| Domain expiry | 2027-09-16 |
| Archive first seen | 2026-09-16 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 14 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about proposals-firelight.finance at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.