Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
pulseredeem.live shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 8 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 63 reports; shared hosting inflates reports | Clear |
| Domain age | 4 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
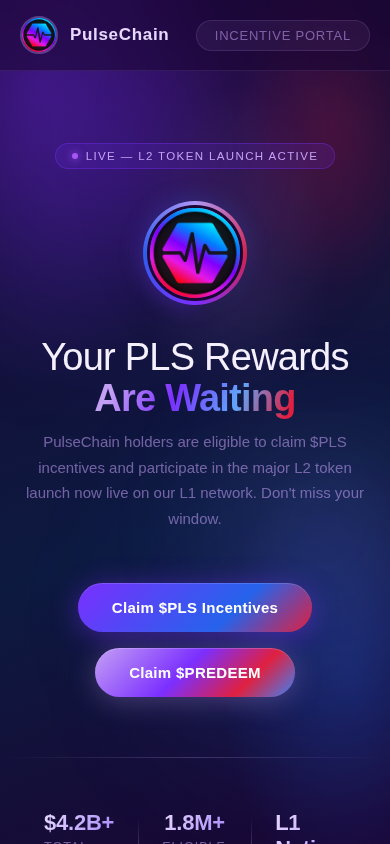
This website is a single-page "PulseChain — Claim Your Rewards" landing site on a newly created ".live" domain. It presents reward-claim, token-style messaging and appears intended to attract visitors into a token or airdrop-style redemption flow. The homepage carries only a short block of text and no substantive product, company, or support content.
Scam/Impersonation Risk
Contradictory signals are present and are serious. The domain is blacklisted in external threat intelligence, and several major security vendors independently flag it as malicious. That is a decisive reputational contradiction, and it outweighs the technical hygiene signals below. The homepage trades on the name of an established blockchain ecosystem and pairs it with an urgent "claim your rewards" call to action. Token-claim lures commonly use this pattern to push visitors toward wallet connection or credential entry. The evidence does not establish that the site is officially connected to that ecosystem. The sandbox run did not observe wallet-connection prompts, clipboard tampering, hidden forms, cloaking, or credential posts to third parties. That limits what was seen in this run but does not clear the site, because a drainer flow can be gated behind later interaction steps. Abuse reports exist against the address the site resolves to. Those reports sit on a shared provider address that serves many unrelated sites, so they are discounted. They are not attributed to this operator and do not add to the blacklist finding. The site's very recent creation and almost non-existent history are consistent with throwaway campaign infrastructure.
- Homepage: the title and page text frame the site as a "PulseChain" rewards-claim page, with very little other content.
- Reputation: 8 engines rate the domain malicious and 2 suspicious, including several tier-one security vendors, and the domain is confirmed on an external blacklist.
- Provenance: the domain is about 0.33 years old (registered in 2026). The web archive holds only 2 snapshots, both captured on 2026-07-05 (1 year tracked).
- Hosting reputation: 63 abuse reports were filed against a shared content-delivery address, with an abuse confidence of zero and the provider whitelisted, so they are treated as infrastructure noise.
Regulatory Verification Notes
The homepage identifies no legal entity, regulator, licence, or registration number, and no governance or accountability statement. Disclosure is unclear to the point of absence. No third-party regulatory or broker-database match was found, so no external reputational signal can be cited in the site's favour. A reward or token-distribution offering would ordinarily be expected to identify its issuer and terms. The real-world operator is not independently verified, and the site's own branding cannot be taken as proof of identity. The valid transport-encryption certificate confirms only that the domain is encrypted and controlled by its holder. It says nothing about who operates the site or whether the offer is genuine.
- Homepage: no company name, licence, registry reference, or terms of participation are presented.
- Transport security: TLS certificate issued by YR1 at domain-validated (DV) level, valid to 2027-01-27.
- Hosting: served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
- Protocol directories: the domain is not listed in any DeFi protocol directory, so no recognised protocol or TVL can be tied to it.
What to Verify Next
Any claim that a rewards or redemption programme exists should be checked only through the official project's own channels, reached independently of this site and not through links on it. The official domain should be confirmed against the project's published communications before any interaction. If the programme proves unofficial, the site should be reported to its hosting provider, its registrar, and the impersonated project's security contacts. A later re-scan is also worthwhile, since the reputation picture for a new domain can change quickly.
- Homepage: the reward-claim call to action is the only functional content and cannot be validated from the site itself.
- Classification: the page falls into a token-sale category, so any distribution terms should be confirmed against the official project.
- Contact and identity: no independently verifiable operator or support route is presented on the page.
Summary Verdict
The overall posture is high-risk. External threat intelligence contradicts the site, its identity is unverified, and its history is too short to offset that. It reads as a recently stood-up reward-claim page rather than an established, accountable operation, and the contradictory signals are decisive.
Infrastructure Integrity
The site sits behind a CDN and WAF, and only edge addresses were observable. The origin server was not visible, so the underlying hosting cannot be verified independently. Edge-only visibility can also conceal rapid content swaps behind an unchanged front end. The protection is a mitigating factor only. It does not offset the external reputation findings and does not demonstrate legitimacy.
Closing Assessment
Read-only viewing is the only use consistent with the evidence. Account login, wallet connection, credential entry, and any payment or token transfer should be avoided entirely until the offer is confirmed through the official project's own channels.
Written analysis generated 2026-11-01 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, history in the web archive, behaviour in a sandbox, hosting and network, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
03 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH
04 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
05 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 63 reports on hosting IP 216.198.79.65 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of pulseredeem.live.
- The request stayed on pulseredeem.live. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-07-05. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 216.198.79.65 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | YR1 |
| SSL expiry | 2027-01-27 |
| Domain age | 0.33 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-07-05 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 8 flagged | AbuseIPDB: 0% confidence, 63 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about pulseredeem.live at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.