Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
saakuru-launch.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
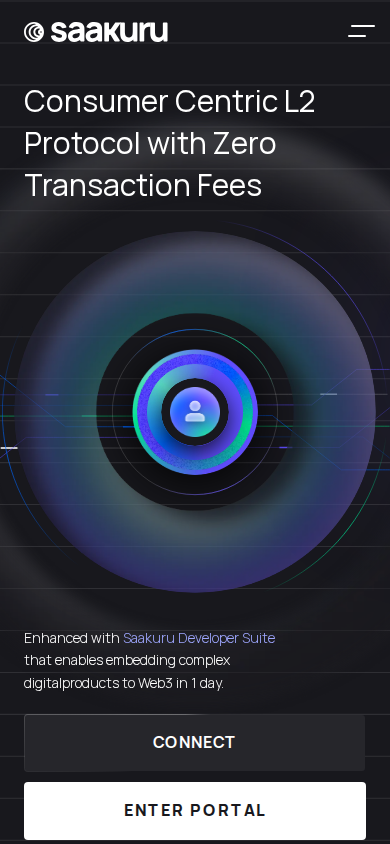
| How the site describes itself | Marketing landing page for Saakuru, an EVM-compatible L2 blockchain that advertises zero transaction fees and a developer suite for embedding products in Web3. It lists network statistics, developer and enterprise calls to action, a SKR token link, and wallet-connection options (Coinbase Wallet, Ledger). No financial return promises or sensitive data requests are visible, but legal identity and operator details are minimal. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-04 and re-scored on 2026-11-05. The certificate, the registration age and the page content describe the site as it was on 2026-11-04.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 2.1 years before captureWeb archive; a site on pages.dev has no registration of its own | Clear |
| Web archive | Archived since 202415 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 1 to 3 years before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
Saakuru's page presents it as a consumer-centric, EVM-compatible Layer 2 blockchain with "zero transaction fees". It is a single marketing landing page for developers and enterprises. It promotes a "Saakuru Developer Suite" said to embed digital products into Web3 "in 1 day", and it carries calls to action to connect a wallet, enter a portal, read documentation, talk to an expert, explore the SKR token, and join the community or core team. The apparent business model is infrastructure and enterprise onboarding around a token-linked blockchain ecosystem. The page hosts no deposit, yield, or payment flow of its own.
Scam/Impersonation Risk
Contradictory signals are present, and they are the decisive factor in this assessment. Independent reputation sources currently flag the site as malicious or suspicious, and the site is blacklisted by external threat sources. No brand impersonation, phishing form, credential harvesting, or conflicting legal identity was observed on the page. The page contains no login form, hidden form, or sensitive-data request, and the behavioral sandbox found no cloaking, clipboard manipulation, or wallet-drainer activity. The danger is therefore the external listing, not visible page mechanics. The listing matters especially because the page promotes wallet connection (Coinbase Wallet, Ledger) and a token link. That combination is a common route for wallet-targeting abuse, and the reputation flag cannot be set aside on the strength of a clean-looking page. The site is served from a shared platform subdomain rather than a standalone branded domain, and it is relatively young. For a project presenting itself as established blockchain infrastructure, this weakens the link between the page and any genuine project identity. The page's own claims are marketing assertions without independent proof. These include "562,851" active wallets with assets, "31,226,967" total blocks, "faster than 300ms" confirmation, and a "public-permissioned" design said to "reduce the risk of hacks to a minimum". The statistics appear as animated counters that load from zero, and no source supports them.
- Homepage: wallet-connection options (Coinbase Wallet, Ledger), an SKR token link, and a portal entry point sit beside unsourced network statistics.
- Homepage: security and performance claims ("public-permissioned", "gas-less by design", "faster than 300ms") are presented without any audit or independent attestation.
- Reputation checks: two scanning engines rate the site malicious and one rates it suspicious, and an external blacklist hit is confirmed. No major search-safety service flagged it.
- Provenance: the site resolves under a shared hosting-platform subdomain, with archive snapshots from 2024-10 to 2026-06 (15 snapshots, 3 years tracked) and a domain age of about 2.1 years.
Regulatory Verification Notes
The site makes no licensing or registration claim. No regulatory authority, license number, or registered legal entity is named. Apart from a copyright line, the page gives no company name, registered address, or accountable operator. Ownership and governance therefore remain opaque on the site itself, which is a transparency gap. A blockchain network that invites enterprises to build products on it, and that references a tradable token, would normally be expected to disclose its operating entity and jurisdiction. This gap is not a scam finding by itself. It compounds the external reputation signal, however, because nothing on the page lets a visitor tie the site to an accountable party. No broker-reputation dataset matched the site, so no third-party regulatory assessment exists to offset the concern. The site's DV-level certificate proves only control of the domain, not the identity of the operator.
- Homepage: only a copyright line identifies the operator, with no legal entity, address, or registration number.
- Homepage: no regulatory license or authority is claimed or referenced.
- Transport security: the TLS certificate was issued by WE1 (domain-validated, DV) and is valid to 2026-12-10, with about 36 days remaining.
- Hosting: the site resolves to AS13335 (CLOUDFLARENET, Cloudflare, Inc., US).
What to Verify Next
Before any engagement, the site's connection to the real Saakuru project should be confirmed through channels established independently of this page. Examples are documentation, announcements, or listings reached from a trusted source rather than from this address. The official domain, the SKR token contract address, and any wallet-connection endpoint should be matched against the project's independently confirmed records on a public block explorer. The operating entity and any claimed authorization should be confirmed with the relevant corporate or financial registry. The current threat-listing status should be rechecked with independent reputation services, since removal would materially change the assessment. Official support and contact channels should be confirmed through an offline or independent route.
- Homepage: the SKR token link and wallet-connection buttons are the highest-impact interaction points to confirm before any use.
- Homepage: the "Our Backers & Ecosystem" and "Core Team" sections name no verifiable parties on the captured page.
- Reputation checks: current listings by independent sources are the principal open item.
Summary Verdict
The site reads as a coherent-looking Web3 marketing page whose presentation does not outweigh an active external threat listing and the absence of any verifiable operator. The posture is high-risk and clearly cautionary. Real-world legitimacy and identity are unconfirmed, and the available evidence does not support treating the site as trustworthy for sensitive interaction.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN/WAF network, and all observed addresses are edge servers, so the origin host could not be seen. This is a mitigating factor only. It shows a mainstream, well-maintained delivery platform and a valid certificate from a known issuer. It cannot confirm who operates the content, and edge-only visibility makes it harder to independently verify hosting or detect rapid content changes. It does not offset the external reputation concern.
Closing Assessment
Browsing the page in a read-only manner is the limit of reasonable interaction. Wallet connection, credential entry, token transactions, and any financial commitment should be avoided until the threat listings are cleared and the operator is independently confirmed.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, registration and ownership and behaviour in a sandbox.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
03 Registration and ownership
- As a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
04 Behaviour in a sandbox
- Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of saakuru-launch.pages.dev.
- The request stayed on saakuru-launch.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-10-03. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2f78 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-10 |
| First seen (web archive) | 2.09 years before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2024-10-03 (2.1 years before capture) |
| Archive snapshots | 15 |
| Reputation | VirusTotal: 2 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about saakuru-launch.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.