Verdict
External threat listings named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
sand-usdt.netlify.app shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on netlify.app, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | A bare crypto wallet transfer form branded Trust Wallet that asks for a recipient address or domain and an amount of USDT, with no visible operator identity, terms, fees beyond an approximate USD value, or risk disclosure. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-14 and re-scored on 2026-11-16. The certificate, the registration age and the page content describe the site as it was on 2026-11-14.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-18)). It was not re-queried for this version. On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: web archive lookup.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 16 marked it malicious, 1 suspiciousVirusTotal; Fortinet, Kaspersky, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
| Hosted by | AMAZON-02Network registered in US | Noted |
The page as captured
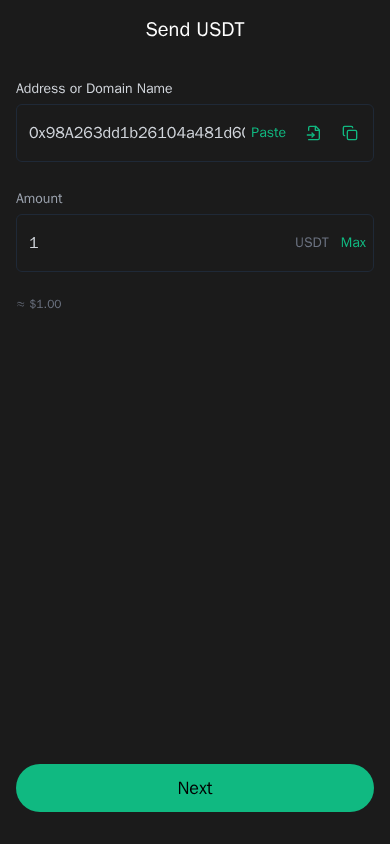
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
16 VirusTotal engines, including Fortinet, Kaspersky, Sophos, marked this site as malicious; independent sources confirm a listing for this site.
Overview
This website is a single-page crypto transfer form branded "Transfer Trust Wallet", served from a free Netlify-hosted subdomain. The only page read was the homepage, which offers a "Send USDT" screen. It has a field labelled "Address or Domain Name" with a "Paste" button, an "Amount" field in USDT with a "Max" option, an approximate dollar conversion shown as "≈ $1.00", and a "Next" button. It presents itself as a non-custodial wallet send interface, but the page names no operator and gives no explanation of how the service is funded or what it charges.
Scam/Impersonation Risk
The evidence points to critical risk. Two independent checks run by TrustSniffer meet its bar for a confirmed listing. A multi-engine malware-scanning aggregator reported sixteen engines flagging the address as malicious and one as suspicious, including Fortinet, Kaspersky and Sophos. Separately, a threat-intelligence feed lists the site as an actor distributing phishing, last seen on 18 October 2026. A transfer form that asks for a destination wallet and an amount is exactly the kind of page a phishing listing is meant to warn about. The page borrows the name of a well-known wallet brand, and nothing in the evidence connects it to that brand or to any identifiable operator. No conflicting legal-entity names were found, because the page names no legal entity. The only name on the page is the wallet branding itself. The analysis did not confirm impersonation of a specific brand, so the concern rests on the listings and on the page offering a financial transfer with no verifiable operator behind it. The critical rating reflects the combination of the confirmed listings, the unverifiable transfer page and the free-platform address.
- Multi-engine scan: sixteen engines flagged the site as malicious and one as suspicious, including Fortinet, Kaspersky and Sophos. It was captured on 14 November 2026.
- Threat-intelligence listing: the site is classed as a phishing actor, last seen 18 October 2026.
- Homepage: the page is branded "Transfer Trust Wallet". It shows one crypto-transfer form and no outbound links.
- Registration record: the address is a subdomain of a shared hosting platform, so the site has no domain registration of its own.
- Sandbox behaviour: three runs observed no requests sending data to other hosts. This does not address the listings above.
Regulatory Verification Notes
On the page we read, the site discloses none of the information a wallet or exchange service is expected to publish. The homepage lists no legal entity, no registration or licence, no fee schedule beyond the approximate dollar conversion, no terms or privacy notice, and no contact channels. Only the homepage was read, so these are gaps on the pages read and not statements about the site as a whole. The site's own wording, "Transfer Trust Wallet", is a claim and not verified identity. No licence is claimed, so none could be checked. No third-party broker reputation signal was matched. The only third-party signals are the security listings described above. The site's transport encryption is a valid organisation-validated certificate, but it was issued to the hosting platform and says nothing about whoever operates this page.
- Homepage: no operator, licence, fee, terms or contact disclosures appear in the captured text. The text is a few dozen characters of form labels.
- Network telemetry: the site was served from AS16509 (Amazon).
- Transport encryption: the TLS certificate was issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 (OV) to Netlify, Inc. It was valid until 2027-03-19 as seen at capture.
- Page metadata: no title, description or structured data beyond the wallet label was present.
What to Verify Next
Anyone who received this address should not treat it as the official wallet service. Whether it belongs to the real wallet brand should be checked through the brand's own channels, reached by typing its address independently or using its official app store listing. A link, message or advertisement that led here should not be used for that check. Any support or contact route should be confirmed the same way, never through anything shown on this page. Funds that were already sent to an address entered here should be reported promptly to the receiving exchange or wallet provider and to local authorities.
- Homepage: the page offers a single sensitive transfer form and no on-site way to identify or contact the operator.
- Homepage: the page contains no links, so it gives no route to terms or an operator profile.
Summary Verdict
The site is rated critical risk. Independent security listings confirm it as a phishing actor, and the page itself gives no operator identity or terms to offset that. Its legitimacy cannot be established from the evidence gathered, and its identity remains unverified. It should be treated as an unsafe place to move funds.
Infrastructure Integrity
The site resolved to four addresses on a large commercial cloud network, and no CDN or edge service was identified. The hosting arrangement is neutral. It neither mitigates the listings nor adds to them. The host's address was checked for abuse reports. The two reports found belong to the cloud provider's shared address, so they were discounted and are not attributed to this site.
Closing Assessment
Nothing should be pasted into this form, including recipient addresses and amounts, and no funds should be transferred through it. Safe use is limited to reading the page without interacting. Anyone who needs the real wallet service should reach it only through its officially published channels.
Written analysis generated 2026-11-16 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
7 findings contributed to this verdict, raised by external reputation, page content, and registration and ownership.
01 External reputation
- 16 VirusTotal engines marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The page runs on a free hosting-platform address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_FREE_PLATFORM_ADDRESS
03 Registration and ownership
- As a site on netlify.app, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (AMAZON-02), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Transfer Trust Wallet
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of sand-usdt.netlify.app.
- The request stayed on sand-usdt.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 2a05:d014:58f:6200::259 |
| Name servers | Not available |
| CDN / edge network | Not detected |
| Resolved IP addresses | 4 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 4 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on netlify.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 16 malicious, 1 suspicious | AbuseIPDB: 0% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about sand-usdt.netlify.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.