Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
sappling-main.app shows high-risk / scam indicators.
| What this site appears to be | A Sapling Airdrop landing page offering SAPLING token rewards in four tiers (up to $5,000) for connecting a Solana wallet and performing on-chain activity. It names no verifiable legal entity, token contract, team, audit, or contact details, and the text uses homoglyph and zero-width character obfuscation. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 15 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
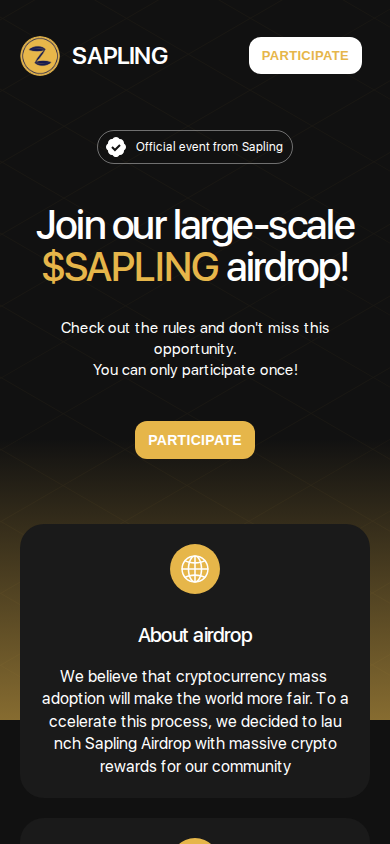
This website is a single-page landing site for a "Sapling Airdrop," presented as a live event. It invites visitors to connect a Solana wallet and complete on-chain activity to earn SAPLING token rewards in four progressive tiers, starting at small amounts and rising to as much as $5,000. The page frames itself as an "official event from Sapling" and calls the programme a "revolutionary," "fair and transparent" distribution platform. Its apparent business model is token-reward acquisition: it collects wallet engagement from participants, and no source of funding for the payouts is disclosed.
Scam/Impersonation Risk
This is a materially elevated-risk site. The evidence shows a confirmed blacklist listing and several independent threat-intelligence detections, including a flag from a tier-one security vendor. No brand impersonation and no conflicting legal identities were observed. The risk comes from external reputation combined with how the page behaves. The visible text is written with look-alike Cyrillic letters and invisible zero-width characters inserted into ordinary English words, such as the navigation labels and the headline "airdrop." This is a recognised evasion technique. It defeats keyword matching and automated content screening, and an honest promotional page has no reason to use it. The content is also a textbook airdrop lure. The homepage promises escalating rewards for wallet connection and "active engagement," and it gives no token contract address, no audit, no team, no explanation of where the rewards come from, and no explanation of what "basic tasks" or "on-chain activity" require. In practice this is the usual route to malicious signing requests or approval-based wallet draining. The "fair and transparent" claims are assertions with no supporting material. The domain spelling ("sappling" with a doubled letter, plus "main") does not match the "Sapling" name the page uses. Nothing independently ties the domain to any legitimate project of that name. Automated browsing sessions did not exercise the wallet-connection flow, so the absence of observed drainer behaviour is not assurance. Sessions also showed no cloaking, hidden forms or clipboard manipulation, which does not offset the reputational findings.
- Domain registered on 2026-10-07 through Tucows Domains Inc (about 13 days old, 0.04 years), so it has no operating history.
- Web archive holds only 2 snapshots, spanning 2026-10-07 to 2026-10-08 (1 year tracked), consistent with a newly launched site.
- Homepage text contains homoglyph and zero-width character substitutions throughout the headline, navigation and body copy.
- Homepage advertises tiered rewards "up to $5,000" for wallet connection and on-chain tasks, with no contract address, audit or funding source.
Regulatory Verification Notes
The site names no legal entity, operator, registered address, licence or registration number, and it makes no regulatory claims. It publishes no terms, privacy or legal pages and no contact channel of any kind. For a project asking visitors to link a financial wallet and move assets, this absence is significant. Ownership is also opaque, so no responsible party can be identified. This is an ownership-opacity condition, not an identity contradiction, since only one name ("Sapling") appears. No third-party broker or regulator record matched this domain, so there is no external regulatory standing to weigh. The confirmed blacklist and detection signals described above are the reputational context for this assessment. The technical profile fits a recently stood-up site: a basic domain-validated transport-encryption certificate, which shows only that the connection is encrypted and says nothing about who operates the site.
- Homepage and "About" content: no company name, jurisdiction, licence, registration number, team or contact details.
- No dedicated legal, terms or privacy pages were identified; the page carries no meta description, title tags beyond the airdrop name, or structured data.
- TLS certificate issued by YE1 (DV, domain-validated only), valid to 2027-01-05.
- Served from AS13335 (CLOUDFLARENET, Cloudflare, Inc., US), a network that hosts many unrelated sites and indicates nothing about the operator.
What to Verify Next
The first step is to establish whether a genuine "Sapling" project exists and whether this domain is referenced by it. That means locating the project's official channels through independent, established sources (not links found on this page) and confirming whether any airdrop is announced there. Any claimed token should be checked on a Solana block explorer for a published mint address, supply, holder distribution and creation date, and compared with what the page implies. Any licensing or registration claim the operator later makes should be confirmed directly with the relevant registry. Because the page gives no contact route, official support or contact channels should be confirmed offline or through the project's established public presence.
- Homepage: names the token only as "SAPLING" and gives no on-chain address for checking.
- Homepage: the "Official event from Sapling" claim cites no verifiable source.
- Homepage and navigation: the "Rules," "Instructions" and "Participate" sections do not state what permissions the wallet connection will request.
Summary Verdict
The overall posture is high-risk and clearly cautionary. Confirmed adverse reputation, a brand-new domain and evasion-style content, together with a high-stakes wallet interaction and no verifiable operator, outweigh the site's technically functional presentation. The evidence does not support treating this as a legitimate airdrop.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and web application firewall, and all observed addresses are CDN edge servers. The origin server is not observable. This is a mitigating factor only. It shows the site is competently fronted and the transport encryption is valid. However, edge-only visibility prevents independent verification of the real hosting and allows content to be swapped quickly. The protection cannot offset the external threat detections.
Closing Assessment
The page should be treated as read-only at most. No wallet should be connected to it, and no credentials, signatures, approvals or funds should be submitted. Anyone who has already connected a wallet should revoke token approvals, move assets to a fresh wallet if any signature was granted, and report the domain to the relevant security channels.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of sappling-main.app.
- The request stayed on sappling-main.app. It was not redirected to another domain. Clear
- Registration is published under Tucows Domains Inc. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-07. Noted
- The earliest public archive of this site is from 2026-10-07. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Tucows Domains Inc |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3032::ac43:9b32 |
| Name servers | everton.ns.cloudflare.com, jo.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-05 |
| Domain age | 0.04 years (continuous registration) |
| Domain expiry | 2027-10-07 |
| Archive first seen | 2026-10-07 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about sappling-main.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.