Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
scannablefakeid.eu shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the registration lookup did not return the domain's registrant, creation date, expiry date and country, the site asks visitors to sign in while its operator could not be verified and a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A storefront selling counterfeit fake IDs, fake passports, and fake residence permit cards. It promises documents that are 'virtually indistinguishable from authentic IDs' and 'undetectable', asks buyers for photos and shipping information, and accepts untraceable payment methods. It has no verifiable legal entity, address, or licensing, and it uses a countdown timer to pressure purchases. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-04 and re-scored on 2026-11-12. The certificate, the registration age and the page content describe the site as it was on 2026-11-04.
- One external source flagged this site when the evidence was captured: 2 VirusTotal engines marked it as malicious. No second source confirms it. The alert is from the evidence captured on 2026-11-04; it was not re-queried for this version and is treated as unconfirmed. On its own it would limit the score to at most 64; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain expiry date (WHOIS), name servers (DNS).
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (70%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe unconfirmed alert ceiling (at most 64) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 2 marked it maliciousVirusTotal | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 3.6 years before captureWeb archive; the registration lookup returned no registration date | Clear |
| Web archive | Archived since 202366 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
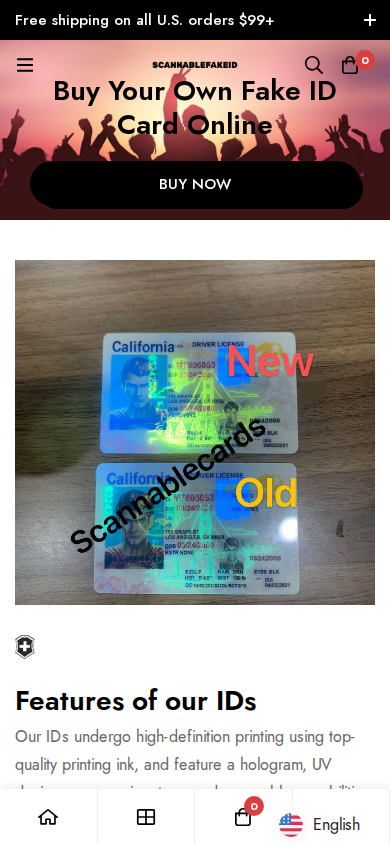
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 3 to 10 years before capture (web archive; the registration lookup returned no registration date).
- Public web-archive history exists since 2023.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
The website scannablefakeid.eu is an online storefront that presents itself as a seller of counterfeit identity documents. Its catalogue covers fake US driver's licences by state, fake passports and fake residence permit cards. A visitor is asked to upload a personal photo and shipping details, and the order is described as a standard online purchase with delivery in 7 to 12 days. Its apparent business model is the sale of forged identity documents, marketed as "scannable" and detection-resistant.
Scam/Impersonation Risk
The site presents critical risk. No brand impersonation and no conflicting legal identities were observed. The risk comes from what the site sells and how it sells it. Its own homepage offers forged identity documents and promises that they are "virtually indistinguishable from authentic IDs" and "undetectable" (translated from the site's marketing copy). It lists hologram, UV design, convex signature, scannable capability and a passed "bend test" as features. It also advertises a 90-day replacement guarantee and free shipping on US orders of $99 or more. Buying forged identity documents is unlawful in many jurisdictions, and sellers of this kind commonly take payment and deliver nothing, or misuse the identity photo and address they collect. The payment options point the same way. The site accepts Western Union, MoneyGram, gift cards, Steam Wallet and Bitcoin, with a 10% discount for Bitcoin. All of these are difficult to trace or reverse. A countdown timer and a "NEW BANK ACCOUNT!" banner add purchase pressure. The page's warning that products are "sold only for collectible purpose" and must not be used as identification (translated) contradicts its own marketing of undetectable, scannable IDs. Two antivirus engines on a third-party multi-engine scanner flagged the domain. That is a single-source alert and not a confirmed listing, and it is not what keeps the score at the floor. The score reflects the sum of many scored findings, including the page's content, forms and behaviour. The page presents five forms, including login, sign-up and password-reset forms. The behaviour analysis scored heavy page rewriting after interaction, a password form, heavy external posting and a high share of synthetic responses. The page is therefore not behaving in a benign or ordinary way.
- Homepage: sells fake IDs, fake passports and fake residence permit cards, and claims they are "undetectable" and "virtually indistinguishable from authentic IDs" (translated).
- Homepage: payment through Western Union, MoneyGram, gift cards, Steam Wallet and Bitcoin (10% discount), plus a countdown timer and a "NEW BANK ACCOUNT!" banner.
- Homepage behaviour: five forms were seen, including login, sign-up and password reset. 18 requests carried data to other hosts, all to destinations TrustSniffer recognises. This is still a scored finding.
- VirusTotal: 2 engines flagged the domain as malicious and 0 as suspicious. No top-tier vendor was among them, and Google Safe Browsing did not list it.
Regulatory Verification Notes
On the homepage, the only page read, the site presents no legal entity, physical address, contact channels, refund or returns terms, terms or privacy documents, or pricing and fee details. For an e-commerce business that collects identity photos and shipping data, each of these is an expected disclosure, and all of them were missing on the pages read. No licence or registration is claimed. Nothing on the page connects the site to a real-world operator, and its real-world identity remains unverified. No broker-reputation match was found for the domain. In this case the gaps are not a mere transparency note. The site openly sells a product that no licensed business could lawfully offer, so no registration could legitimise it. The web archive holds 66 snapshots, but the earliest historical captures contain only bare domain titles. They do not show what the site sold earlier, so continuity of purpose cannot be established.
- Homepage: no legal entity, address, contact channel, refund policy, terms or privacy page, or pricing disclosure was found on the pages read.
- Registration record: the domain was registered through PDR Ltd. Registrant, creation date, expiry date and country were missing from the lookup. Registration privacy is a scored finding.
- Web archive: 66 snapshots from 2023-03-15 to 2026-09-01 (a span of 1,266 days). The site was first seen in the archive 1,330 days before capture. The largest gap between snapshots was 318 days.
- Transport encryption: the certificate seen at capture was a DV certificate issued by WE1, valid until 2026-12-28. It confirms an encrypted connection only, not who operates the site.
What to Verify Next
Anyone who already sent a photo, shipping details or a payment to this site should contact their payment provider or bank at once, and monitor for misuse of the identity data supplied. Gift-card, Western Union and MoneyGram transfers are rarely recoverable, so the issuer or transfer service should be told promptly. Compliance and onboarding teams should treat any identity document traced to this vendor as non-genuine and escalate it under their fraud procedures. Any claimed operator identity should be checked against the official company register of the relevant jurisdiction. The page presents none. If the site's login or password-reset forms were used, the same password should be changed wherever else it is used.
- Homepage: orders require a personal photo and shipping information, so submitted data should be treated as exposed.
- Homepage: the accepted payment channels, including gift cards, Steam Wallet and Bitcoin, are hard to reverse once sent.
- Homepage forms: login and password-reset forms were present, so any reused credentials are exposed to the same risk.
Summary Verdict
The site sits at the bottom of the trust scale and carries critical risk. Its own content, the sensitive forms it presents, its behaviour on the page and an external alert converge on the same conclusion. The supportive technical signals, such as a valid certificate and a multi-year archive presence, show only that the site is operational and long-running. They carry no weight as evidence of legitimacy.
Infrastructure Integrity
The site is served through Cloudflare, Inc. All four observed addresses are edge addresses, and no origin address was observed. This is neutral and does not mitigate the findings above. Cloudflare also hosts a very large number of unrelated sites, so it says nothing about who operates this one.
Closing Assessment
The site should not be used for purchases, and no credentials, identity photos, shipping details or payments should be submitted to it. Interaction should be limited to reporting it through the relevant fraud or abuse-reporting channel.
Written analysis generated 2026-11-12 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
18 findings contributed to this verdict, raised by page content, several checks together, behaviour in a sandbox, external reputation, and registration and ownership.
01 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page asks visitors for sensitive information.Page content
rule:PAGE_FORM_SENSITIVE - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
02 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
03 Behaviour in a sandbox
- The page replaced a large part of its own content during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page showed a password field during the sandbox session, and it could not be matched to a recognised brand's sign-in page.Behaviour in a sandbox
rule:BEHAV_PASSWORD_FORM_PRESENT - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
04 External reputation
- 2 VirusTotal engines marked this domain as malicious when the evidence was captured.External reputation
rule:EXT_BLACKLIST_MEDIUM
05 Registration and ownership
- The registration lookup did not return the domain's registrant, creation date, expiry date and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page structure: 3 findings share one limit, because they describe one page structure. The limit applied, so together they counted for less than their sum.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
- Certificate and search-engine setup: 3 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of scannablefakeid.eu.
- The request stayed on scannablefakeid.eu. It was not redirected to another domain. Clear
- Registered through PDR Ltd. Noted
- The earliest public archive of this site is from 2023-03-15. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | PDR Ltd. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3032::ac43:a951 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-28 |
| First seen (web archive) | 3.64 years before capture; the registration lookup returned no registration date |
| Domain expiry | Not available |
| Archive first seen | 2023-03-15 (3.6 years before capture) |
| Archive snapshots | 66 |
| Reputation | VirusTotal: 2 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about scannablefakeid.eu at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.