Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
sedrezltd.best shows high-risk / scam indicators.
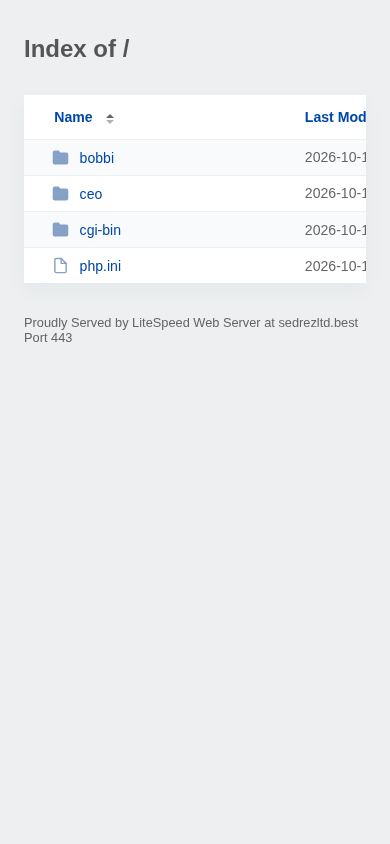
| What this site appears to be | Public directory index served by LiteSpeed Web Server. Lists folders (bobbi, ceo, cgi-bin) and a php.ini file; no forms, social links, or monetization present. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 5 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 18 days oldMost scam domains are under a year old | Risk |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website presents only a bare public directory index rather than a functioning business service: the homepage exposes folders named “bobbi,” “ceo,” and “cgi-bin,” together with a `php.ini` file, and identifies the server as LiteSpeed Web Server. No visible forms, commercial offer, social presence, or user-facing purpose is provided.
Scam/Impersonation Risk
The site has a confirmed external blacklist signal, with multiple threat-intelligence detections identifying the domain as malicious or suspicious. This is the decisive contradiction in the assessment and warrants a security-forward posture even though the captured homepage itself contains no payment form, login mechanism, or overt solicitation. The directory listing and exposed server banner also indicate an incomplete or potentially misconfigured web deployment, but they do not by themselves establish malicious intent. No separate brand impersonation or conflicting legal identity was observed.
- The homepage is an “Index of /” directory listing containing the `bobbi`, `ceo`, and `cgi-bin` folders and a `php.ini` file.
- External reputation checks recorded 5 malicious and 2 suspicious detections, including threat detections from Fortinet and Sophos.
- The domain is reported as blacklisted by two external sources; this is a confirmed blacklist signal rather than a mere broker warning.
- The homepage exposes the “LiteSpeed Web Server” banner and has no login form, hidden form, or external submission destination.
Regulatory Verification Notes
The captured site does not provide a business identity, licensing information, regulatory status, terms, privacy notice, or other substantive legal disclosure. This is a transparency and verification gap, not independent proof of fraud, but it prevents the operator or any regulated activity from being established from the available pages. The site’s transport security confirms encrypted delivery only; it does not validate the operator, business purpose, or regulatory standing.
- The homepage contains only a directory index and no identifiable company, licensing, or regulatory disclosure.
- Confirmed technical evidence shows service through AS13335, CLOUDFLARENET – Cloudflare, Inc., US.
- The TLS certificate is DV-validated, issued by YE2, and valid until 2027-01-09 21:33:56 UTC.
- No broker-reputation match was identified in the available third-party broker dataset.
What to Verify Next
Independent checks should be completed before any interaction beyond passive inspection. The relevant regulator or corporate registry should be consulted for any claimed operator or regulated service, and any official contact channel should be confirmed through an independently sourced route rather than through the site. Security teams should also determine whether the exposed directories contain downloadable files or active content and should treat any such content as untrusted. Credentials, account creation, downloads, and financial transactions should not be undertaken unless the blacklist and malicious-detection findings are independently resolved.
- The homepage provides no named operator or regulatory reference against which a registry search can be performed.
- The directory index exposes multiple folders and a configuration file, creating a need to inspect content safely before opening or downloading anything.
- Behavioral testing observed no forms, wallet connections, external posts, or external requests on the captured page, limiting the assessment to the exposed directory and associated reputation signals.
Summary Verdict
The available evidence supports a critical trust posture with material risk for sensitive interaction. The site’s apparent lack of functionality does not offset the confirmed malicious and blacklist signals, and the real-world operator remains unverified. No contradictions involving a named brand or competing legal identities were observed, but the external threat findings are sufficient to make the site unsuitable for credentials, account access, downloads, or financial activity.
Infrastructure Integrity
Cloudflare provides CDN/WAF protection, and all observed addresses were Cloudflare edge servers rather than a directly exposed origin. This reduces direct origin exposure and is a mitigating infrastructure characteristic only; it does not establish legitimacy or counter the external reputation findings.
Closing Assessment
Prospective users and enterprise controls should keep activity to passive observation, block or isolate the domain where appropriate, and require independent security and operator validation before permitting any sensitive interaction.
Written analysis generated 2026-10-12 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
03 Registration and ownership
- Registration details are held behind a privacy service, so no operator is named publicly. This is common and legal, and it also means there is nobody to check.Registration and ownership
rule:KF_WHOIS_PRIVATE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 25% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of sedrezltd.best.
- The request stayed on sedrezltd.best. It was not redirected to another domain. Clear
- Registration is published under Spaceship, Inc.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-11. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Spaceship, Inc. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3033::ac43:8953 |
| Name servers | ANUJ.NS.CLOUDFLARE.COM, MARISSA.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2027-01-09 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | 2027-10-11 |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 5 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about sedrezltd.best at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.