Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
shares-netnetcapital.com shows high-risk / scam indicators.
| What this site appears to be | NetNet Capital Management presents NET, a USDG-reserved token with staking distributions, alongside a set of real-money gambling games and 25x leveraged tokenized-equity cards, all reachable through wallet-funded subscriptions. The page self-describes as a parody and disclaims any offer of securities, yet it actively promotes deposit-based programs with no verifiable legal entity, licence, audit, or contact address, so the economic model is critical-risk. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 9 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20264 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
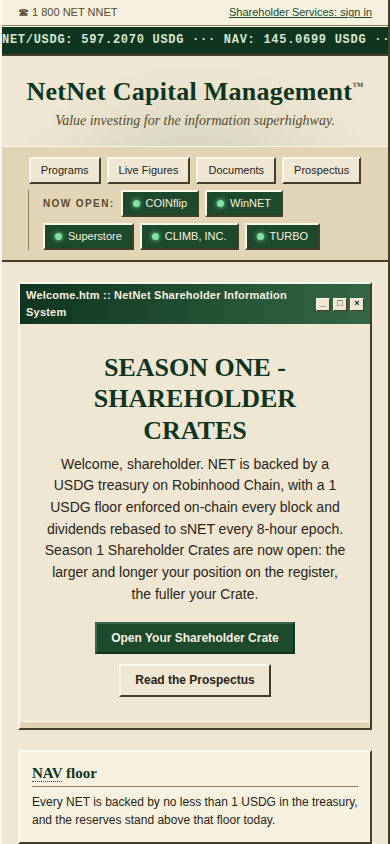
NetNet Capital Management, served from a recently registered domain, is a crypto-and-gambling portal styled as a retro "shareholder information system". It promotes NET, a token described as backed by a USDG treasury on Robinhood Chain, and a staking tier (sNET) that pays distributions every 8-hour epoch. Alongside these it offers real-money games (COINflip, Turbo Blackjack, crash and Plinko-style games), a nightly "WinNET" draw, a "Superstore", and 25x leveraged tokenized-equity cards (TURBO) tied to tickers such as MSFT, NVDA and AAPL. Its apparent business model is monetizing wallet-funded deposits through house edge, trading fees and token subscriptions.
Scam/Impersonation Risk
Contradictory signals are present and serious. The domain is blacklisted by external threat-intelligence sources. Several independent security engines classify it as malicious, including two major security vendors. No brand impersonation or conflicting legal identities were observed, so the risk does not come from copying another brand. It comes from the economic model, which carries many critical-risk indicators. The homepage ticker advertises a 1 USDG on-chain "floor", a premium of roughly four times net asset value, and reserves of about eleven million USDG. It also advertises distributions "3 times daily" and the assurance "the coin is fair". All of these are self-reported, and nothing independent corroborates them. Staking yields and a guaranteed floor presented as fixed mechanics resemble a deposit-and-yield scheme, because the funds being deposited are the same funds that pay the returns. The gambling layer adds a 5% fee on automated-market-maker trades and TURBO card activity, a 1% table rake and a house edge on every game. The 25x leveraged equity cards are described as sitting in a manager-custodied sleeve outside the reserves, so deposited funds pass into custodial control. A parody disclaimer states that nothing on the page is an offer. It directly contradicts the page's transactional calls to action, and it gives depositors no protection. Evidence:
- Homepage: the domain was registered in September 2026 (~0.1 years old, about 36 days), and the page already operates deposit-based programs.
- Web archive: 4 snapshots spanning 2026-09-14 to 2026-09-22 (1 year tracked), consistent with a newly launched property.
- External reputation: 9 engines rated the domain malicious and 3 suspicious, and it was not found in the DeFi protocol directory.
- Homepage: 12 distinct business-model red flags were recorded, including guaranteed-return language, deposit-before-service, custodial control of funds and opaque value flow.
Regulatory Verification Notes
The site offers no verifiable legal entity, licence, audit, registered address or named operator. The only "address" given is "Suite 4663, The Permanent Internet", which is not a physical location. Contact runs through a toll-style phone hotline that asks for a wallet address, plus a Telegram channel. Together these show that the operator cannot be identified or held accountable, even though the site takes real-money bets and leveraged positions. For a gambling and securities-like offering, the absence of any gambling licence, securities authorization or reserve attestation is a significant disclosure gap. The decisive concern is still the contradictory-signal evidence above, not this gap alone. No third-party broker or regulator record matched this entity. Evidence:
- Homepage and prospectus links: no company name, licence number, auditor or registered office is disclosed.
- Homepage: contact is limited to a phone hotline and a Telegram channel.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by YE1 (domain-validated, DV), valid to 2026-12-13. This confirms encryption only, not operator identity.
What to Verify Next
Before any engagement, the operator's legal identity should be established independently. Request the operating company, its jurisdiction and any gambling or securities licence, and check them directly with the relevant regulator's public register rather than through links on the site. The claimed reserves and the "immutable" distribution formula should be tested against audited, third-party attestations. Whether the on-chain contracts have been independently audited should also be checked. Any support or contact channel should be confirmed through an independent route before reliance. If a deposit has already been made, it should be documented, and the relevant platform or exchange should be notified. Evidence:
- Homepage: reserve, supply and staking figures are self-reported and carry no auditor attribution.
- Homepage: the stated 1 USDG floor and the distribution mechanics have no linked independent verification.
- Linked properties: the sub-sites for games, draws, store, careers and TURBO each present separate deposit surfaces, and none discloses an operator.
Summary Verdict
The site is rated at the lowest trust tier. External threat detections combine with a very new domain and a deposit-driven model offering gambling and high-yield token returns. The evidence converges on an elevated-risk posture with a clearly cautionary assessment. Technical hygiene and clean on-page behavior do not outweigh these contradictory signals.
Infrastructure Integrity
The site is fronted by a Cloudflare CDN and WAF, and every observed address is an edge server, so the origin host cannot be independently identified. This offers some protection against direct attack, but it does not validate the operator. Edge-only visibility also means content or behavior can change quickly without any change to the hosting footprint. Benign sandbox behavior, with no external calls, hidden forms or wallet-drainer activity, is a mitigating observation only.
Closing Assessment
The site should be treated as unsafe for logins, credential entry, wallet connection, deposits or any financial interaction. At most, read-only viewing from an isolated browser is reasonable. Anyone who has already interacted with it should secure their wallet approvals and report the matter to the relevant platform or authority.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, page content, several checks together, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of shares-netnetcapital.com.
- The request stayed on shares-netnetcapital.com. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-14. Noted
- The earliest public archive of this site is from 2026-09-14. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3031::6815:40e1 |
| Name servers | DUKE.NS.CLOUDFLARE.COM, KATELYN.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-13 |
| Domain age | 0.10 years (continuous registration) |
| Domain expiry | 2027-09-14 |
| Archive first seen | 2026-09-14 |
| Archive snapshots | 4 |
| Reputation | VirusTotal: 9 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about shares-netnetcapital.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.