Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
solhost.xyz shows high-risk / scam indicators.
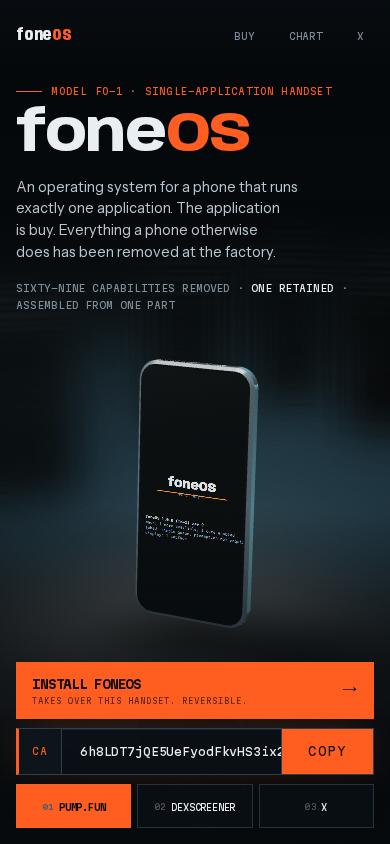
| What this site appears to be | A satirical landing page for the foneOS memecoin (Solana contract address shown, linked to pump.fun, DexScreener and X). It presents a joke single-app phone concept, has no forms or login, and explicitly disclaims any product, roadmap, financial return, or affiliation with real companies. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 12 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 2.6 years oldRegistered history | Clear |
| Web archive | Archived since 20242 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a single-page landing site for a Solana-based memecoin called foneOS. It is presented as a satirical product page for a "phone that runs exactly one application", where the only application is buying the token. A visitor sees a stylised handset specification with a laser-etched-contract-address conceit, a displayed token contract address, an "Install foneOS" button, and outbound links to a token launchpad, a market-tracking page and a social media account. Its apparent purpose is to promote and drive trading in the token. It sells no product and has no sign-up, login or payment form.
Scam/Impersonation Risk
Hard contradictory signals are present. The site is blacklisted by multiple external reputation sources, including three tier-one security vendors, and the volume of detections is high enough that independent reputation controls treat it as a critical external listing. The detections are not specified by category, so the evidence supports neither phishing nor brand impersonation. No conflicting legal identities and no impersonation of a known brand were observed. The blacklisting is nonetheless decisive and cannot be offset by the page's candid self-description. The homepage openly calls itself a joke and states that there is no product, no roadmap and no promise of financial return. It also shows no team, audit or legal entity behind the token, and a self-declared joke does not make the token itself safe to trade. The behaviour captured on the homepage adds to the concern. The "Install foneOS" button, described as taking over the handset and being reversible, requests fullscreen mode. The page also claims to read the device clock and battery. During loading it generated heavy third-party request traffic, including many outbound data submissions, and executed several suspicious inline scripts. It produced a large volume of console errors and a sharp DOM expansion after interaction. A page that sells nothing but runs this much client-side activity and asks the visitor to "install" something is a plausible vector for abuse. No wallet-connection, clipboard-hijack, wallet-drainer or credential-collection behaviour was detected in the test runs. The tracker footprint is minimal.
- Homepage: states that the token will not make money, that there is no product or roadmap, and that the site has no affiliation with real companies. It names no team, auditor or operating entity.
- Homepage: the "Install foneOS" control triggers a fullscreen request, and the page makes a device clock and battery read claim.
- Behavioural testing of the homepage: three successful runs recorded 114 external XHR requests, 28 external POST requests, 6 suspicious inline scripts and 52 console errors. There were no password forms, hidden forms or wallet-drainer runs.
- Domain provenance: the current registration record was created on 2026-02-17 (about 0.67 years old). The web archive holds only 2 snapshots, both from March 2024 (1 year tracked), so historical depth is shallow.
Regulatory Verification Notes
The site makes no licensing or registration claim and names no legal entity, regulator or jurisdiction. Its sole identity and disclosure content is the disclaimer of any financial return or affiliation. That is a content gap rather than evidence of wrongdoing in its own right. The site offers no basis on which a visitor could tie it to an accountable operator. No broker or regulatory-database match exists, so no third-party standing is available either way. Technical hygiene is basic. The site presents a valid but domain-validated-only certificate, which proves control of the domain rather than the identity of any organisation. It also lacks a page title, description and canonical metadata, consistent with a quickly assembled landing page. The new, thin trust history, the unverified real-world identity and the critical external listing together keep the site firmly in a cautionary classification.
- Homepage: contains no legal, terms, privacy or company pages, and no licence or registration references.
- Transport encryption: a TLS certificate issued by YE2 (DV), valid to 2026-11-29 (about 40 days remaining at analysis time).
- Hosting: served from AS13335 (CLOUDFLARENET, Cloudflare, Inc., US).
- Domain registration: through Namecheap, with an expiry date of 2027-02-17.
What to Verify Next
Before any interaction beyond viewing, the token contract address should be checked independently on a public Solana blockchain explorer. It should not be taken from the page itself. The reader should compare the address, the token creation date and the holder distribution against the claims the site makes. The project's social media account should be reached through an independent route rather than via the site's outbound links, to see whether it is the same project and not a copycat. The site's own "install" control should not be activated. The regulatory status of memecoin trading should be checked with the relevant authority in the reader's own jurisdiction. Whether the external listings remain active should be re-checked later, since a clean result would be needed before any reassessment.
- Homepage: shows a single token contract address and links only to a launchpad, a market tracker and one social media account.
- Homepage: gives no team, audit or developer information that could be cross-checked.
- External reputation: the critical listing is currently active and does not specify what the detections cover.
Summary Verdict
The assessment is a clearly cautionary, high-risk posture. The site is a new, thinly documented token-promotion page whose critical external reputation listing outweighs every positive technical or content indicator. Its transparency about being satirical does not remove that risk, and its real-world operator remains unverified.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and every observed address is an edge server. The origin server was not observable, so the real hosting location cannot be independently confirmed, and content could in principle be swapped behind the edge without notice. The shared edge infrastructure carries no abuse history, and the site's bot-protection layer showed no cloaking. This is a mitigating factor only. It does not offset the external reputation findings.
Closing Assessment
The site should be treated as unsafe for anything beyond passive viewing. No credentials, wallet connections or financial transactions should be attempted through it. Its "install" control should be left alone, and the other checks above should come first.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, page content.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- The page carried inline scripts written in a style TrustSniffer treats as suspicious.Behaviour in a sandbox
rule:BEHAV_SUSPICIOUS_INLINE_SCRIPTS - The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
03 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 30% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of solhost.xyz.
- The request stayed on solhost.xyz. It was not redirected to another domain. Clear
- Registration is published under NAMECHEAP INC. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-02-17. Noted
- The earliest public archive of this site is from 2024-03-28. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NAMECHEAP INC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 172.67.186.64 |
| Name servers | LYNN.NS.CLOUDFLARE.COM, WALK.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-11-29 |
| Domain age | 2.56 years (continuous registration) |
| Domain expiry | 2027-02-17 |
| Archive first seen | 2024-03-28 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 12 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about solhost.xyz at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.