Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
theroomemes.com shows high-risk / scam indicators.
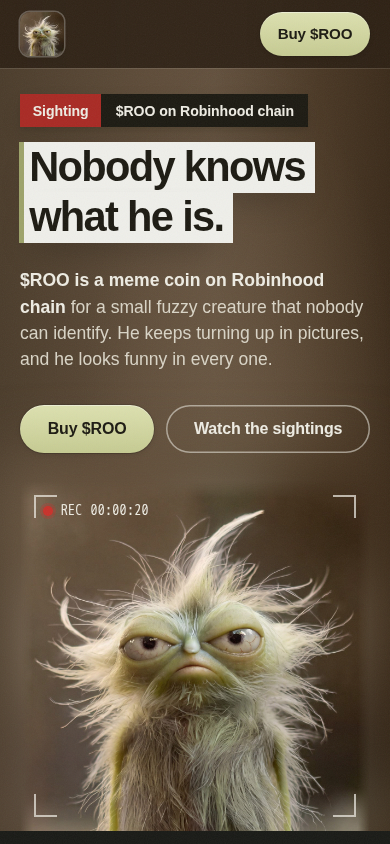
| What this site appears to be | A Robinhood-chain meme coin landing page for $ROO that promotes an airdrop to holders and sighting posters, with a wallet-connect registration button, an unverified contract address and a disclaimer of no intrinsic value. The captured text also includes unrelated embedded content, including prompt-injection attempts and notes about where to store seed phrases, which raises concern. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 15 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20265 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website is a single-page promotional site for "$ROO", a meme coin on the Robinhood chain, built around the tagline "Nobody knows what he is." It presents a mascot-style "sighting" gallery with downloadable images, an airdrop for token holders, a contract section, buying instructions and an FAQ. Its apparent business model is speculative sale of the token, supported by viral social posting and a promised reward drawn from an undefined share of the token supply.
Scam/Impersonation Risk
Confirmed contradictions are present, so this assessment is clearly cautionary. Several independent security engines currently flag the domain as malicious, and one tier-one security vendor is among them. This amounts to a confirmed blacklist presence in external threat intelligence, and it is the decisive factor in the assessment. No brand impersonation and no conflicting legal identities were observed, so the risk arises from the reputation evidence and the page's behaviour rather than from a copied brand. The homepage compounds the concern. Its airdrop requires visitors to "connect your wallet" to register, while the reward criteria stay unannounced and the allocation is only "a slice of the supply." That vagueness sits beside the reassurance that "nothing here ever touches your funds, just your address." The contract address is unverified, and no team, audit or revenue explanation accompanies it. The captured page text also contains embedded instructions aimed at automated analysis tools, together with notes about where to store seed phrases. Neither belongs on a legitimate token landing page, and both suggest content built to manipulate automated reviewers or to normalise handing over wallet secrets. The domain is only days old and was registered shortly before the first archive captures, which fits a short-lived promotional campaign and offers no track record to offset the detections. Evidence:
- Domain registered 2026-10-03 (about 16 days old, 0.04 years) through Dominet (HK) Limited, expiring 2027-10-03.
- Web archive shows 5 snapshots between 2026-10-03 and 2026-10-16 (1 year tracked), so no meaningful history exists.
- Homepage: the airdrop section asks visitors to connect a wallet to register, with undefined criteria and an undefined share of supply.
- Homepage text includes embedded prompt-injection content and seed-phrase storage notes unrelated to the token.
Regulatory Verification Notes
The site discloses no operating company, licence, registration number, legal-terms page or named team. Its only candid statement is a disclaimer that the token has no intrinsic value and no expected return. Beyond that disclaimer, the project offers no accountable counterparty to whom a holder could turn. Real-world operator identity remains unverified, and the registration details are incomplete, so ownership is opaque. A missing licence is a verification gap rather than proof of wrongdoing, but here it coincides with the confirmed external detections. The token's lottery-style "sighting reward" mechanics and the speculative airdrop are the kind of offering that attracts securities and consumer-protection scrutiny, yet the site cites no regulatory standing. No third-party broker or regulator database entry was matched. Evidence:
- The homepage and its FAQ name no legal entity, licence or registration authority.
- Served from AS13335 (Cloudflare, US).
- TLS certificate issued by YE1 (DV), valid to 2027-01-01. This is domain-validated only and says nothing about who operates the site.
- No contract audit or team disclosure appears in the captured page content.
What to Verify Next
Before any engagement, the token contract address should be checked independently on the relevant blockchain explorer for deployer history, holder concentration, liquidity lock status and any ability of the deployer to mint or restrict transfers. The airdrop's eligibility rules, snapshot date and supply allocation should be confirmed through an official, independently verified project channel, not through the landing page. The linked social accounts should be reviewed for account age, follower authenticity and consistency with the site. Any official contact channels should be confirmed through an independent route before relying on them. Evidence:
- The homepage publishes a contract address but gives no audit, deployer or liquidity information.
- The airdrop section leaves reward criteria and allocation undefined.
- The page links to profiles on X and Telegram, whose authenticity the site does not establish.
Summary Verdict
The website sits in a high-risk posture. Confirmed external threat detections, a newly created domain with no history, and a wallet-connect promotion with undefined mechanics converge on an assessment that sensitive interaction is unsafe. The page's candid disclaimers do not offset these signals, and the site cannot be treated as legitimate on the evidence available.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN/WAF, so every observed address is a shared edge node and the origin server is not visible. Edge-only visibility prevents independent verification of the true hosting and can mask rapid content swaps. This protective layer and the valid certificate are mitigating factors only. They do not offset the reputation risk, and a young domain with sparse subdomains is consistent with a short-lived deployment.
Closing Assessment
Wallet connections, token purchases, credential entry and any financial interaction should be avoided. Any browsing should be limited to read-only viewing from an isolated device or browser, with no wallet extension attached. Seed phrases or private keys must never be entered or stored anywhere because of this site's instructions.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
03 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of theroomemes.com.
- The request stayed on theroomemes.com. It was not redirected to another domain. Clear
- Registration is published under Dominet (HK) Limited. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-03. Noted
- The earliest public archive of this site is from 2026-10-03. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Dominet (HK) Limited |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3033::6815:1d92 |
| Name servers | KIRA.NS.CLOUDFLARE.COM, WEST.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-01 |
| Domain age | 0.04 years (continuous registration) |
| Domain expiry | 2027-10-03 |
| Archive first seen | 2026-10-03 |
| Archive snapshots | 5 |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about theroomemes.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.