Verdict
Read-only browsing is the most the evidence supports until a new check shows the listing has been cleared. An established site listed this way may have been compromised, in which case its owner is a victim.
ton-telegram.network was listed as malicious by VirusTotal security engines when the evidence was captured on 2026-08-20.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: the confirmed external listing ceiling (at most 24) applies, but the score is below it; a confirmed external listing limits the score; the registration lookup did not return the domain's registrant and country. The findings below give the detail.
| How the site describes itself | An unofficial informational site describing The Open Network (TON) and Toncoin: features, components (Storage, Proxy, DNS, Payments), and links to exchanges and community channels. Contains promotional referral-style links but does not itself appear to solicit deposits or host custody services. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-08-20 and re-scored on 2026-11-12. The certificate, the registration age and the page content describe the site as it was on 2026-08-20.
- 15 VirusTotal engines (Sophos among the engines that flagged it) marked this site as malicious when the evidence was captured on 2026-08-20, which meets TrustSniffer's bar for a confirmed listing. It was not re-queried for this version. On its own it would limit the score to at most 24; the score is lower because of the other findings below. The domain had been registered for 7 years; an established site listed this way may have been compromised, in which case its owner is a victim rather than the source.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 15 marked it malicious, 2 suspiciousVirusTotal; Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports | Clear |
| Domain age | 7.5 years oldRegistered 2019-02-24 | Clear |
| Web archive | Archived since 202170 snapshots | Clear |
| Certificate | Valid until 2026-10-23 when capturedIssued by YR1; that date has passed and renewal was not checked | Watch |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: 3 to 10 years at capture (registered 2019-02-24).
- Public web-archive history exists since 2021.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
15 VirusTotal engines, including Sophos, marked this site as malicious; this meets TrustSniffer's bar for a confirmed listing.
Overview
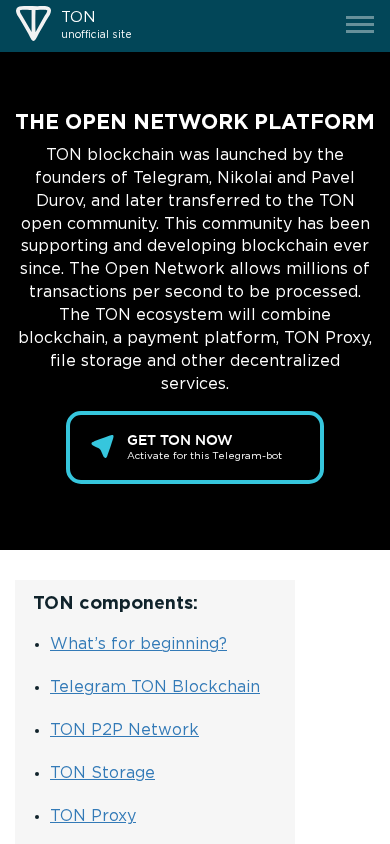
This website presents itself as an unofficial informational guide to The Open Network (TON) and the Toncoin cryptocurrency. It describes the platform's components (storage, proxy, DNS and payments), tells the story of the project's origin, and offers a "Get TON now" call to action alongside a prompt to activate a Telegram bot. It appears to be sustained by promotional links to third-party exchanges and community channels rather than by selling financial products itself.
Scam/Impersonation Risk
The site is critical risk, and contradictory signals are present. 15 engines, including a leading security vendor, Sophos, flagged the site as malicious, and 2 more rated it suspicious. This meets TrustSniffer's bar for a confirmed listing. It rests on a single source, VirusTotal, so it is not described as a blacklist entry. The report does not say what the listing relates to, and it does not speculate about the cause. The domain name pairs "ton" with "telegram", and the site is not Telegram. The page labels itself an "unofficial site", yet it tells the story of Telegram's founders and the project's transfer to a community. This lets the name borrow credibility from a well-known brand. No conflicting legal identities were found. The homepage hosts no forms, login or password fields, and no payment collection. The page's own mechanics still sent data to other hosts in 42 requests, and 72 percent of files loaded from other domains. These are scored findings, although none of the requests went to destinations TrustSniffer does not recognise.
- VirusTotal (alerts captured 2026-08-20): 15 engines rated the site malicious and 2 rated it suspicious, including Sophos.
- Homepage: titled as the TON blockchain platform and labelled "unofficial site", while the domain name contains the Telegram brand.
- Homepage behaviour capture: 42 requests sent data to other hosts, none of them to destinations TrustSniffer does not recognise, and 72.0% of files loaded from other domains.
- Web archive: 70 snapshots from 2021-11-23 to 2026-05-15 (a span of 1,634 days, longest gap 211 days), with the same title in the samples checked.
Regulatory Verification Notes
The site presents no licence or regulatory claim, and none is expected of an informational reference site. Identity is not verified. Two linked profiles on recognised social networks make a connection to a real project community likely, but the links the site publishes are not independent evidence. On the pages read, which covered only the homepage, no contact channel and no terms or privacy page were found. These are the disclosures such a site is expected to make. The homepage promotes referral-style links to Binance, Mercuryo, OKX, FTX and EXMO and to Telegram, Twitter, Instagram and Quora channels. It also makes scale claims about TON, such as processing "millions of transactions per second" (the site's own wording). The site presents these as fact and offers no operator or source to back them. No third-party broker profile was matched.
- Registration record: domain registered 2019-02-24 (~7.5 years at capture) through Porkbun LLC, with expiry recorded for 2027-02-24.
- Hosting: served from AS14061 (DigitalOcean, LLC).
- Transport encryption: TLS certificate issued by YR1 (DV), valid until 2026-10-23. That date has since passed and renewal was not checked.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "YR1" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site.
- Homepage: contact channels and terms or privacy content were not found on the pages read.
What to Verify Next
The site calls itself unofficial, so its claims about TON should be checked directly with the project's official channels, reached by typing their addresses rather than following this site's links. Any exchange named on the homepage should be reached through its own official site, not through the referral-style links presented here. The listing reflects the capture date of 2026-08-20. Its current status should be checked directly with the security vendors that flagged the site before any reliance on the domain. A route to the site's operator should be obtained independently, since none was found on the pages read.
- Homepage: external links point to five exchanges and to social channels, and the site presents the "Get TON now" call to action.
- VirusTotal: the flagging engines include Sophos, so the vendor can be checked directly.
- Homepage text: the page identifies itself as "unofficial site".
Summary Verdict
TrustSniffer assesses the site as critical risk. The score is held down by the external blacklist kill switch ceiling, and the supporting signs of an established site do not change that. Its identity connection to a real project community is likely but unverified.
Infrastructure Integrity
The domain resolved to a single IP address, which appears to be the origin, and no CDN was detected, which is neutral. The address's abuse record was checked, and 0 reports were recorded. This neither offsets the listing nor adds to it.
Closing Assessment
A prospective user should treat the site as a critical-risk source. It should be used, at most, for reading. The exchange links and the bot-activation prompt should not be followed. Any TON wallet, exchange or community resource should be reached directly through its own official channels.
Written analysis generated 2026-11-12 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
10 findings contributed to this verdict, raised by governance, page content, behaviour in a sandbox, and registration and ownership.
01 Governance
- When the evidence was captured, 15 VirusTotal engines marked this domain as malicious, which TrustSniffer counts as a confirmed external listing, and that caps the score whatever the other checks found. This ceiling (at most 24) applies, but the score is below it, so it does not set the score.Governance
rule:GOV_CRITICAL_BLACKLIST - A confirmed external threat listing caps the score at the bottom of the scale.Governance
rule:gov_external_blacklist_kill_switch
02 Page content
- The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Behaviour in a sandbox
- Most of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - An automated reading of the page's network activity judged some requests unusual for this kind of page, although every destination was a service TrustSniffer recognises.Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
04 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Third-party connections: 3 findings share one limit, because they all measure one fact: the page loads files from other hosts. The limit applied, so together they counted for less than their sum.
- Certificate and search-engine setup: 2 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- 2 linked profiles on recognised social networks
What TrustSniffer observed
First-party facts recorded during the assessment of ton-telegram.network.
- The request stayed on ton-telegram.network. It was not redirected to another domain. Clear
- Registered through Porkbun LLC. Noted
- DNS for this domain is served by porkbun.com, across 4 name servers. Noted
- The domain is registered until 2027-02-24. Noted
- The earliest public archive of this site is from 2021-11-23. Clear
- It is hosted on DIGITALOCEAN-ASN, a network registered in US. Noted
Domain intelligence
| Registrar | Porkbun LLC |
|---|---|
| Hosting | DIGITALOCEAN-ASN - DigitalOcean, LLC |
| Network registered in | US |
| Server IP | 138.68.86.9 |
| Name servers | maceio.ns.porkbun.com, curitiba.ns.porkbun.com, salvador.ns.porkbun.com, fortaleza.ns.porkbun.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR1 |
| SSL expiry | 2026-10-23 (the certificate seen at capture; this date has passed and renewal was not checked) |
| Domain age | 7.49 years (registered 2019-02-24) |
| Domain expiry | 2027-02-24 |
| Archive first seen | 2021-11-23 (4.7 years before capture) |
| Archive snapshots | 70 |
| Reputation | VirusTotal: 15 malicious, 2 suspicious | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about ton-telegram.network at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.