Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
treasurys-firelight.finance shows high-risk / scam indicators.
| What this site appears to be | Firelight is a DeFi protocol page offering XRP staking rewards through a liquid staking token and a DeFi cover marketplace funded by staker fees. It cites two audits, a bug bounty, and institutional backing, but names no legal entity, links no audit reports, and relies on broad disclaimers. Because the core action is depositing XRP for yield, the business model is rated high-risk despite the absence of phishing signals. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 14 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
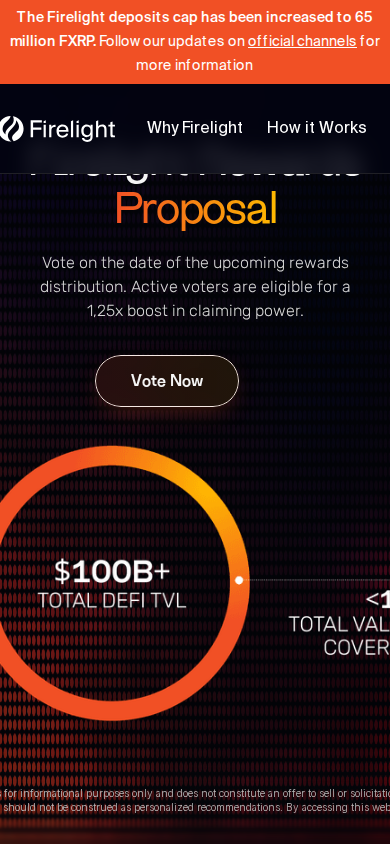
Firelight, presented at treasurys-firelight.finance, is a single-page DeFi landing site for a protocol that offers staking of XRP through a bridged token. Visitors are invited to stake XRP, receive a liquid staking token, earn "Firelight Rewards", and take part in a marketplace of on-chain protection cover funded by fees paid by third-party cover buyers. The page also carries a reward-distribution vote and positions itself as "the protection layer for digital assets". Its apparent business model is yield generation from user deposits, supplemented by fees from cover purchasers.
Scam/Impersonation Risk
This is a high-risk, clearly cautionary case. Multiple independent security engines currently flag the domain as malicious, and an external blacklist listing is confirmed. The domain was registered only weeks ago, yet it presents a mature-looking protocol with audit, bug-bounty and institutional-backing claims. That mismatch between a brand-new domain and the credibility the page projects is the central concern. The pairing of a protocol name with an unrelated word in the domain also warrants scrutiny. No explicit brand-impersonation or conflicting legal identities were established, so the risk rests on the blacklist and reputation evidence rather than on a proven copycat. On the homepage, the core action is depositing XRP into a bridged staking vault ahead of any service. The page advertises an increased deposit cap of 65 million FXRP and a 1.25x "claiming power" boost for voters. It cites unlinked audits by OpenZeppelin and Coinspect and a bug bounty, and it claims a "$2B" figure and "1,000+" stress-tested risk models, none of which is substantiated on the page. The source of the staking rewards and points is only loosely described. Behavioural testing found the page opening a wallet-connection modal and requesting a wallet signature for the vote. It also recorded several unrecognised third-party POST submissions, a high share of external traffic, and repeated console errors. Taken together, these make any wallet interaction on this domain a credible fund-loss or approval-abuse vector. Evidence:
- Domain registered on 2026-09-15 (about 0.1 years old), with only 2 web-archive snapshots, spanning 2026-09-15 to 2026-09-16.
- 14 security engines rate the domain malicious and 2 suspicious; two top-tier vendors are among them. A confirmed blacklist listing is in effect.
- The homepage requests an EVM wallet connection and a signature for the rewards vote, and makes 3 non-whitelisted external POST requests.
- The homepage claims audits, a bug bounty, a "$2B" figure and "1,000+" risk models without linking any supporting reports. The domain has no DeFiLlama listing.
Regulatory Verification Notes
The homepage names no legal entity, operator, jurisdiction, licence or registration number. Its only legal content is a broad disclaimer. The disclaimer says the site is informational, is not an offer or solicitation, and gives no professional advice. That wording sits uneasily beside prominent calls to stake and vote. The page attributes a quotation to a named co-founder of an affiliated firm but offers no verifiable link to that organisation. Identity cannot be independently tied to any real-world brand or person. Ownership and governance are opaque, which is an administrative and transparency concern and not an identity contradiction. No third-party broker-reputation record exists for the site, and the absence of regulatory standing is not itself evidence of fraud. Here, however, it compounds the reputation findings. Evidence:
- The homepage disclaimer is generic and identifies no operator or regulator.
- The registrar is NICENIC INTERNATIONAL GROUP CO., LIMITED, with registration running to 2027-09-15.
- The site is served from AS13335 (Cloudflare, US) with a DV TLS certificate from issuer YE2, valid to 2026-12-14.
- No licence claim, licence number or registry reference appears on the page.
What to Verify Next
Before any interaction, the protocol's genuine web address should be established independently, through its official social accounts or an established DeFi aggregator, and compared with this domain. The audit claims should be checked directly on the named auditors' own publications and the bounty claim on the bounty platform's own program listing. The claimed affiliation with the named backer should be confirmed through that organisation's own channels. Any wallet that has already connected to this site should have its token approvals reviewed and revoked. Evidence:
- The homepage links no audit report and no legal documentation.
- The homepage quotes a named co-founder of an affiliated firm without any verifiable link to that firm.
- The site requested wallet connection and signature during testing, so existing approvals are the immediate exposure.
Summary Verdict
The overall posture is elevated risk. Confirmed adverse reputation signals, a very new domain and an unverified operator behind a deposit-first yield product converge into a clearly negative assessment. Protective technical hygiene does not offset this, and the available evidence does not support treating the site as legitimate.
Infrastructure Integrity
The site sits entirely behind Cloudflare's CDN and WAF, and every observed address is a Cloudflare edge address. The origin server was not observable, so hosting cannot be independently attributed. The valid, mainstream-issued TLS certificate and reputable network provider are mitigating factors only. They protect traffic in transit and do not indicate that the operator is trustworthy. They cannot offset the external threat detections.
Closing Assessment
The domain should not be used for wallet connection, signing, staking or deposits, and no credentials or funds should be entrusted to it. Any interest in the protocol should be pursued only through an address confirmed independently of this site, and this domain should be treated as read-only at most.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of treasurys-firelight.finance.
- The request stayed on treasurys-firelight.finance. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-15. Noted
- The earliest public archive of this site is from 2026-09-15. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3036::ac43:dcf5 |
| Name servers | miles.ns.cloudflare.com, tia.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-12-14 |
| Domain age | 0.10 years (continuous registration) |
| Domain expiry | 2027-09-15 |
| Archive first seen | 2026-09-15 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 14 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about treasurys-firelight.finance at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.