Verdict
External threat listings named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
trias-one.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
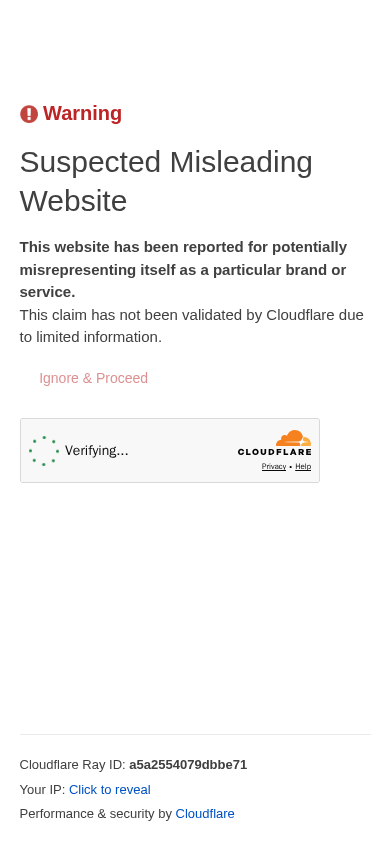
| How the site describes itself | Cloudflare interstitial warning that the requested site has been reported as possibly misrepresenting itself as a brand or service. Cloudflare states the claim is unvalidated, and the site's own content is not visible. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-25)). On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (70%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 10 marked it malicious, 1 suspiciousVirusTotal; Fortinet, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 2.5 years before captureWeb archive; a site on pages.dev has no registration of its own | Clear |
| Web archive | Archived since 202419 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 1 to 3 years before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
10 VirusTotal engines, including Fortinet, Sophos, marked this site as malicious; independent sources confirm a listing for this site.
Overview
This address is a project on Cloudflare's free pages.dev hosting platform, a subdomain that carries the label "trias-one" and has no domain registration of its own. The material read from its homepage was a warning notice. It contained no product, pricing, service or company description, so the site's purpose and business model could not be established from its own content.
Scam/Impersonation Risk
TrustSniffer rates the site as critical risk. A confirmed threat listing records this address as distributing phishing, and it was last seen on 25 October 2026. VirusTotal separately reported ten engines as malicious and one as suspicious, including Fortinet and Sophos. Two independent sources therefore agree, which is why the listing counts as confirmed. The site's own page says it "has been reported for potentially misrepresenting itself as a particular brand or service" and that Cloudflare has not validated the claim "due to limited information". That claim is a notice about the site and is not the basis of the finding. The listing and the engine detections carry the finding on their own. The address belongs to a free platform tenant and is not a brand's own domain, and the "pages.dev" part of the name is the platform's, not the operator's. The behaviour measured at capture adds weight. About 96% of the files loaded came from other domains, and 137 requests sent data to other hosts, 8 of them to destinations TrustSniffer does not recognise. The page also logged 18 console errors. Each of these is a scored finding, and together with the free-platform address they make up the score. No login or sensitive-data form was seen on the page.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Threat-intelligence listing, role: distributor of phishing, last seen 2026-10-25.
- VirusTotal: 10 malicious and 1 suspicious engine verdicts, including Fortinet and Sophos.
- Web archive: first seen 2024-04-30, with 19 snapshots through 2026-06-16 (a 777-day span, longest gap 362 days). The address was first seen about 928 days before capture and has no registration of its own.
- Homepage behaviour at capture: 137 data-sending requests to other hosts, 8 to unrecognised destinations, 96% of files from other domains, 18 console errors.
Regulatory Verification Notes
No licence, registration or regulatory standing was claimed or found, and no third-party regulatory match exists. Identity is unverified. The only identity-like label on the page read was the warning's own title, so it connects the site to no real-world person or organisation. A business of this type would be expected to publish contact channels and terms or privacy documents. On the pages read (the homepage only), neither was found. That is a disclosure gap on those pages and not a regulatory finding on its own. The missing disclosures matter here only because they leave no accountable operator to hold responsible alongside the confirmed listing. No broker-reputation match was found for this address.
- Homepage: no contact channels and no terms or privacy page found on the page read.
- Homepage: the only identity-style text was the warning title, "Suspected Misleading Website".
- Hosting: served from AS13335 (Cloudflare, Inc., US) through the pages.dev platform.
- Transport encryption: TLS certificate issued by WE1 (DV), valid to 2027-01-02, which establishes encryption only and says nothing about who runs the site.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "WE1" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site. "Valid to" is the date it expires.
What to Verify Next
Verification should focus on how the address was reached and on whether any brand is attached to it. If a message, advertisement or search result pointed here and implied a particular company or service, that claim should be checked only through the company's own official channels, found independently and not through anything on this site. Any representation that the site is licensed or affiliated with a known entity should be treated as unsupported until the named entity confirms it directly. The page offered no files, so there are no download steps to check.
- Homepage: the page offered a proceed-anyway button and no description of an operator, product or service.
- Homepage: no forms were seen, so there is no submission channel to test.
- Threat listing and engine detections: both tie the address itself to phishing.
Summary Verdict
The site sits in the critical-risk band. Confirmed external detections, a free-platform address with no identifiable operator and unrecognised data flows all point the same way. Its real-world identity remains unverified, and nothing observed supports a more favourable reading.
Infrastructure Integrity
The site is delivered through Cloudflare's network. All four observed addresses are Cloudflare edge servers, and no origin server address was observed. A check of the host address's abuse record found no reports. This is a neutral technical fact, and it neither supports nor weakens the findings above.
Closing Assessment
The address should not be used. The warning's proceed-anyway option should not be taken. If it arrived through an unsolicited message or advertisement, treat that source as suspect and report it. Any account or payment relationship with a brand the page seems to invoke should go through that brand's official channels reached independently.
Written analysis generated 2026-11-14 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
11 findings contributed to this verdict, raised by external reputation, page content, behaviour in a sandbox, and registration and ownership.
01 External reputation
- 10 VirusTotal engines marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page runs on a free hosting-platform address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_FREE_PLATFORM_ADDRESS - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
03 Behaviour in a sandbox
- Most of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
04 Registration and ownership
- As a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Third-party connections: 3 findings share one limit, because they all measure one fact: the page loads files from other hosts. The limit applied, so together they counted for less than their sum.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Suspected Misleading Website
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of trias-one.pages.dev.
- The request stayed on trias-one.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-04-30. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2f4e (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-02 |
| First seen (web archive) | 2.54 years before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2024-04-30 (2.5 years before capture) |
| Archive snapshots | 19 |
| Reputation | VirusTotal: 10 malicious, 1 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about trias-one.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.