Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
u-s-d-t-bep-2-0.onrender.com shows high-risk / scam indicators.
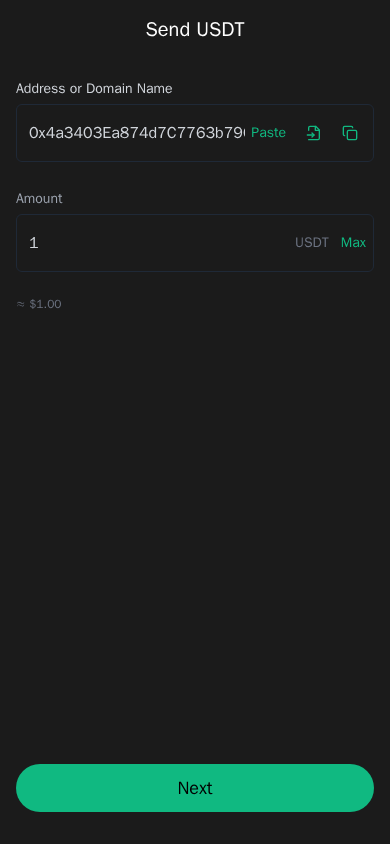
| What this site appears to be | A crypto wallet transfer form branded "Trust Wallet" that lets a user send USDT to an entered address or domain. The supplied content has no domain, legal identity, fee, or support information, so the high-stakes transaction cannot be verified. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 50% confidenceAbuseIPDB, 46 reports; shared hosting inflates reports | Risk |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | RENDERServer in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Scam/Impersonation Risk
Material contradictions were observed. Several independent threat-intelligence engines flag the domain as malicious, including at least one top-tier security vendor, and a confirmed blacklist listing applies to it. The hosting address has also drawn a large volume of recent abuse reports from many distinct reporters, the latest only a day before this assessment. Those reports attach to a shared hosting-provider address, so they say less about this operator specifically than the domain-level detections do. The detections are not discounted, however, and they reinforce each other. The page asks for a high-stakes financial action, sending USDT to a user-supplied address, under a well-known wallet brand, while offering nothing that ties it to that brand. The domain name is a hosting-platform subdomain built around "USDT" and a "BEP 2.0" label, which does not match how an established wallet provider would present itself. Page analysis did not confirm brand impersonation, and no conflicting legal identities exist because no legal pages exist. The brand-versus-hosting mismatch is still a claim-versus-evidence dissonance on a page that handles funds. The sandbox saw no wallet-drainer behaviour, no clipboard manipulation, no hidden forms and no external network posting. That absence does not offset the reputation findings, because a transfer form can redirect funds simply through the address a victim is induced to enter. Evidence:
- Homepage: a single crypto-transfer form (address or domain, amount, "Max", "Next") labelled "Transfer Trust Wallet", with only a few dozen characters of text and no meta description or page title beyond the form heading.
- Domain reputation: four security engines rate the domain malicious, one of them a top-tier vendor, and a confirmed blacklist entry applies to the domain itself.
- Hosting address: 46 abuse reports from 11 distinct reporters, with a confidence rating of 50 and the most recent report on 2026-10-19. The reports apply to a shared provider IP.
- Browser behaviour: three of three sandbox runs completed with zero external requests and zero wallet-drainer, clipboard-hijack or hidden-form indicators, but the page was flagged for a sensitive transaction form with no surrounding context.
Regulatory Verification Notes
The site offers no legal identity, registered entity, licence or registration number, no terms or privacy pages and no contact channel. For a service that moves digital assets, these omissions are a substantive disclosure gap. The gap is made more serious by the negative reputation findings. Ownership and governance are opaque: nothing on the page lets a visitor trace the operator or the party responsible for custody and fees. No third-party broker or regulatory-database match exists for this site, and none of the evidence indicates a regulated status. Transport encryption is present, but it is a basic domain-validated certificate. That confirms an encrypted connection and does not confirm who operates the site. Evidence:
- Homepage: no company name, licence authority, licence number, jurisdiction or fee and monetization information anywhere in the captured content.
- Transport encryption: TLS certificate issued by WE1 (domain-validated only), valid to 2026-12-20.
- Hosting: served from AS397273 (Render, US) in the ARIN registry region, on a shared application-hosting platform.
- Business-model assessment: classified as a high-risk exchange or wallet-type service with three red flags: unverifiable legal status, an evidence gap for a high-stakes action, and a mismatch between the claimed brand and the evidence.
What to Verify Next
Anyone who encountered this page should check the claimed brand against the genuine provider's official channels. These are the app-store listing or the provider's own documented website, reached by typing the address manually rather than by following a link. The operator's right to use the brand cannot be established from this page. Because the brand claim is unproven, no funds or wallet access should be committed until the operator is identified. Anyone who has already sent funds or interacted with the form should record the destination addresses and transaction identifiers. They should contact their exchange or wallet provider, and report the page to the hosting platform's abuse desk and to the brand owner. A confirmed licence number, if the operator ever publishes one, should be checked directly with the relevant financial regulator's public register, and official support channels should be confirmed through an independent route. Evidence:
- Homepage: the form accepts an arbitrary address or domain, so the recipient of any transfer is determined entirely by what the user enters, with no on-page confirmation or fee preview.
- Hosting: the site runs on a shared platform subdomain, so abuse complaints can be routed to the platform operator.
- Page content: no support, terms or privacy pages were found to cross-check.
Summary Verdict
The overall posture is clearly cautionary and high-risk. Blacklist-level external detections converge with an unattributable, unexplained funds-transfer page that uses a recognised wallet brand. The few positive technical signals, such as a valid certificate and clean sandbox behaviour, are routine and do not outweigh those findings. The site's real-world operator is unverified, so no legitimacy can be inferred.
Infrastructure Integrity
The site is hosted directly on a shared application-hosting platform (Render, AS397273, United States), with no separate CDN or WAF detected in front of it and two resolving addresses that look like origin servers. Addresses on this platform are shared with unrelated tenants, which explains part of the abuse-report volume. The platform's own reputation provides no mitigation here, because the domain-level detections are specific to this site and infrastructure protections cannot offset them.
Closing Assessment
The site should not be used for any login, wallet connection, credential entry or transfer of funds. At most it should be viewed passively, and any contact with the brand it claims should go through that brand's official channels.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by external reputation, page content.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH - The server address behind this site has a strong record of abuse reports.External reputation
rule:EXT_ABUSEIP_SEVERE
02 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN
Signals weighed against the site
- AbuseIPDB: 46 reports on hosting IP 216.24.57.16 (Render, Data Center/Web Hosting/Transit), 50% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of u-s-d-t-bep-2-0.onrender.com.
- The request stayed on u-s-d-t-bep-2-0.onrender.com. It was not redirected to another domain. Clear
- It is hosted on RENDER, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | RENDER - Render, US |
| Country | US |
| Server IP | 216.24.57.16 |
| Name servers | Not available |
| CDN / edge network | Not detected |
| Resolved IP addresses | 2 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 2 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-20 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 50% confidence, 46 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about u-s-d-t-bep-2-0.onrender.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.