Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
videosnw-ru.vercel.app shows high-risk / scam indicators.
| What this site appears to be | Russian-language page claiming access to a GLONASS/GPS video/protocol and instructing the user to download a file and enable installation from unknown sources. Behavior and wording strongly suggest distribution of an executable/installer with high risk of malware; lacks verification, contact details, or legitimate trust signals. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 7 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 72 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
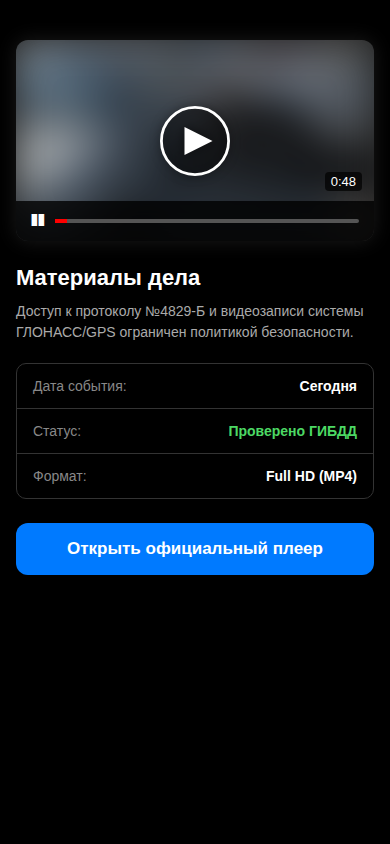
This website is a single-page, Russian-language download lure presented as a "Регистратор" (recorder) video viewer. It claims to give access to a restricted GLONASS/GPS video recording and a case protocol, described as a Full HD MP4 file, and it pushes the visitor to open an "official player" and install a roughly 2.4 MB file. It shows no product, pricing, company or service. Its apparent purpose is to get visitors to download and run an installer, not to sell or publish anything.
Scam/Impersonation Risk
The evidence converges on a high-risk, malware-distribution pattern. Several independent security engines currently flag the site as malicious, and it is blacklisted on external reputation lists. Page analysis independently rates the content as high risk and as an executable-delivery page. The homepage walks the visitor through a social-engineering sequence. It tells the visitor to accept the download, click "Download anyway" if the browser warns, open the file, and then enable installation "from this source" in the device settings. That sequence is designed to defeat built-in platform protections. The page also invents official authority. It cites a numbered protocol, the status "Verified by traffic police", an event date of "Today" and restricted access "by security policy". None of these claims is supported by any verifiable source, and the page offers no explanation of what the file actually does. This is a bait-and-install design that pressures the visitor with urgency and official-sounding language. No brand impersonation and no conflicting legal identities were detected. The risk comes from the blacklisting and the delivery mechanics, not from identity contradictions.
- Homepage: step-by-step instructions to bypass download warnings and enable unknown-source installation, with a "download file again" button and a 2.4 MB recording labelled as a video.
- Homepage: unverifiable claims of police verification and a restricted protocol (No. 4829-Б), with no issuing body, contact or reference given.
- External reputation: multiple major security engines flag the domain as malicious, and it appears on external blacklists.
- Page behaviour analysis: flags for prompted downloads, unknown-sources installation instructions and executable installer delivery.
Regulatory Verification Notes
The site discloses nothing on any page that could support a legal or regulatory assessment. It names no operating company, registration number, licence, physical address, terms of use, privacy policy or support channel, so both ownership and governance are opaque. Content that claims to originate from a state traffic authority would be expected to carry a verifiable institutional source, and none appears. No third-party broker or regulatory-database record was matched for the site. No licensing claim is made, so there is nothing to validate. In this case the disclosure gap supports the cautionary reading rather than standing alone as a finding. Neither the hosting nor the encryption provides any evidence of the operator's identity.
- Homepage: no company name, address, licence, legal pages or contact details in the visible content.
- Hosting: served from AS16509 (AMAZON-02 – Amazon.com, Inc., US), as a subdomain of a shared application-hosting platform.
- Transport encryption: TLS certificate issued by WR1 (domain-validated, DV), valid to 2026-11-27; domain validation confirms control of the domain only, not who operates it.
- Identity: the site is not independently linked to any real-world brand or person.
What to Verify Next
Because the page's intent is installer delivery, verification should concern containment, not engagement. Any claim about an official traffic-police video or protocol should be checked only through the relevant authority's own published channels, reached independently of this site. Any person who has already opened, downloaded or installed the file should treat that device as potentially compromised. This means removing the file, revoking the unknown-sources permission, running a full scan with a reputable security product, and changing credentials from a clean device. Organisations should also check whether the domain or the file appears in their web-proxy, email or endpoint logs.
- Homepage: the only action requested is to download and install a file, so no legitimate content is available to evaluate.
- Homepage: the instructions require disabling a device protection, which makes the downloaded file the key item to check.
- Site contents: no official support or contact channel is published on the page, so independent routes must be used.
Summary Verdict
The site is assessed as high-risk and untrustworthy. Confirmed external blacklisting and the strong content indicators of installer-based malware delivery outweigh every neutral technical attribute. The posture is clearly cautionary, and no legitimate use for the site is apparent.
Infrastructure Integrity
The site is served through a shared application-hosting platform behind Cloudflare CDN/WAF, with edge addresses on both Cloudflare and Amazon-based ranges. This protective layer is only a mitigating factor and does not offset the reputation findings. A sizeable number of abuse reports attach to the shared platform address. They apply to the provider's multi-tenant infrastructure, not to this site specifically, so they are discounted and carry no weight in this assessment. The sandbox session showed no external requests, no hidden forms and no wallet or clipboard activity. This shows the harm lies in the downloaded file, not in the page's runtime behaviour.
Closing Assessment
The site should not be visited for any purpose beyond analysis, and nothing should be downloaded, opened or installed from it. Security teams should consider blocking the domain and warning anyone who may have received a link to it. Anyone who has already installed the file should isolate the device and begin remediation immediately.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Signals weighed against the site
- AbuseIPDB: 72 reports on hosting IP 216.198.79.3 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of videosnw-ru.vercel.app.
- The request stayed on videosnw-ru.vercel.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 216.198.79.3 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 7 flagged | AbuseIPDB: 0% confidence, 72 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about videosnw-ru.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.