Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
web-node-7931-oye24wry1-deployment-access1.vercel.app is low-trust and potentially risky.
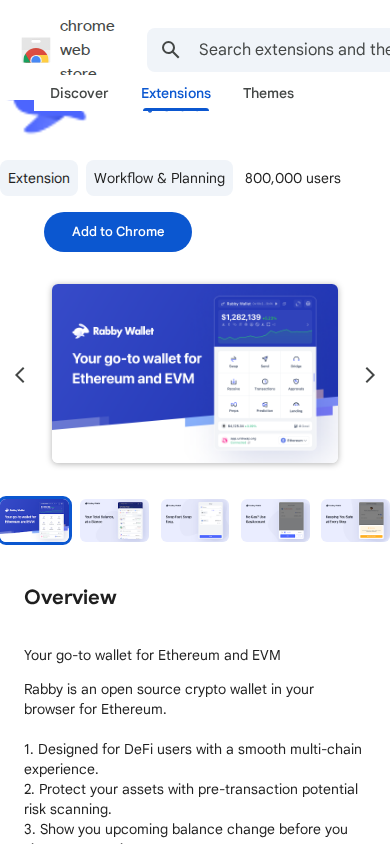
| What this site appears to be | Official-looking Chrome Web Store listing for Rabby Wallet, an open-source Ethereum/EVM browser wallet described as offering pre-transaction risk scanning and balance-change previews. It shows a publisher linked to rabby.io, about 800,000 users, and disclosed data-use limits, with no login or payment form in the captured content. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 103 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
This website is a single-page replica of a Chrome Web Store listing for Rabby Wallet, an open-source, non-custodial Ethereum/EVM browser wallet. It sits on a temporary-looking Vercel deployment subdomain rather than the official extension store. The page shows the wallet's marketing copy: multi-chain DeFi support, pre-transaction risk scanning, balance-change previews before signing, a 4.0 rating from about 2,800 reviews, roughly 800,000 users and an "Add to Chrome" button. It states no monetization model. Its apparent purpose is to steer visitors toward installing a crypto wallet extension.
Scam/Impersonation Risk
Confirmed contradictory signals are present. The deployment's reputation screening returned a malicious and a suspicious detection from the reputation engines, which constitutes a blacklist hit. No phishing verdict, Safe Browsing listing or conflicting legal identities were recorded. The pattern is a well-known fraud archetype: a trusted-brand storefront (a browser-store page for a widely used wallet) hosted on a disposable-looking, auto-generated hosting subdomain that the official publisher would not use. For a wallet product the main danger is substitution. The page's install button, or a later content swap, could point visitors to a tampered extension that captures seed phrases or signs malicious transactions, and a convincing copy of a real listing is exactly what makes that effective. The page also carries a strong typo-style lookalike resemblance to its hosting platform's domain, which fed a brand-suspicion penalty. The sandbox found no wallet-drainer behavior, clipboard hijacking, hidden forms, cloaking or password-collecting forms across three runs, and the page requests no credentials or payment. These observations lower the likelihood of an active credential trap on the captured page, but they do not offset the blacklist hit or the questionable hosting context. A large volume of abuse reports exists against one of the shared edge addresses, but they belong to the platform provider's multi-tenant infrastructure and have been discounted as not specific to this site. Evidence:
- Homepage: reputation screening shows one malicious and one suspicious detection against this deployment, alongside a clean Safe Browsing result.
- Homepage: Chrome Web Store layout, Rabby branding, a publisher badge and an "Add to Chrome" button are served from a generic, auto-generated Vercel subdomain.
- Homepage: no login form, payment form, hidden form or wallet-connect prompt was captured, and no drainer or clipboard-write behavior occurred in any sandbox run.
- Shared edge address: 103 abuse reports are attributed to the CDN provider's shared infrastructure and are treated as non-specific to this site.
Regulatory Verification Notes
The captured page contains no legal, terms, about or company pages, and it names no licensing authority or registration number. The listing's developer section shows a contact mailbox on the wallet project's own domain, a "non-trader" declaration, and privacy disclosures, but these are copied storefront content and do not tie the deployment to the actual publisher. Registration details for the deployment are incomplete, which amounts to ownership opacity and governance opacity. These are administrative limitations and do not by themselves indicate wrongdoing, but they leave the operator unidentified. No third-party broker or regulatory-database match exists for this site. Wallet software is not normally a licensed financial service, so the absence of a license is a disclosure gap and not a contradiction. Evidence:
- Homepage: the listing's developer panel carries a "non-trader" statement and privacy disclosures, but no legal entity name, address or registration number.
- Hosting infrastructure: served from AS16509 (AMAZON-02 - Amazon.com, Inc., US) in the United States.
- Transport encryption: TLS certificate issued by WR1 at DV (domain-validated) level, valid to 2026-11-27 with 37 days remaining.
- Third-party broker dataset: no match for this site.
What to Verify Next
The wallet should be obtained only through the official extension store or the wallet project's own website, reached by typing the address manually or via a bookmark, never through this deployment. Anyone who has already followed this page's install button should check which extension identifier was installed and compare it with the one published by the project on its official channels. The publisher's contact channels should be confirmed through an independent route before any correspondence. Anyone who has interacted with this deployment with a wallet connected should review and revoke token approvals. Evidence:
- Homepage: the page presents publisher and install elements that can be reproduced by anyone and cannot be relied on as provenance.
- Homepage: the listing advertises version and update details that can be cross-checked against the project's official release channels.
- Homepage: the listing's developer contact is on the wallet project's own domain, which makes an independent confirmation route available.
Summary Verdict
Available evidence supports a clearly cautionary posture. A confirmed blacklist hit and a replica of a trusted brand's storefront on an unrelated hosting subdomain outweigh the otherwise benign page behavior. The operator's identity remains unverified, and sensitive interactions, such as logins, credential entry, wallet connections and financial transactions, are unsupported by the evidence.
Infrastructure Integrity
The site is delivered through a mainstream, trusted cloud edge network in the United States, and all six observed addresses are edge nodes; the origin server was not observable. This is a mitigating factor only. Edge-only visibility prevents independent verification of the true hosting origin and allows content to be swapped quickly behind an unchanged address, so it cannot offset the reputation findings.
Closing Assessment
Read-only viewing is the most this site supports. Nothing should be installed from it, no wallet should be connected, and no credentials or funds should be entered until the official publisher independently confirms that this address belongs to it.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, page content, registration and ownership, behaviour in a sandbox.
01 External reputation
- A small number of malware engines flagged this domain. On its own this is a weak signal.External reputation
rule:EXT_BLACKLIST_MEDIUM
02 Page content
- The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
04 Behaviour in a sandbox
- The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
Signals weighed against the site
- AbuseIPDB: 103 reports on hosting IP 216.198.79.195 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of web-node-7931-oye24wry1-deployment-access1.vercel.app.
- The request stayed on web-node-7931-oye24wry1-deployment-access1.vercel.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 216.198.79.195 |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 0% confidence, 103 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about web-node-7931-oye24wry1-deployment-access1.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.