Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
xrpaynet.live shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 16 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Listed as unsafeGoogle | Risk |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 4 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
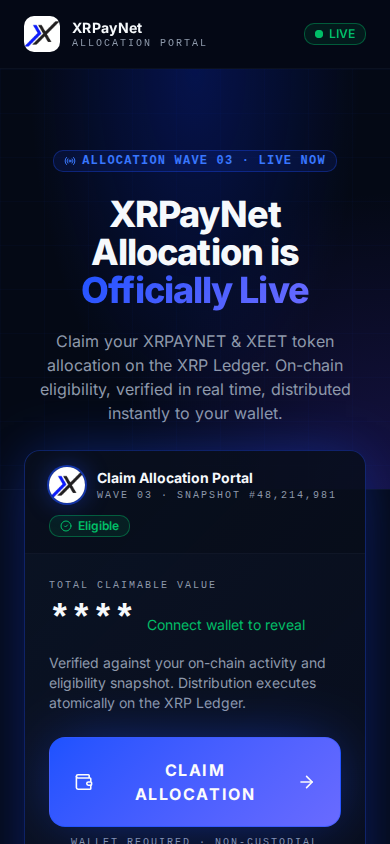
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Google, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a single-page landing site on the domain xrpaynet.live. Its page is titled "XRPayNet Allocation Live — Claim Your Tokens Now" and urges visitors to claim a token allocation. The name evokes the XRP and payments ecosystem, but the captured page shows no demonstrated affiliation with any established project. Its apparent purpose is to funnel visitors into a token-claim flow. No product, company, or business model is described, and that gives the site the profile of a promotional lure rather than an operating service.
Scam/Impersonation Risk
Contradictory signals are present, and they are severe. The site is blacklisted. A major browser-safety service classifies it under social engineering, and a large number of independent security engines, including several top-tier vendors, flag it as malicious. Together these triggered an automatic reputation ceiling that overrides every positive technical signal. This cannot be read as a mere reputational concern, because the detections come from several independent sources. No conflicting legal identities were found, and no confirmed impersonation of a specific named brand was established. The risk comes from the blacklist convergence combined with the "claim your tokens now" call to action, a framing typical of token-giveaway and wallet-solicitation lures. Behavioural testing of the homepage points the same way. Across all three sandbox runs, hidden forms were present, including password-type fields that a visitor cannot see. The page sent a large volume of background data to many third-party destinations that are not established infrastructure. Nearly all of its outbound traffic went to external parties. Its content also changed substantially after interaction, which is consistent with a page that assembles its real behaviour dynamically. Wallet-connection prompts, clipboard tampering, drainer behaviour, and cloaking were not observed in testing. That is an observation of the test runs only and does not offset the blacklist evidence. Evidence:
- Homepage: the title and call to action solicit a token allocation claim, with no accompanying description of the issuer or the project.
- Homepage behaviour: hidden forms, including hidden password fields, were detected in 3 of 3 sandbox runs. 12 external POST requests and 17 external XHR requests went to non-whitelisted destinations, and about 3,184 DOM mutations followed interaction.
- Domain provenance: registered 2026-07-09 (~0.3 years old, roughly 106 days). The web archive holds 1 snapshot, first seen 2026-07-12, with 1 year tracked, so the site has no history of legitimate operation.
- Reputation: the browser-safety classification and the multi-vendor malicious detections were both confirmed on the scanned domain.
Regulatory Verification Notes
The captured page makes no verifiable regulatory claim. It shows no licence, registered company, or named operator. Whether any on-page disclosure exists remains unclear. Ownership is opaque, and the registrant details are incomplete. A site that solicits token claims and asks for sensitive input normally carries identifiable corporate and compliance information, so this absence matters here. Taken alone, a missing licence is only a verification gap. In this case it adds to, and does not cause, the elevated risk assessment. No third-party broker or regulator record matched this domain, and that finding is neutral rather than reassuring. The domain is also not recognised in DeFi protocol-tracking directories, so it has no independent footprint as an established crypto project. Evidence:
- Registration: the domain is held through the registrar NICENIC International Group Co., Limited, with expiry set to 2027-07-09. Registrant detail is incomplete.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: the TLS certificate is issued by WE1 at DV (domain-validation) level only and is valid to 2026-12-05. It confirms domain control, not the operator's identity.
- Directory recognition: the DeFi tracking lookup completed and returned no listing for this domain.
What to Verify Next
No interaction with the site is advisable. Anyone who believes an "XRPayNet" allocation is genuine should consult the project's announcements through channels reached independently of this site, for example by looking up the project through known, established sources rather than any link or message that led here. Anyone who has already visited the page should not have entered credentials, seed phrases, or payment details. If they did, they should change the affected passwords from a clean device, revoke any wallet permissions granted, and monitor the wallet and associated accounts. Any claimed licence or registration should be checked directly with the relevant regulator's public register. The check should use the regulator's own website and a name found there, not details supplied by this site. Anyone who encountered the domain through a message, advertisement, or social post should report that message to the platform on which it appeared. Evidence:
- Homepage: the token-claim call to action is the only functional element observed, so legitimacy depends entirely on what an independent source says about the project.
- Behavioural testing: hidden password-type fields were found, so any credential entered on the page is at risk even though it is not visibly requested.
- Reputation: the confirmed browser-safety and multi-vendor detections give a security basis for reporting the domain to the platform on which it was found.
Summary Verdict
The assessment is firmly adverse. Confirmed multi-source threat detections, young and unestablished provenance, and concealed form behaviour converge on a site that should be treated as hostile to visitors' interests until independent evidence shows otherwise. Whatever limited technical hygiene it displays does not alter that conclusion, and the real-world operator remains unidentified.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and WAF, and all four observed IP addresses are Cloudflare edge servers. The origin server was not observable. A valid TLS certificate from a mainstream issuer is in place. These protections are a mitigating factor only. They are available to any customer, including malicious operators, and they cannot offset the external threat detections. Edge-only visibility also prevents independent verification of the hosting and allows content to be swapped quickly without any visible infrastructure change.
Closing Assessment
Do not enter credentials, wallet details, seed phrases, or payment information on this site, and do not connect a wallet or approve any transaction from it. Anyone who has already done so should act on the remediation steps above promptly.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, history in the web archive, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- The page contained a form a visitor cannot see.Behaviour in a sandbox
rule:BEHAV_HIDDEN_FORMS - The page replaced a large part of its own content after loading.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of xrpaynet.live.
- The request stayed on xrpaynet.live. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-07-09. Noted
- The earliest public archive of this site is from 2026-07-12. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3030::ac43:a07b |
| Name servers | alfred.ns.cloudflare.com, deborah.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-05 |
| Domain age | 0.30 years (continuous registration) |
| Domain expiry | 2027-07-09 |
| Archive first seen | 2026-07-12 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 16 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 1 match |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about xrpaynet.live at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.