Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
zcat.meme shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 8 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 2.5 years oldRegistered history | Clear |
| Web archive | Archived since 20242 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
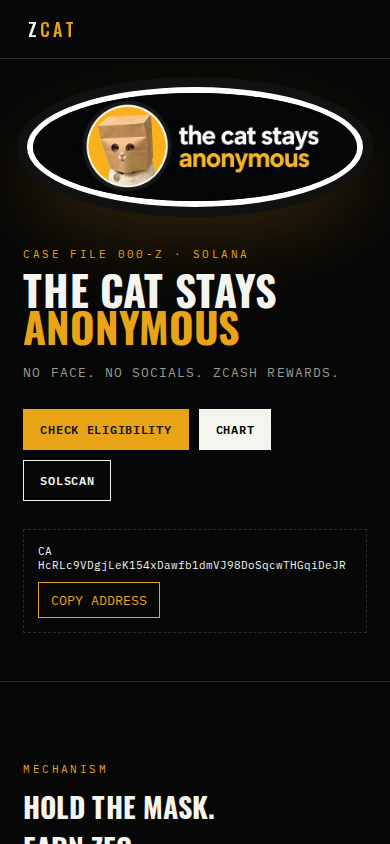
ZCAT is a single-page, meme-themed website titled "ZCAT — Anonymous Cat" on the .meme top-level domain. It presents a short block of promotional text under a playful, pseudonymous brand and appears to serve as the landing page of a meme-token or online-community project. Its commercial purpose could not be established from the captured content, and no independent link to a named real-world operator was confirmed.
Scam/Impersonation Risk
This is the decisive area of the assessment. The site is blacklisted: multiple independent security engines flag the domain as malicious, and one of them is a major endpoint-security vendor. The detections are not accompanied by a specific threat category, so the exact nature of the abuse (malware, phishing or another form) is unconfirmed. The breadth and severity of the flags, however, make them a confirmed adverse reputation signal rather than an isolated false positive. No conflicting legal identities and no brand-impersonation findings were observed, and the behavioural sandbox did not detect wallet-connection prompts, wallet-drainer behaviour, hidden forms, credential posts to external hosts or cloaking. These clean behavioural results do not offset the reputation hits. The site makes frequent calls to third-party hosts, but none of them were to non-whitelisted destinations. Its recently re-registered footing and the meme-token context are typical of short-lived campaigns, and that context raises the stakes for any visitor asked to connect a wallet or send funds. Evidence:
- Homepage and domain reputation: several independent security engines classify the domain as malicious, including one major endpoint-security vendor, and a confirmed blacklist hit is recorded.
- Homepage behaviour: in three sandbox sessions, 4 external XHR calls and 2 external POST requests were made, all to whitelisted destinations. No wallet-provider interaction, drainer activity or password-form exfiltration was detected. A clipboard write was observed, with no hijack behaviour.
- Domain provenance: the current registration was created on 2026-09-08 (~44 days old). The web archive holds only 2 sparse snapshots, from 2024-04-29 to 2026-09-17 (3 years tracked), so the site has no meaningful continuous operating history.
Regulatory Verification Notes
The captured page, which holds roughly 1,400 characters of text, presents no licence, regulated-entity claim, legal terms or company identification. Identity could not be independently tied to a real-world person or brand, and ownership is opaque: registrant details are incomplete. This is an ownership-opacity matter rather than an identity contradiction. No third-party broker or regulatory-database record matched the site, so no external regulatory standing, positive or negative, is established. The missing licensing and legal disclosure is a verification gap, but in this case it compounds an already severe reputation problem. It would not be an accusation on its own. Evidence:
- Registration: domain registered through Dynadot LLC., created 2026-09-08, expiring 2027-09-08.
- Transport security: TLS certificate issued by WE1 (DV, domain validation only), valid to 2026-12-07 with about 45 days remaining. DV certificates confirm domain control, not organisational identity.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Homepage: no company name, licence number, terms page or privacy policy was visible in the captured content.
What to Verify Next
Any engagement should begin with independent confirmation of who operates the project and whether it is a genuine undertaking. That means checking for an official announcement through channels that are not reached via this domain, and confirming that any token, contract or social account referenced by the site matches what the project's own verified channels publish. Official support and contact routes should be confirmed through an independent route. Because the underlying detection category is unspecified, the security engines' own reports on the domain should be reviewed before anything is downloaded or any wallet is connected. Evidence:
- Homepage: the site gives no verifiable operator, team or registry reference to check against.
- Domain history: the sparse archive and the recent registration date offer no long-standing record that could corroborate the project's claims.
- Reputation: the unspecified threat classification means the nature of the abuse cannot be ruled in or out without consulting the detecting engines' own reports.
Summary Verdict
The overall posture is one of high risk. Confirmed adverse detections, a brief and thin operating record, and an unverified, opaque operator outweigh the technically sound transport configuration and the benign sandbox behaviour. The site should be treated as an unsafe counterparty until its reputation is cleared.
Infrastructure Integrity
The site sits behind the Cloudflare CDN and WAF. All four observed addresses are edge servers, and the origin host is not visible. This is a mitigating factor only: it shows the site is not on obviously disreputable hosting, but edge-only visibility prevents independent verification of the underlying host and can mask rapid content changes. The protection therefore cannot offset the adverse reputation findings.
Closing Assessment
Limit any interaction to passive, read-only viewing, preferably from an isolated environment. Do not sign in, submit credentials, connect a wallet, make any financial commitment or download files from the site unless its security reputation is cleared and the operator is independently verified.
Written analysis generated 2026-10-22 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of zcat.meme.
- The request stayed on zcat.meme. It was not redirected to another domain. Clear
- Registration is published under Dynadot LLC.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-08. Noted
- The earliest public archive of this site is from 2024-04-29. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Dynadot LLC. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3030::6815:14ca |
| Name servers | luke.ns.cloudflare.com, pola.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-07 |
| Domain age | 2.48 years (continuous registration) |
| Domain expiry | 2027-09-08 |
| Archive first seen | 2024-04-29 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 8 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about zcat.meme at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.