Verdict
135461223.site shows high-risk / scam indicators.
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
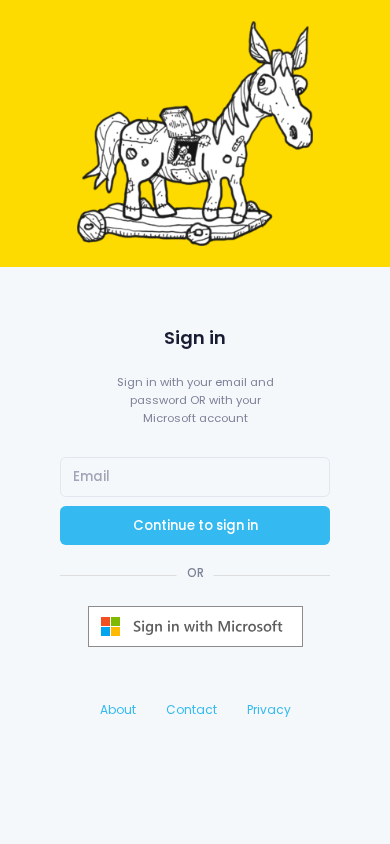
| What this site appears to be | A sign-in page for Nimblr Security Awareness offering email or Microsoft account login and a demo booking link. The page contains minimal explanatory content and lacks public pricing, legal, or contact details beyond basic links. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 13 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0 reportsAbuseIPDB; shared hosting inflates this count | Noted |
| Domain age | 6.3 years oldRegistered history | Clear |
| Web archive | Archived since 202163 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 3 to 10 years (registration continuity).
- Public web-archive history exists since 2021.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a login-only portal presenting itself as “Nimblr Security Awareness,” with email/password or Microsoft-account sign-in, links for About, Contact, and Privacy, and an invitation to book a 30-minute demonstration for an “intelligent simulation and training” service.
Scam/Impersonation Risk
Confirmed contradictory reputation signals create a critical risk to sensitive interaction. External security assessments identify malicious activity associated with the website, and the site is confirmed as blacklisted by multiple sources. The public page also provides only minimal context around a credential-collection workflow, making it insufficient to establish that the sign-in service is operated by the claimed security-awareness business. No separate identity inconsistency or brand-impersonation finding was recorded, but those points do not offset the confirmed blacklist and malicious-detection signals.
- External reputation assessment recorded 13 malicious detections from 18 effective evaluations, with threat detections from Fortinet, Kaspersky, and Sophos.
- The website was identified on a confirmed blacklist, with blacklist status reported by two sources.
- Domain registration telemetry records registration on 2020-04-30 and an age of 6.3 years through the 2027-04-30 expiry.
- Archive telemetry records 63 snapshots from 2021-11-23 through 2026-07-10, spanning 6 tracked years.
Regulatory Verification Notes
The public-facing material does not establish a clear legal operator, pricing model, payment process, or applicable licensing position. The presence of About, Contact, and Privacy links is not equivalent to a complete corporate or regulatory disclosure. The operator identity remains unverified, and any security-awareness or training claims should therefore be treated as unsubstantiated pending independent confirmation. Transport encryption is present, but domain-validated TLS confirms encrypted communication rather than the identity or legitimacy of the operator. No regulated-broker match was identified in the available third-party context.
- The public login page contains approximately 283 characters of explanatory text and provides no visible pricing, legal-entity, or payment-processing disclosure.
- Hosting telemetry identifies HETZNER-AS — Hetzner Online GmbH, Germany, on AS24940.
- The site uses a valid DV TLS certificate issued by YR1, valid through 2026-11-09T14:38:01+00:00.
- The business-model content contains no claimed license authority or license number.
What to Verify Next
Before any credential submission, the purported operator should be identified through an independently sourced corporate website or offline business contact, and any applicable training-provider or software-service registration should be checked with the relevant official registry. The sign-in destination and Microsoft-account flow should be confirmed through a known, independently obtained channel rather than through the reviewed page. Until those checks succeed, the appropriate posture is to avoid login, credential transfer, financial activity, downloads, or installation of software associated with the site.
- The public page is classified as “Login-only / Unknown,” with one sensitive login form and limited explanatory context.
- The page itself offers a demo-booking route but does not provide sufficient public information to validate the service or its operator.
- Independent confirmation is required because identity verification is currently unverified and the external reputation assessment contains confirmed malicious and blacklist indicators.
Summary Verdict
The website has a critical trust posture and presents unacceptable exposure for credentialed or other sensitive interaction. Its apparent business purpose cannot be treated as authenticated, and the available evidence supports restricting engagement to non-interactive observation while independent validation is pending.
Infrastructure Integrity
The website is protected by a CDN/WAF, and the observed address belongs to an edge server rather than a confirmed origin; this reduces direct origin exposure but can also limit independent hosting verification. The protective infrastructure is a mitigating technical control only and does not overcome the external reputation findings.
Closing Assessment
Enterprise users should suspend sensitive interaction with the site and escalate any intended engagement for independent identity, security, and registry validation before proceeding.
Written analysis generated 2026-08-18 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by registration and ownership, page content, analysis engine, behaviour in a sandbox, external reputation.
01 Governance Risk
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED
02 Sensitive Interaction Risk
- The analysis matched a pattern TrustSniffer treats as a direct threat to a visitor.Analysis engine
signal:direct_threat - A sign-in path on this site handles sensitive information.Page content
rule:PAGE_LOGIN_PATH_SENSITIVE - The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of 135461223.site.
- The request stayed on 135461223.site. It was not redirected to another domain. Clear
- Registration is published under Abion AB. Clear
- DNS for this domain is served by portsdns.se, across 2 name servers. Noted
- The registration is paid up to 2027-04-30. Noted
- The earliest public archive of this site is from 2021-11-23. Clear
- It is hosted on HETZNER-AS, from a server in DE. Noted
Domain intelligence
| Registrar | Abion AB |
|---|---|
| Hosting | HETZNER-AS - Hetzner Online GmbH, DE |
| Country | DE |
| Server IP | 116.203.212.240 |
| Name servers | a.portsdns.se, b.portsdns.net |
| SSL issuer | YR1 |
| SSL expiry | 2026-11-09 |
| Domain age | 6.30 years (continuous registration) |
| Domain expiry | 2027-04-30 |
| Archive first seen | 2021-11-23 |
| Archive snapshots | 63 |
| Reputation | VirusTotal: 13 flagged | AbuseIPDB: 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about 135461223.site at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.