Verdict
amaamn.com shows high-risk / scam indicators.
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
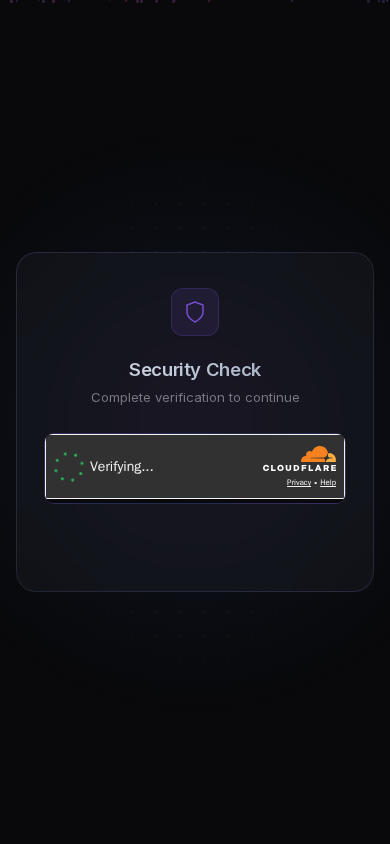
| What this site appears to be | A short verification/bot-check interstitial asking the user to enable JavaScript to continue. No forms, links, or business content are present. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 13 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0 reportsAbuseIPDB; shared hosting inflates this count | Noted |
| Domain age | 4 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 2026Public history exists | Clear |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website is a minimal verification interstitial that presents a “Security Check” and asks visitors to enable JavaScript before continuing. It exposes no visible products, services, business information, contact channel, or transaction functionality, so its apparent purpose is limited to gating access through an anti-bot challenge rather than presenting an identifiable operating business.
Scam/Impersonation Risk
The site presents a critical interaction risk because external security intelligence recorded 13 malicious detections and one suspicious detection, and the domain is present on confirmed blacklist sources. These findings outweigh the otherwise neutral page-level presentation. No brand impersonation, phishing form, conflicting legal identity, or sensitive input form was observed; however, the available page is too limited to establish what content would appear after the verification step. No contradictions were observed in the page’s stated identity itself, but the external malicious detections and blacklist status are material contradictions to safe engagement.
- External security scanning recorded 13 malicious and 1 suspicious detections for the assessed domain.
- The domain was identified by two external blacklist sources.
- The homepage displayed only “Complete verification to continue” and contained no forms, links, or business content.
- Browser analysis recorded six external XHR requests, two external POST requests, and four console errors during two successful runs.
Regulatory Verification Notes
The site provides no accessible legal, privacy, terms, licensing, registration, address, telephone, or contact-form information. This is a regulatory and identity-verification gap rather than independent proof of fraud. The supplied on-chain intelligence independently recognizes amaamn.com as a registered DeFi protocol, but it does not provide a protocol category or a total-value-locked, market-capitalization, or trading-volume figure; that recognition therefore supplies useful legitimacy context without establishing the operator’s identity or regulatory status. The available identity evidence remains apparent rather than independently verified.
- The homepage’s only displayed identity text was “Verifying…,” with the heading “Security Check.”
- No privacy page, terms page, policy page, email, telephone number, physical address, or contact form was captured.
- Domain registration records identify Realtime Register B.V. as registrar; registration date is 2026-05-20 and the recorded age is approximately 0.33 years.
- TLS uses issuer YR2 with DV validation and is valid through 2026-12-09.
What to Verify Next
Before any sensitive interaction, an institution should independently confirm whether the domain is the intended official address for the recognized protocol, validate any claimed operating entity and authorization directly through the relevant jurisdictional register, and obtain business and support details through an independently sourced channel. Any later page that requests credentials, wallet approval, downloads, or financial transfers should be assessed separately rather than treated as a continuation of the present verification screen.
- The captured homepage did not expose an operating entity, licensing claim, or contact route to corroborate independently.
- The page requested JavaScript completion but did not reveal the destination or service behind the challenge.
- The external security record contains confirmed blacklist and malicious-detection findings that require independent resolution before sensitive use.
Summary Verdict
The website should be treated as an elevated-risk, sensitive-interaction environment, not as a trustworthy destination for credentials, account access, or financial activity. Independent recognition of amaamn.com as a DeFi protocol is a meaningful legitimacy signal, but the supplied record provides no category or financial-scale metric and does not reconcile that recognition with the assessed site’s minimal verification page. The confirmed external malicious detections and blacklist status remain decisive.
Infrastructure Integrity
The site is protected by Cloudflare CDN/WAF infrastructure, and the observed address is an edge address rather than an independently exposed origin. This provides a defensive layer against direct infrastructure exposure but does not offset the site’s external reputation findings or establish operator legitimacy.
Closing Assessment
Sensitive interaction should be withheld unless the domain, operating entity, authorization, and post-verification destination are independently confirmed through trusted channels. Any engagement should remain limited to non-sensitive observation until those checks produce a consistent result.
Written analysis generated 2026-09-17 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by registration and ownership, analysis engine, behaviour in a sandbox, external reputation.
01 Governance Risk
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
02 Sensitive Interaction Risk
- The analysis matched a pattern TrustSniffer treats as a direct threat to a visitor.Analysis engine
signal:direct_threat - Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
Identity verification
| Status | LIKELY |
|---|---|
| Identity score | 70/100 |
| Identity verification confidence | 72% |
- org:Verifying
- on_site_identity
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of amaamn.com.
- The request for amaamn.com ended on notvelo.com, a different domain. Watch
- Registration is published under Realtime Register B.V.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-05-20. Noted
- The earliest public archive of this site is from 2026-07-03. Clear
- It is hosted on AEZA-AS, from a server in RU. Noted
Domain intelligence
| Registrar | Realtime Register B.V. |
|---|---|
| Hosting | AEZA-AS - AEZA GROUP LLC, RU |
| Country | RU |
| Server IP | 185.104.151.130 |
| Name servers | KIRA.NS.CLOUDFLARE.COM, ROCCO.NS.CLOUDFLARE.COM |
| SSL issuer | YR2 |
| SSL expiry | 2026-12-09 |
| Domain age | 0.33 years (continuous registration) |
| Domain expiry | 2027-05-20 |
| Archive first seen | 2026-07-03 |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 13 flagged | AbuseIPDB: 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about amaamn.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.