Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
bookmark-plum-zeta.vercel.app shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 91 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
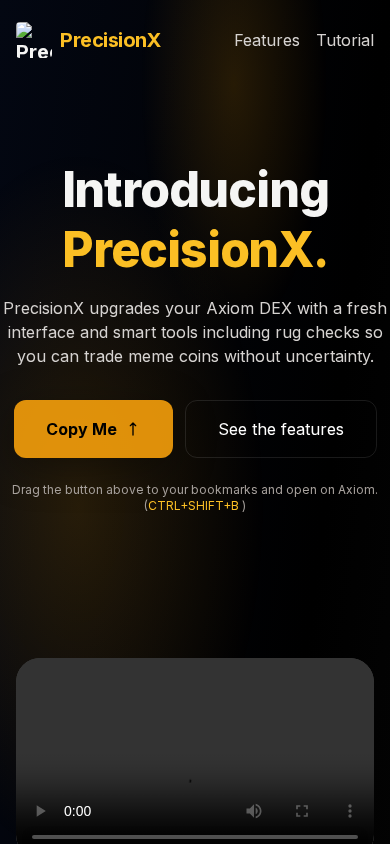
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
PrecisionX is a single-page website published as a subdomain on a shared application-hosting platform, not on a domain of its own. Its homepage carries a short block of text under the title "PrecisionX". The evidence reviewed does not establish a defined product, service or business model. Any commercial purpose is therefore unconfirmed.
Scam/Impersonation Risk
This site shows confirmed contradictory signals and is assessed as high risk. Several independent threat-detection sources flag the site as malicious or suspicious. It also sits on an external blacklist, and this reputational finding is decisive. Brand impersonation was not detected, nor were conflicting legal identities or on-page phishing mechanics. The risk therefore rests on the blacklist and detection findings, not on identified deception in the page content. Behavioural testing was uneventful. Three sandbox sessions completed without any outbound third-party requests, wallet-connection prompts, clipboard manipulation, hidden forms or credential posts to external destinations. This lowers the likelihood of active drive-by exploitation, but it does not offset the external detections. A large volume of abuse reports exists against the shared hosting address the site resolves to, and the most recent report is very recent. Those reports are attributed to shared provider infrastructure rather than to this site specifically, so they are treated as context and not as evidence against the operator. The site's own blacklist and detection findings stand independently of them. Evidence:
- Homepage and domain-level reputation: multiple security engines classify the domain as malicious or suspicious, and an external blacklist listing is present.
- Homepage behavioural sandbox: three successful runs with zero external requests, no wallet, clipboard or hidden-form activity, and three console errors.
- Hosting address: 91 abuse reports are recorded against the shared platform address (64.29.17.195), attributed to shared infrastructure and discounted.
Regulatory Verification Notes
The captured homepage discloses no legal entity, licence, registration number, terms page or other governance information. Operator identity could not be independently connected to any real-world person or organisation. Because the site lives on a shared-platform subdomain, there is no independent domain registration to anchor ownership, so ownership and governance remain opaque. No third-party broker or regulatory record matched this site, and none should be assumed. The absence of licensing information is a verification gap, not by itself evidence of fraud, but here it compounds the confirmed reputational findings. The only positive technical element is a valid, properly formed transport-encryption certificate. This indicates an encrypted connection only. It says nothing about the operator's legitimacy. Evidence:
- Homepage: no company name, licence, registration number or jurisdiction is presented.
- Hosting infrastructure: served from AS16509 (AMAZON-02 – Amazon.com, Inc., US).
- Transport encryption: TLS certificate issued by WR1 (DV, domain validation only), valid to 2026-11-27 with 31 days remaining.
What to Verify Next
The operator's identity and purpose should be established through independent channels before any engagement. Whoever referred the site should be asked to confirm the organisation behind PrecisionX through a separate, known contact route. Any claimed company registration or licence should be checked directly with the relevant registry, not through links on the site. The current detection status should be rechecked with the threat-intelligence sources, since reputational listings can change after clean-up. The official support or contact channels should be confirmed through an offline or independently sourced route. Evidence:
- Homepage: no identifiable operator or contact details are available to check.
- Domain hosting: the site runs on a shared-platform subdomain, so the legitimacy of the brand cannot be inferred from the domain name.
- Reputation findings: the blacklist and malicious detections are current and unresolved in the evidence.
Summary Verdict
The overall posture is high risk. Confirmed external threat detections and a blacklist listing outweigh the site's clean behavioural profile and valid encryption. The site's identity is unverified, and it cannot be treated as trustworthy.
Infrastructure Integrity
The site is delivered through a trusted CDN/WAF layer on Amazon-hosted infrastructure in the United States. All six observed IP addresses are CDN edge servers, and no origin server was visible. That edge-only visibility prevents independent verification of the true hosting location and can mask rapid content swaps. The protective infrastructure is a mitigating factor only and does not offset the reputational findings.
Closing Assessment
The site should be limited to read-only viewing at most. Account login, credential entry, payments and any other financial interaction should be avoided, and nothing should be downloaded from it, until its operator is independently identified and the external detections are cleared.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- A large share of what the page loaded came from other domains.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 91 reports on hosting IP 64.29.17.195 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of bookmark-plum-zeta.vercel.app.
- The request stayed on bookmark-plum-zeta.vercel.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 64.29.17.195 |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 91 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about bookmark-plum-zeta.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.