Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
send-dt-bsc.vercel.app shows high-risk / scam indicators.
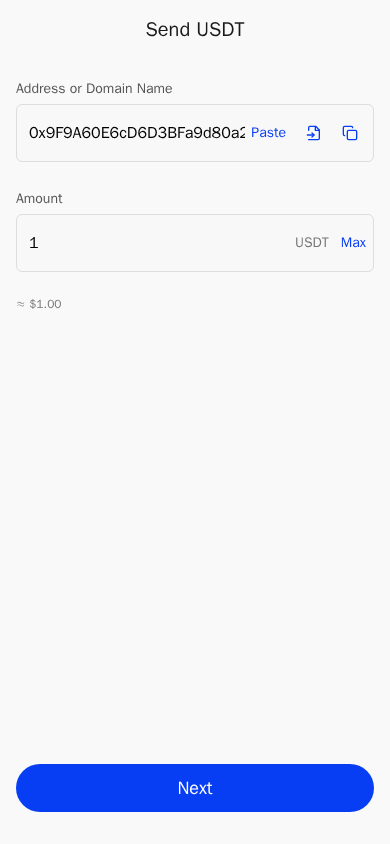
| What this site appears to be | A crypto wallet interface labeled 'Transfer Trust Wallet' for sending USDT, with fields for recipient address or domain, amount, a Max button, and a Next button. The captured text includes no domain, legal identity, fee terms, or support contact, and the brand name alone does not establish that this is the official wallet. Brand impersonation is not confirmed because the source domain is not provided. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 18 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 82 reports; shared hosting inflates reports | Clear |
| Domain age | 11 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a single-page interface titled "Transfer Trust Wallet" that presents a USDT send form with an address-or-domain field, an amount field, a Max button and a Next button. The page has no company name, fee terms, support channel or service description, so its apparent purpose is to collect a cryptocurrency transfer instruction while posing as a wallet service.
Scam/Impersonation Risk
This is the dominant concern. Several major security vendors currently flag the site as malicious, and a number of additional engines rate it suspicious. This amounts to a confirmed blacklist listing and is the decisive factor behind the elevated-risk assessment. The page's own content supports that reading. It asks a visitor to enter a recipient and an amount for a stablecoin transfer, yet offers nothing that would justify trusting it with value: no provider identity, no fee schedule and no way to tell where funds end up. The wallet branding is an unsupported claim, because the name "Trust Wallet" on a bare form does not show that this is the official product. The site's hostname is a free-tier subdomain on a general-purpose hosting platform, and its name closely resembles that platform's domain. Impersonation of a specific brand is not confirmed, but this is the pattern typical of disposable lookalike pages. During sandbox testing the page also made several outbound requests to non-allow-listed third-party destinations, including data-submitting requests. Wallet-drainer, clipboard-hijacking and hidden-form behaviors were not observed. The site shows no conflicting legal identities, because it shows no legal identity at all. Evidence:
- Homepage: a single crypto-transfer form (recipient, amount, Max, Next) with only about 89 characters of visible text and no title, description or branding metadata.
- Threat intelligence: 18 engines rate the domain malicious and 2 suspicious, including three tier-one vendors, which triggered the automatic critical-risk override.
- Archive record: 2 snapshots between 2026-10-09 and 2026-10-13, with about 10 days of observable history.
- Sandbox: three runs recorded 3 non-allow-listed external POST requests and 3 non-allow-listed XHR calls, with up to about 56% of requests going to external destinations.
Regulatory Verification Notes
The page contains no legal entity name, licence or registration claim, terms of service, privacy policy or contact route. A service that moves customer funds would normally disclose these items, and their absence leaves the operator unidentified. No third-party broker or regulator record matches the site, and no licensing authority is cited that could be checked. These gaps are verification and transparency shortfalls rather than proof of wrongdoing in themselves. Here they sit alongside the confirmed security-vendor detections, so they reinforce the cautionary assessment instead of being a neutral omission. Technical hygiene does not offset this. The site's encryption is a basic domain-validated certificate, which proves only control of the hostname and says nothing about who operates it. Evidence:
- Homepage: no operator name, address, licence number, fee terms or support channel appears in the captured content.
- Transport encryption: certificate issued by WR1 (domain-validated), valid to 2026-11-27.
- Hosting: served from AS16509 (AMAZON-02 - Amazon.com, Inc., US).
- No third-party broker-intelligence match was found for the domain.
What to Verify Next
No one should send funds through this page. If a wallet or transfer link reached someone by message, social post or advertisement, the first step is to establish the sender's real identity independently. The wallet vendor's official application or website should be reached only through a channel the user already trusts, such as the official app store listing or a manually typed, bookmarked address. Any claim of affiliation with a named wallet brand should be confirmed on that brand's own official channels, and the official support route should be confirmed offline or through those same channels. Anyone who has already entered an address or authorised a transaction should review their wallet's recent approvals and transactions, revoke token permissions, and move remaining assets to a freshly created wallet if the seed phrase was ever entered. Evidence:
- Homepage: the transfer form gives no indication of which service or which on-chain destination it will use.
- Page analysis: the branding claim is unsupported, and the value flow is opaque.
- Third-party detections are current, so any earlier interaction should be treated as potentially exposed.
Summary Verdict
Available evidence places this site firmly in a high-risk posture. Active detections from several independent security vendors, combined with a financial-transaction form that discloses nothing about who runs it, outweigh any technical signals in its favor. Its identity remains unverified, and nothing collected supports treating it as a legitimate wallet service.
Infrastructure Integrity
The site is served from Amazon-hosted address space through a content-delivery layer. Every observed address is an edge node, the origin server could not be observed, and the delivery layer's shared addresses are reputable and pose no direct concern. Abuse reports tied to one of those addresses (82 in total) relate to shared provider infrastructure rather than this site, so they were discounted. The protective infrastructure is a mitigating factor only. It does not offset the external detections, and edge-only visibility makes it harder to verify hosting independently and to notice rapid content swaps.
Closing Assessment
Nobody should enter wallet addresses, approve transactions, connect a wallet or transfer funds through this site. Passive viewing is the only use that does not expose the visitor to risk. Anyone who encountered it through an unsolicited message should treat that message as suspect and report the link to the platform that delivered it.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Signals weighed against the site
- AbuseIPDB: 82 reports on hosting IP 216.198.79.3 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of send-dt-bsc.vercel.app.
- The request stayed on send-dt-bsc.vercel.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-10-09. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 216.198.79.3 |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | 0.03 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-10-09 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 18 flagged | AbuseIPDB: 0% confidence, 82 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about send-dt-bsc.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.