Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
cetus-zone.xyz shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: An ownership check raised a concern: the registration record did not name the registrant. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | Cetus is a decentralized exchange and liquidity protocol on the Sui network. The page offers token swaps, concentrated-liquidity pools, DCA and limit-order automation, a token-claim flow, and developer resources. It shows wallet-connect prompts and no login or credential forms. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-21 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-21.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 9 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 24 days oldRegistered 2026-09-27 | Risk |
| Web archive | Archived since 2024144 snapshots; the history predates the current registration (2026-09-27); an earlier owner may have held the name | Noted |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
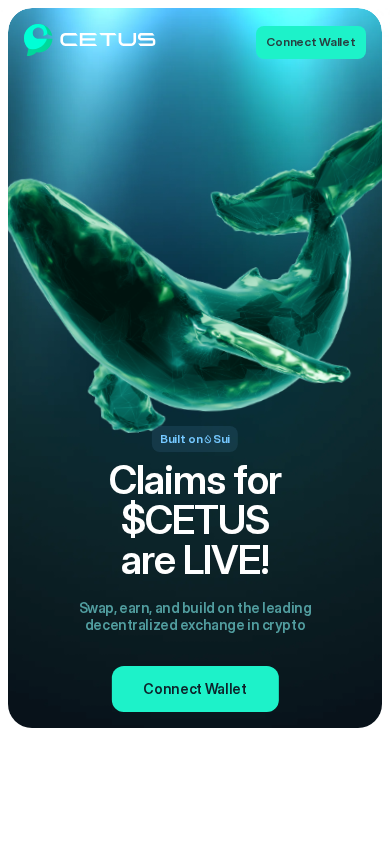
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-09-27).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
Cetus Zone is a decentralized-finance landing page that presents itself as the Cetus exchange and liquidity protocol on the Sui network. To a visitor it offers token swaps, concentrated-liquidity "Infinity Pools", dollar-cost-averaging and limit-order automation, a launchpad for new tokens, a live token-claim banner and developer documentation. The apparent business model is fee income from swaps and liquidity provision, with CETUS and xCETUS rewards paid to active users and liquidity providers. Every action is gated behind a wallet connection rather than a login form.
Scam/Impersonation Risk
Contradictory signals are present and decisive. Several independent security engines currently flag the site as malicious, and the combined external reputation amounts to a confirmed blacklisting. Nothing in the available evidence offsets this. The page's own content analysis found no credential forms, hidden forms or clipboard manipulation, and no brand impersonation was formally flagged. The absence of those indicators does not neutralise the external detections. The site's profile also matches a well-known lure pattern. A freshly registered domain carrying a protocol's name promotes a live "Claims for $CETUS are LIVE!" banner and pushes visitors to connect a wallet. The wallet picker offers a Tron wallet path and TronLink on a site that says it is built on Sui, which is incongruent. The homepage states unverifiable headline figures, namely roughly $103B in trade volume, 18M accounts and 214M all-time trades. It also advertises "Audited by" without naming any auditor. The published contact address sits on a different domain from the one serving the page. That makes it impossible to confirm that this domain is the protocol's official property. The features themselves (swaps, concentrated-liquidity pools, DCA and limit orders, token launches, reward-bearing positions) carry real market and smart-contract risk. On a flagged domain, a connected wallet or a signed "claim" transaction is the main loss vector, and funds sent to or approved for the wrong destination are generally unrecoverable. Identity is unverified and ownership is opaque.
- Homepage: a prominent token-claim banner and a Connect Wallet call-to-action precede any explanatory content, and the wallet list includes a Tron wallet continuation prompt on a Sui-branded product.
- Homepage: unsourced statistics counters (trade volume, accounts, all-time trades) are shown without any verifiable reference.
- Domain registration: created 2026-09-27 (~0.06 years old, about 23 days), registered through NICENIC International Group Co., Limited and running to 2027-09-27.
- Web archive: 144 snapshots, all captured in 2024 (first and last seen 2024-04-18, 1 year tracked), which sits at odds with the very recent current registration.
Regulatory Verification Notes
The site claims no license, regulator or registration number, and the page names no legal entity, operating company or jurisdiction. As a permissionless, non-custodial DeFi front end, it would not necessarily carry a financial license. But no responsible party can be identified from the page, so users have no recourse path. Its audit claim cannot be assessed because no audit firm or report is cited. No third-party broker or regulator record matched the site. The page does present a named team, documentation and social channels (Twitter, Discord, Medium, Telegram), but these on-page assertions do not establish who controls this particular domain. Given the confirmed external detections, none of this can be treated as legitimacy evidence.
- Homepage: an "Audited by" badge appears without any named audit firm or linked report.
- Homepage and footer: no company name, registered address, licensing authority or license number is published.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by YE1 with domain-validation (DV) only, valid to 2026-12-26 (about 66 days remaining), which proves control of the domain, not the operator's identity.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "YE1 with domain-validation" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site. "Valid to" is the date it expires.
What to Verify Next
The first step is to establish whether this domain is the protocol's official property, using only independently sourced channels. These are the project's official documentation and announcements, reached through a route that does not start from this site, and its verified social accounts. Any token claim should be confirmed there before any wallet is connected. The audit claim should be checked directly with the named auditor's own publication. Anyone who has already connected a wallet or signed a transaction on this domain should review and revoke token approvals and consider moving assets to a fresh wallet. The project's official support channels should be confirmed independently as well.
- Homepage sandbox sessions recorded 12 outbound POST requests, 9 of them to destinations outside known-benign services.
- The same sessions logged 15 external data requests, 9 to unrecognised destinations, and 42 console errors.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Homepage: the claim banner and wallet connection prompt are the only interactive entry points, so any on-chain exposure begins there.
Summary Verdict
The site presents a polished and technically functional DeFi front end, but confirmed adverse threat-intelligence findings, a very recently registered domain and unverified operator identity place it firmly in an elevated-risk category. Its surface quality does not offset those findings. Its legitimacy cannot be accepted, and it should be treated as hostile until independently cleared.
Infrastructure Integrity
The site sits behind a mainstream CDN and WAF, and only edge addresses were observable, with no origin server visible. The hosting provider is reputable and the certificate is valid. Together these are a mild mitigating factor for availability and transport security. Such infrastructure is available to any customer, benign or malicious, so it says nothing about the operator's intent. It also limits independent hosting verification and can mask rapid content swaps. A young-domain, sparse-subdomain pattern was noted as an unconfirmed heuristic only and is weighted accordingly.
Closing Assessment
Do not connect a wallet, sign any transaction, claim tokens, grant approvals or enter credentials on this domain. Viewing the page passively is the only proportionate use, and any DeFi activity should be conducted solely through independently confirmed official addresses.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, hosting and network, registration and ownership and behaviour in a sandbox.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
03 Hosting and network
- The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
04 Registration and ownership
- The registration record did not name the registrant.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
05 Behaviour in a sandbox
- The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of cetus-zone.xyz.
- The request stayed on cetus-zone.xyz. It was not redirected to another domain. Clear
- Registered through NICENIC INTERNATIONAL GROUP CO., LIMITED. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-09-27. Noted
- The earliest public archive of this name is from 2024-04-18, before the current registration on 2026-09-27; an earlier owner may have held it. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3035::ac43:b951 (a CDN edge address; the server behind it was not observed) |
| Name servers | shaz.ns.cloudflare.com, vicente.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-26 |
| Domain age | 24 days (registered 2026-09-27) |
| Domain expiry | 2027-09-27 |
| Archive first seen | 2024-04-18 (2.5 years before capture) |
| Archive snapshots | 144 |
| Reputation | VirusTotal: 9 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
The web archive has records of this name from 2024-04-18, before the current registration on 2026-09-27. That archive history predates the current registration, and an earlier owner may have held the name.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about cetus-zone.xyz at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.