Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
claim-meme.netlify.app shows high-risk / scam indicators.
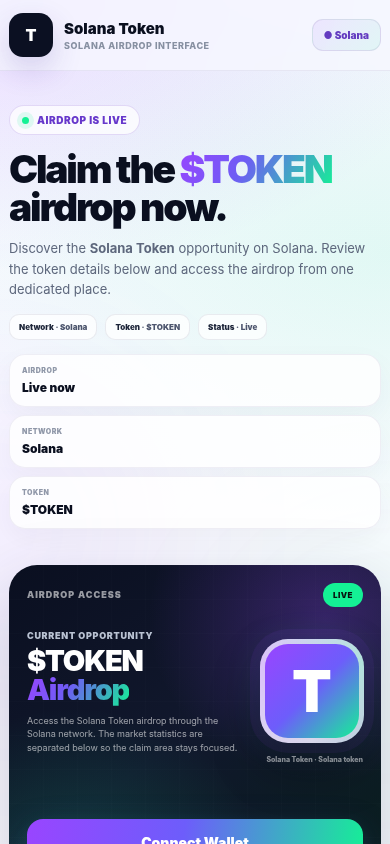
| What this site appears to be | A Solana token airdrop page that invites visitors to connect their wallets to claim $TOKEN. It shows no verifiable issuer, contract, or legal identity, and it displays unverifiable live claim activity and partner-ecosystem names. The missing proof for a wallet-connection action makes it high-risk. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- VirusTotal and Google Safe Browsing had no flags for this domain; its hosting IP carries AbuseIPDB reports below the confidence level TrustSniffer treats as a flag.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
This website is a single-page Solana token airdrop portal titled "Solana Token — $TOKEN Airdrop". It tells visitors that an airdrop is live and invites them to connect a crypto wallet to claim a placeholder token called $TOKEN. The page carries generic branding, market-data panels and a scrolling feed of recent claims. It discloses no issuing project, and its only visible value flow is the wallet-connection step, which suggests a wallet-solicitation or token-promotion model.
Scam/Impersonation Risk
No formal contradictions were observed. There is no confirmed phishing or impersonation finding, no conflicting legal identities, and no threat-intelligence listing. The page content itself nonetheless shows a cluster of fraud-pattern indicators, and these are the reason for the cautious assessment. The homepage's "Recent airdrop activity" feed shows wallet claims stamped one to a few dozen seconds ago, each paying about 1 to 2 SOL. The advertised prize is a token called $TOKEN, so the payouts are inconsistent with the offer. The feed also cannot be tied to any on-chain source. The statistics panel quotes 100,000 24-hour activity, 61,000 airdrop claims and 39,000 distributions, while the price, market cap, liquidity and volume panels are all empty placeholders. The "Contract" field in the token details is blank, so a visitor has no way to confirm which asset is being distributed. A ticker of well-known Solana ecosystem names (BONK, Jito, Marinade, Metaplex, Orca, Pyth, SolBlaze) implies partnerships or endorsements that the page does not substantiate. Together, these elements are consistent with the engineered urgency and social proof used in wallet-solicitation campaigns, though they do not by themselves prove that this page is one. The domain is also a free subdomain on a mainstream hosting platform. Automated lookalike analysis flagged its similarity to that platform's name, but this reflects the hosting arrangement and is not evidence of impersonation. Two abuse reports exist against a shared cloud address used by this site (a content delivery network IP operated by Amazon Data Services Ireland Ltd, with a confidence score of 0). They have been discounted because they apply to the provider's shared, multi-tenant infrastructure and are not attributable to this site. In a controlled browser session the page made no external network calls, showed no hidden forms, and ran no clipboard manipulation or wallet-drainer behavior. The session did not complete a wallet connection, so the post-connection signing flow remains untested. Evidence:
- Homepage: the recent-activity feed lists truncated wallet addresses with payouts of roughly 1 to 2 SOL for a claim of a different asset, $TOKEN.
- Homepage: the aggregate claim and distribution counts sit beside market-data fields that are all blank, and the token contract field is empty.
- Homepage: seven named Solana ecosystem projects appear in a marquee with no link, attribution or proof of relationship.
- Hosting posture: the domain is a platform-provided subdomain, and the only abuse reports concern a shared provider address, so they are discounted as shared-infrastructure reports.
Regulatory Verification Notes
The site contains no legal or identity pages. It names no issuing entity, foundation or developer, and it offers no terms of distribution, privacy statement, audit, license, registration number, contact route or physical address. The airdrop is therefore not tied to any accountable party that could be identified from the page. For a mechanism that asks for a wallet connection, these omissions are material disclosure gaps, and operator identity remains unverified. The assessment reflects both the opacity around ownership and governance and the absence of any verifiable licensing or legal status. The analysis found no third-party reputational record for the site. That is neutral and does not offset the on-page gaps. The transport layer is sound, but encryption establishes only a secure channel and says nothing about the operator's legitimacy. Evidence:
- Homepage: no company name, legal terms, privacy policy, contact details or regulator reference appears anywhere on the page.
- Homepage: the project is described only as "Solana Token" with the symbol $TOKEN, with no issuer or distribution rules.
- The site's transport encryption: an organization-validated TLS certificate issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 to Netlify, Inc, valid to 2027-03-19.
- The site's hosting infrastructure: served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
What to Verify Next
Before any wallet interaction, the airdrop's legitimacy should be confirmed independently of this page. First, a token project's official website or verified social account, reached through an independent route and not through this page, should confirm that this specific airdrop exists. Second, any claimed token mint address should be checked in a public Solana blockchain explorer for its creation date, holder distribution and authority settings. Third, the ecosystem projects named on the page should be asked, through their own channels, whether they have any relationship with this campaign. Fourth, the official contact and support channels for the claimed project should be confirmed offline or through trusted directories. If, after these checks, a wallet is connected, it should be a newly created wallet holding no meaningful assets, and each signature request should be reviewed before it is approved. Evidence:
- Homepage: the empty contract field means the asset cannot be matched to an on-chain record from the page alone.
- Homepage: the "Connect Wallet" and "Access the airdrop" controls are the only calls to action and are not supported by any documentation.
- Homepage: the ecosystem names are displayed without links or announcements that could be checked.
Summary Verdict
The available evidence is consistent with an unverified promotional or wallet-solicitation page and not with an established, accountable project, and it calls for verification before any further step. Technical hygiene is adequate, but it is outweighed by the unproven claims, the missing issuer identity and the high-stakes nature of the requested action. No hard contradiction was found, so the overall posture is to verify before proceeding.
Infrastructure Integrity
The site is served from Amazon-operated infrastructure behind a content delivery and web-application-firewall layer, and all observed addresses are edge nodes, so the origin server is not visible. The transport-security configuration is sound and the infrastructure provider is reputable. These factors mitigate technical exposure only. They do not establish who operates the page, and edge-only visibility means the underlying content could be changed quickly without a change in the hosting footprint.
Closing Assessment
Treat the page as an unverified claim. Confirm the issuer and token contract through independent official channels before connecting a wallet, sharing seed phrases or approving any signing request.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by page content, several checks together.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED
02 Several checks together
- No external feed lists the site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
Signals weighed against the site
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (Amazon Data Services Ireland Ltd, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of claim-meme.netlify.app.
- The request stayed on claim-meme.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:58f:6200::259 |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 flagged | AbuseIPDB: 0% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about claim-meme.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.