Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
deepsafenetwork.live shows high-risk / scam indicators.
| What this site appears to be | DeepSafe's page sells $800 'Verifier NFT' passes for a CRVA verification network. Buyers get a promised 5,000-token $DEF airdrop, staking to nodes, $40 referral cashback, and future airdrops, with payment via crypto wallet connection. No legal entity, audit, team, or verifiable live product is shown, and the page is an unverified high-stakes financial transaction. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 26 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20263 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
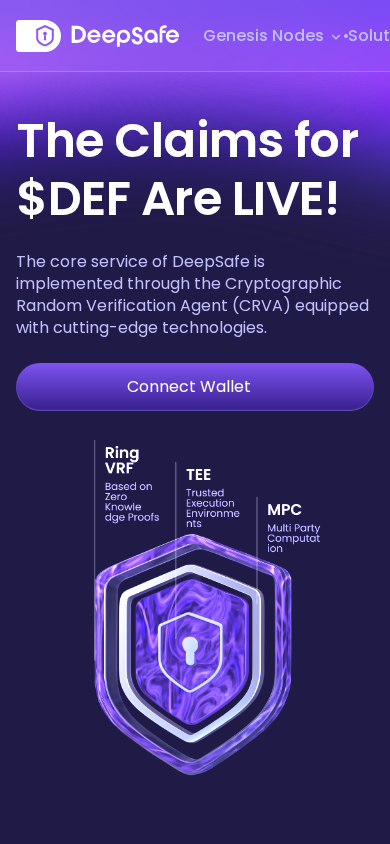
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
DeepSafe is a single-page Web3 landing site that sells "Verifier NFT" passes for a proposed "Cryptographic Random Verification Agent" (CRVA) network. It presents a wallet-connect interface, a $DEF token airdrop narrative and a referral scheme. Its apparent business model is revenue from NFT sales and from recruiting further buyers, not from a demonstrable product or service.
Scam/Impersonation Risk
The site shows confirmed contradictory signals. It is blacklisted by external threat-intelligence sources, and a major network-security vendor flags it among multiple malicious detections. No brand impersonation and no conflicting legal identities were observed, so the risk comes from the reputation findings combined with the commercial structure of the offer.
The homepage asks for an upfront payment of $800 per pass. In return it promises 5,000 $DEF tokens per NFT, with 30% unlocked in the six months after a mainnet launch that has no demonstrated date, then a six-month lock and a linear release over the following year. It also promises staking of those tokens to "DeepSafe nodes", a $40 cashback for each successful referral, and unspecified "future airdrops". Referral codes work only for people who already hold an NFT, so payouts depend on recruitment. This is the structure of a multi-level or referral-income scheme, not a product purchase. The page also contradicts itself. It announces that "$DEF claims are LIVE" while the pass is marked "Ended", and it describes a verification network without showing a working product, audit or technical documentation.
Payment runs through a wallet selector covering more than a dozen wallets, including a Tron wallet flow. The page also shows a transaction-signing prompt. Behavioural testing found that most outbound POST traffic and a large share of background data requests went to destinations outside any recognised-service set. It also recorded a very high volume of client-side errors, consistent with an unfinished or hastily assembled front end.
- Homepage: the $800 "Verifier NFT" is presented with a "$DEF are LIVE" banner, while the same pass is labelled "Ended".
- Homepage: the rules state that referrers must hold an NFT to activate invitation codes, and the $40 cashback is paid per successful referral.
- Browser testing: 12 external POST requests, 9 of them to non-whitelisted destinations, and 15 external background requests, 9 of them non-whitelisted.
- Browser testing: 188 console errors across 3 successful runs.
- Domain registered 2026-09-26 (~24 days old). The web archive holds only 3 snapshots, from 2026-09-26 to 2026-10-09 (1 year tracked).
Regulatory Verification Notes
The site names no legal entity, operator, team, registered address, audit, refund policy or terms of sale. It claims no licence or registration, so there is nothing to validate. For a site that collects high-value crypto payments and promises token distributions, that silence is a material disclosure gap. It also leaves buyers with no named counterparty to hold accountable. Domain ownership details are withheld or incomplete, so the operator cannot be tied to any real-world person or company. The registrar is a Hong Kong-based provider, which says nothing about the operator's identity or jurisdiction. No third-party broker or regulator profile matched this site. The absence of one is not treated as a finding.
- Homepage: no company name, jurisdiction, licence, audit, team or contact address.
- Homepage: no refund, dispute or risk-disclosure language beside the $800 payment prompt.
- Domain registration is through NICENIC INTERNATIONAL GROUP CO., LIMITED, created 2026-09-26 and expiring 2027-09-26.
- TLS certificate issued by YE2 (DV, domain validation only), valid to 2026-12-25. It confirms an encrypted connection but nothing about who runs the site.
- Served from AS13335 (Cloudflare, Inc., US).
What to Verify Next
Before any engagement, an evaluator should look for an independently verifiable legal entity behind DeepSafe. That means a corporate registry entry, a named team with traceable professional histories, and a published smart-contract address that can be inspected on a public block explorer. Any claimed audit should be confirmed directly with the auditing firm through its own channels, not through links on this site. The $DEF token and the CRVA "mainnet" should be checked for independent listings, working code repositories and announcements from established sources. The official contact and support channels should be confirmed through an independent route. Any regulator in the evaluator's jurisdiction that supervises token sales or investment schemes should be consulted on whether such an offer is permitted.
- Homepage: the mainnet launch, node staking and token vesting are described but not linked to any verifiable contract, repository or documentation.
- Homepage: the page names no auditor and no regulator.
- External reputation: the site is flagged as malicious or suspicious by several independent detection sources, which warrants checking current status before any contact.
Summary Verdict
The assessment is critical and clearly cautionary. Confirmed external threat detections, a deposit-first referral-driven offer, unverifiable claims and an operator who cannot be identified converge on a high-risk posture. A valid certificate and clean reputation of the hosting provider do not offset these findings. The only use consistent with the evidence is passive, read-only viewing. Account login, credential entry and any financial interaction are unsafe.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and web application firewall, and all observed addresses are CDN edge servers. The true origin host was not observable. This is a mitigating factor only. It shows that mainstream protective infrastructure is in use, but it conceals the actual hosting location and allows page content to be swapped quickly without visible changes in hosting. Protective infrastructure cannot offset the external threat detections.
Closing Assessment
No wallet should be connected to this site, no transaction signed and no funds sent, and referral links or invitation codes should not be shared. Anyone who has already interacted with it should revoke token approvals for the wallets used and consider moving remaining assets to a fresh wallet. Any losses should be reported to the relevant financial or cybercrime authority.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of deepsafenetwork.live.
- The request stayed on deepsafenetwork.live. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-26. Noted
- The earliest public archive of this site is from 2026-09-26. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3031::6815:2406 |
| Name servers | magnolia.ns.cloudflare.com, quinton.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-12-25 |
| Domain age | 0.07 years (continuous registration) |
| Domain expiry | 2027-09-26 |
| Archive first seen | 2026-09-26 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about deepsafenetwork.live at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.