Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
directassetreclaim.com shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 1% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports | Clear |
| Domain age | 7 months oldMost scam domains are under a year old | Watch |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
| Hosted by | PONYNETServer in US | Noted |
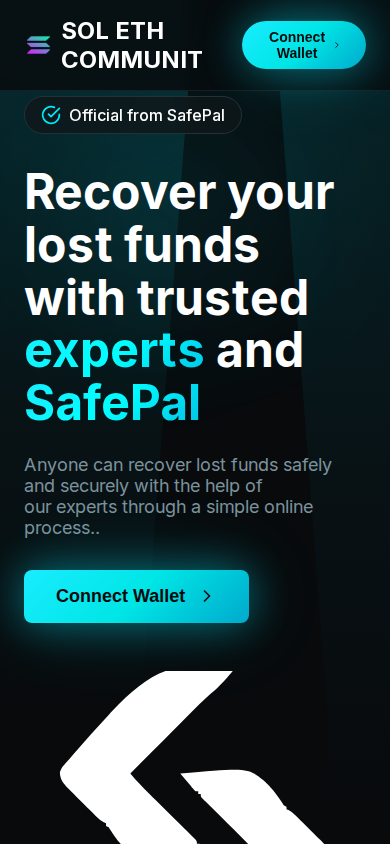
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
The website directassetreclaim.com is a single-page presence whose title is simply the domain name. Its name positions it as an asset or funds recovery service, and the homepage carries only a short block of text. Its apparent purpose is to attract visitors seeking recovery of lost assets, and any commercial model would depend on visitors engaging with the operator directly.
Scam/Impersonation Risk
This site presents confirmed adverse contradictions and warrants a clearly cautionary reading. Several independent threat-intelligence engines currently classify the domain as malicious or suspicious, and the site is blacklisted on that basis. The reputational record also carries a prior phishing association. During interactive sandbox testing, the homepage changed materially after interaction, which is strong cloaking behavior. The rendered content differs from what a passive visit shows, a pattern typical of deceptive pages. The sandbox also saw heavy background traffic to external destinations, though none was outside known-benign services, and no wallet-draining, clipboard-hijacking, or hidden credential-form behavior. Two abuse reports exist against the hosting address, which is shared provider infrastructure. They are weaker evidence about this site specifically, but they are not discounted, and they add to the picture. No conflicting legal identities or confirmed brand impersonation were observed. Evidence:
- Homepage, sandbox testing: strong cloaking after interaction, with a substantial semantic and visual change in the rendered page across three successful runs.
- Reputation checks: four engines rate the domain malicious and one rates it suspicious, and an external blacklist listing is active.
- Hosting address: two abuse reports in the recent past, in spam and web-abuse categories, attributed to a shared hosting address.
- Domain registration: registered 2026-03-30 (~0.59 years old), so the domain has no meaningful operating history.
Regulatory Verification Notes
The captured homepage does not clearly disclose the operator's legal identity, a company registration, or any licensing or regulatory authorization. The real-world operator has not been independently verified. This matters because the site's name implies a recovery service for lost funds or assets, a category where lawful operators are normally expected to show authorization. No regulatory registration could be matched, and no third-party broker intelligence was found. On the technical side, the site holds a valid but only domain-validated certificate. That proves control of the domain, not the identity of the operator. Evidence:
- Homepage: the short page text discloses no company name, registration number, or licensing detail.
- Domain registration: registered through PDR Ltd. (PublicDomainRegistry.com) from 2026-03-30 to 2027-03-30, with the registrant shielded by Privacy Protect, LLC.
- Transport encryption: TLS certificate issued by YR1 (DV), valid to 2027-01-30.
- Hosting: served from AS53667 (PONYNET – FranTech Solutions, US).
What to Verify Next
Any claim of authorization should be tested against the official register of the relevant financial regulator in the visitor's own jurisdiction, searching by the exact operator name and registration number. If the operator cannot supply those details, no engagement is warranted. Any claimed contact channel or case reference should be confirmed through an independent route, such as a regulator-published number, rather than details shown on the site. Visitors who have already submitted details or money to this operator should contact their bank or payment provider and consider reporting the site to a consumer-protection or cybercrime authority. Evidence:
- Homepage: no verifiable corporate or licensing identifiers were captured to check against a registry.
- Domain history: the site is about seven months old, so no track record exists to cross-check.
- Reputation findings: the active threat detections make independent confirmation a precondition for any interaction.
Summary Verdict
Available evidence places this site in an elevated-risk posture. Confirmed threat-intelligence detections, deceptive page behavior, and a very young domain with no verified operator point in the same direction, and the few hygiene positives do not offset them. The site should be treated as untrustworthy for any sensitive purpose until the detections are resolved and an operator is independently verified.
Infrastructure Integrity
The domain resolves to a single directly exposed address at a US data-center provider, with no CDN or WAF in front of it. The site therefore gets no protective-infrastructure mitigation, and the address is shared with other tenants. The valid certificate and a correctly identified network owner are baseline hygiene only. They do not offset the reputation findings.
Closing Assessment
At most, read-only viewing is acceptable, and it should happen from an isolated, non-sensitive environment. Logging in, entering credentials, paying fees, or sharing personal or financial details with this site should be avoided entirely. Anyone seeking asset recovery should use an authorized provider they have identified independently through an official regulator register.
Written analysis generated 2026-11-01 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY
03 Registration and ownership
- Registration details are held behind a privacy service, so no operator is named publicly. This is common and legal, and it also means there is nobody to check.Registration and ownership
rule:KF_WHOIS_PRIVATE
Signals weighed against the site
- AbuseIPDB: 2 reports on hosting IP 198.251.83.106 (FranTech Solutions, Data Center/Web Hosting/Transit), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 15% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of directassetreclaim.com.
- The request stayed on directassetreclaim.com. It was not redirected to another domain. Clear
- Registration is published under PDR Ltd. d/b/a PublicDomainRegistry.com. Clear
- DNS for this domain is served by asurahosting.com, across 2 name servers. Noted
- The registration is paid up to 2027-03-30. Noted
- It is hosted on PONYNET, from a server in US. Noted
Domain intelligence
| Registrar | PDR Ltd. d/b/a PublicDomainRegistry.com |
|---|---|
| Hosting | PONYNET - FranTech Solutions, US |
| Country | US |
| Server IP | 198.251.83.106 |
| Name servers | NS25.ASURAHOSTING.COM, NS26.ASURAHOSTING.COM |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR1 |
| SSL expiry | 2027-01-30 |
| Domain age | 0.59 years (continuous registration) |
| Domain expiry | 2027-03-30 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 1% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about directassetreclaim.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.