Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
dttjjkkllzbvesjzndtp.vercel.app shows high-risk / scam indicators.
| What this site appears to be | Russian-language page presenting a video/file labeled as official material and giving step-by-step instructions to download and install a file, including enabling installation from unknown sources. Likely a malicious drive-by installer or social-engineering lure. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 7 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 72 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
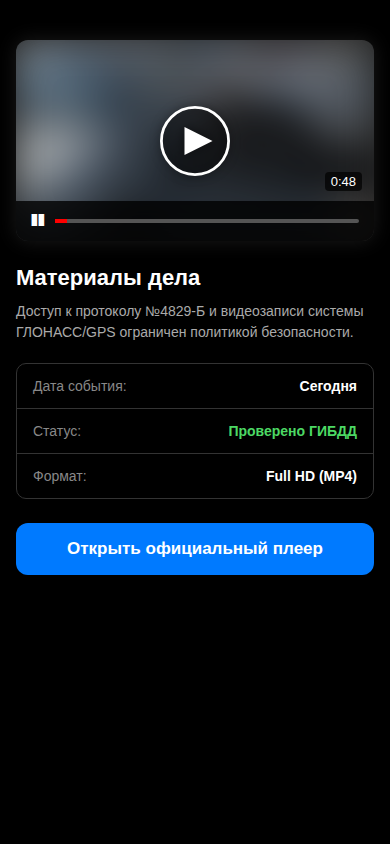
This website is a single-page, Russian-language lure that poses as an official traffic-incident video record. It presents a "Registrar" player page with case-file styling and prompts the visitor to download and manually install a file in order to view the footage. Its apparent purpose is not to offer a product or service but to deliver an installable payload, most likely an Android application package, to visitors through social engineering.
Scam/Impersonation Risk
Contradictory signals are confirmed, and the posture is clearly cautionary. The domain is currently blacklisted by external reputation sources. Multiple security engines classify it as malicious, and several of them are among the most widely deployed in enterprise environments. The homepage content explains why. It frames the download as official evidence, citing a numbered case protocol, a GPS/satellite-tracking recording, and a "Verified by traffic police" status. It states that access to the material is restricted by security policy, which creates urgency and a sense of authority. The visitor is then walked through four steps: accept the download, click through any browser warning with "Download anyway", open the file, and enable installation from an unknown source. The advertised "recording" is a small file of about 2.4 MB, which is implausible for a Full HD video. This is a claim-evidence mismatch typical of drive-by installer lures. Bypassing the platform's built-in install protections is the core of the attack mechanism. No brand impersonation and no conflicting legal identities were detected, so the risk comes from malicious-distribution behavior, not from a cloned brand. A large number of abuse reports exist against a shared hosting-provider address linked to the site. Those reports are discounted as shared-platform noise and do not drive this assessment. Evidence:
- Homepage: presents a "Registrar" page with a case protocol number, "Verified by traffic police" status, and an "Open official player" button, giving no verifiable source for any of these claims.
- Homepage: instructs the visitor to click "Download anyway" through browser warnings and to enable installation from an unknown source, a pattern associated with malicious payload delivery.
- External reputation: 7 malicious and 1 suspicious detections, including from three tier-one security vendors, with a confirmed blacklist hit.
- Hosting-provider address: 72 abuse reports, discounted because they apply to shared infrastructure.
Regulatory Verification Notes
The site makes no license claim and has no legal, terms, privacy, about, or contact pages. It names no operator, company, or registration number. Ownership and governance are therefore opaque, and the site's connection to any real-world entity is unverified. Its invocation of police authority is entirely unsupported by any attributable source, and no genuine government channel is identified. The domain is a randomly generated subdomain on a public application-hosting platform, with no distinctive brand name or page title. A page of this kind has no legitimate regulatory standing to assess. No third-party broker-reputation match exists, so this section rests on the absence of any disclosure, not on an external verdict. Evidence:
- Homepage: no operator name, legal entity, license, or registration number, and no legal or contact pages.
- Homepage metadata: no title, description, or structured data identifying a publisher.
- Hosting: served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
- Transport encryption: TLS certificate issued by WR1 (DV), valid to 2026-11-27. Domain-validated encryption only confirms domain control, not operator identity or intent.
What to Verify Next
The page itself should not be treated as verifiable. Anyone who received its link should confirm independently, through official government or police channels reached by a route that does not use this page, whether any such case record exists. The sender of the link should be contacted through a separate channel to establish how it was generated. Any device on which a file from this page was downloaded or installed needs prompt security triage. That means removing the application, revoking the unknown-source install permission, reviewing granted permissions and account activity, and running a reputable mobile security scan. Security teams should consider blocking the address and reporting it to the hosting platform and relevant abuse-reporting channels. Evidence:
- Homepage: the stated installation steps require disabling a core device safeguard, so any recipient who followed them should treat the device as potentially exposed.
- Homepage: the claimed case record cannot be validated from anything on the page, so confirmation must come from an official authority.
- External reputation: current malicious detections make blocking and abuse reporting proportionate steps.
Summary Verdict
The site reads as a malicious-file distribution and social-engineering lure, not as a legitimate service. The convergence of third-party malicious detections, a deceptive official-authority narrative, an installer disguised as a video, and an unattributable operator places it at the highest risk tier. The harmless-looking behavior observed in the sandbox does not change that, because the danger lies in the payload the visitor is persuaded to install.
Infrastructure Integrity
The site sits behind mainstream Cloudflare and Vercel edge infrastructure, and the observed addresses are all edge nodes, with no origin server identified. These protections concern delivery and availability only. They mitigate nothing about the content, and they cannot offset the reputation risk attached to the page.
Closing Assessment
The site should be neither opened on a device holding sensitive data nor interacted with. Files should not be downloaded, and no installation permission should be changed. Any exposure should be handled as a potential malware incident.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Signals weighed against the site
- AbuseIPDB: 72 reports on hosting IP 216.198.79.3 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of dttjjkkllzbvesjzndtp.vercel.app.
- The request stayed on dttjjkkllzbvesjzndtp.vercel.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 216.198.79.3 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 7 flagged | AbuseIPDB: 0% confidence, 72 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about dttjjkkllzbvesjzndtp.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.