Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
expirience.icu shows high-risk / scam indicators.
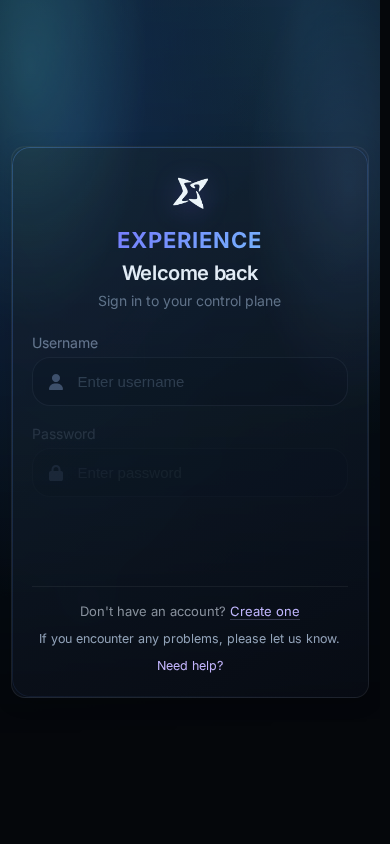
| What this site appears to be | A sparse login screen labeled 'Sign in to your control plane' requesting username, password, and authenticator code. No marketing, product details, contact info, or legal identifiers are present. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 4 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20264 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
This website presents a sparse control-plane sign-in interface requesting a username, password, and authenticator code. It provides no visible explanation of its services, products, pricing, operator, or commercial purpose, so its apparent function is limited to account access for an unidentified service.
Scam/Impersonation Risk
The site presents a critical sensitive-interaction risk. External reputation evidence records the domain as blacklisted by multiple sources and identifies multiple malicious and suspicious detections. The page itself intensifies that concern: it is a login-only interface with no surrounding business context, legal identity, contact information, or explanation of what the authenticated account controls. No conflicting legal entities or specific brand impersonation were observed, but the confirmed blacklist status and the unexplained request for authentication materially outweigh the limited benign technical observations.
- The login page requests a username, password, and authenticator code while providing no service description or operator identity.
- External reputation checks recorded the domain as blacklisted by 2 sources, with 3 malicious and 2 suspicious detections.
- The archive recorded 4 snapshots, first seen on 2026-10-01 and last seen on 2026-10-02, with 1 year tracked.
- The domain was registered on 2026-10-01 and is approximately 0.01 years old.
Regulatory Verification Notes
The available page does not disclose a legal entity, licensing authority, registration number, or regulated-business status. This prevents independent attribution of the service to a real-world operator; identity verification remains unverified. The absence of such disclosures is a regulatory and transparency gap, while the external reputation findings described above remain the decisive security concern rather than a licensing conclusion.
- The examined page contains no legal identifiers, licensing information, or regulatory disclosures.
- The domain registrar is PDR Ltd. d/b/a PublicDomainRegistry.com.
- The site uses a DV TLS certificate issued by YE2, valid until 2026-12-30 17:20:02 UTC.
What to Verify Next
The service should not be used for login, credential submission, account recovery, or financial activity unless its operator and purpose are independently established. A prospective user should confirm the intended service through a trusted offline or previously verified channel, match the operator against the relevant corporate and licensing registries, and obtain confirmation from an independently sourced support or security contact. Any credentials entered into the site should be treated as potentially exposed and handled under the organization’s incident-response procedures.
- Three sandbox runs completed successfully, with 0 external XHR requests and 0 external POST requests observed.
- The observed behavior recorded 6 console errors and a maximum post-interaction DOM difference of 75.
- No wallet-provider, wallet-sensitive, wallet-drainer, clipboard-hijacking, or hidden-form activity was observed.
Summary Verdict
The available evidence supports a critical-risk posture for sensitive interaction with an unidentified service. The combination of confirmed external reputation problems, an unexplained authentication surface, and absent operator context is inconsistent with a site suitable for trusted account or financial use.
Infrastructure Integrity
Cloudflare CDN/WAF protection fronts the website, which provides a mitigating layer against direct exposure but does not establish legitimacy. The observed edge infrastructure is associated with AS207003, operated by WEB1-AS – Web1 Oy, FI; the origin server was not observable in this analysis.
Closing Assessment
Treat the site as unsuitable for sensitive interaction unless its operator, purpose, and authorization can first be independently validated through trusted channels.
Written analysis generated 2026-10-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - A sign-in path on this site handles sensitive information.Page content
rule:PAGE_LOGIN_PATH_SENSITIVE
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of expirience.icu.
- The request stayed on expirience.icu. It was not redirected to another domain. Clear
- Registration is published under PDR Ltd. d/b/a PublicDomainRegistry.com. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-01. Noted
- The earliest public archive of this site is from 2026-10-01. Clear
- It is hosted on WEB1-AS, from a server in AE. Noted
Domain intelligence
| Registrar | PDR Ltd. d/b/a PublicDomainRegistry.com |
|---|---|
| Hosting | WEB1-AS - Web1 Oy, FI |
| Country | AE |
| Server IP | 78.17.209.207 |
| Name servers | THEO.NS.CLOUDFLARE.COM, ANGELA.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-12-30 |
| Domain age | 0.01 years (continuous registration) |
| Domain expiry | 2027-10-01 |
| Archive first seen | 2026-10-01 |
| Archive snapshots | 4 |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about expirience.icu at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.