Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
famous-kheer-db82b0.netlify.app shows high-risk / scam indicators.
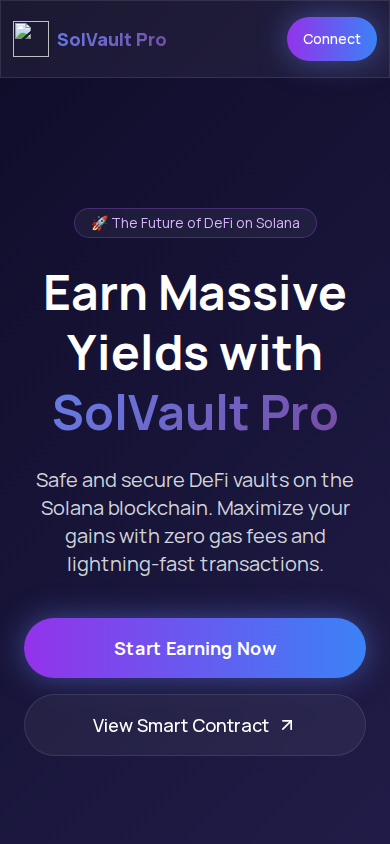
| What this site appears to be | SolVault Pro is a Solana DeFi landing page that invites visitors to connect a wallet, deposit SOL into yield vaults, and 'start earning' with 'massive yields'. It cites audits, multi-sig custody, and a 2% performance fee, but provides no named auditor, contract address, team, legal identity, or risk disclosure. The deposit flow is a high-stakes financial action with missing proof, and the statistics appear to be placeholders. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 1% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
SolVault Pro is a single-page Solana DeFi landing site that presents itself as a yield-vault platform. It invites visitors to connect a Phantom-style wallet, deposit SOL into vaults and "start earning" with what it calls "massive yields". Its apparent business model is custodial or pooled yield generation, with the operator keeping a 2% performance fee on generated returns. The site sits on a randomly generated subdomain of a shared hosting platform rather than a dedicated brand domain.
Scam/Impersonation Risk
This site carries a clearly elevated risk. Confirmed contradictions are present: it is currently blacklisted by an external threat-intelligence detection, which is decisive for the assessment. No conflicting legal identities and no brand impersonation were observed. The domain's resemblance to the hosting platform's name reflects the shared-subdomain structure, not a spoofed brand. Separately, four abuse reports exist against a shared provider address used by the site. These relate to shared infrastructure rather than demonstrably to this operator, so they are context and not an independent finding.
The homepage content is the main concern. It promises "massive yields" and "zero gas fees". It asserts "audited contracts" and "time-locked multi-sig wallets" for all vault funds, yet names no auditor, audit report, contract address, team or legal entity. The "View Smart Contract" call to action does not substantiate the custody claim. The headline statistics read as unpopulated placeholders ("$0M+" total value locked, "0+" active users, "0.0s" finality), which contradicts the "high security" and "Is my money safe? Yes" messaging. The flow follows a deposit-before-service pattern with no risk disclosure, no strategy description and no named counterparties. The source of the promised yield and the destination of deposited funds cannot be traced from anything the site publishes. The pattern of wallet connection, an immediate deposit prompt, unexplained returns and unverifiable safety assurances is consistent with high-yield vault schemes that route deposited funds to operator-controlled wallets. Automated browsing runs did not detect wallet-draining, clipboard-hijacking or cloaking behaviour, so the risk lies in the offer and its opacity rather than in observed malicious scripting.
- Homepage hero and "Why Choose SolVault?" blocks: "massive yields", "zero gas fees" and "audited contracts and multi-signature wallets" appear with no named auditor, report or contract address.
- Homepage statistics section: total value locked, active users and finality time are shown as "$0M+", "0+" and "0.0s", which indicates placeholder content.
- Homepage FAQ: the "Is my money safe?" answer asserts time-locked multi-sig custody, and the "How do I start?" answer directs visitors to connect a Phantom wallet and deposit SOL, with no supporting proof.
- Protocol-recognition check: the site is not recognised in any DeFi protocol directory, so no independently verified locked-value figure exists.
Regulatory Verification Notes
No licence, registration number, regulator, jurisdiction or operating company is disclosed anywhere on the site. The homepage footer carries only a generic copyright line, and no terms, privacy, about or contact pages were found to establish who operates the service. No third-party broker or regulatory record matched this site. This is a disclosure gap on a service that takes custody of user funds, and the real-world operator remains unidentified. The conclusion is therefore that the operator cannot be connected to any accountable legal entity, and the absence of such disclosure is treated as a verification gap, not as a finding in itself. The OV-validated certificate, issued to the hosting platform and not to the site's operator, confirms the encrypted transport of the connection but says nothing about the operator's identity or legitimacy.
- Homepage footer: only a generic copyright notice for the product name appears, with no legal entity, address, licence or registration identifier.
- Homepage business description: the 2% performance fee is stated, but strategies, counterparties, audit reports, team and legal entity are not.
- Hosting and transport: the site is served from AS16509 (Amazon), and its TLS certificate was issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 at the OV level to Netlify, Inc, valid to 2027-03-19.
What to Verify Next
Any engagement should be preceded by independent confirmation that a real, accountable operator exists. This means identifying the legal entity behind the service through an authoritative company or financial-services registry in the claimed jurisdiction, and confirming that the entity is authorised to take custody of customer assets. The audit claim should be tested by locating the named auditor's own published report and matching it to a specific on-chain program address. Without both, the audit and custody statements should be treated as unsubstantiated. The vault program's deployment history, upgrade authority and multi-sig signers should be inspected directly on a public Solana block explorer, rather than through links supplied by the site. Official support and contact channels should be confirmed through an independent route before any funds are committed.
- Homepage "View Smart Contract" call to action: no contract address is published, so on-chain verification has no starting point.
- Homepage FAQ and features text: the audit and time-locked multi-sig custody claims name no auditor, no signers and no lock duration to verify.
- Site-wide: no about, legal or contact page exists to anchor an entity lookup or a registry check.
Summary Verdict
The overall posture is high-risk and clearly cautionary. Confirmed external detections combine with an unverifiable, deposit-first yield proposition and an unidentified operator. Technical hygiene does not offset these concerns, and nothing in the evidence supports treating the site as trustworthy for any financial interaction.
Infrastructure Integrity
The site is served entirely from Amazon-operated address space behind a CDN/WAF layer. All four observed addresses are edge servers, and the origin server was not observable. This mitigates direct exposure and shows professional hosting. It does not confirm the operator's identity or intent. A free, platform-generated subdomain behind a shared edge also makes content swaps and redeployments trivial and fast, which is a recognised risk for short-lived deposit-collection pages.
Closing Assessment
Browsing the page in a read-only manner is acceptable. The wallet should not be connected, no assets deposited and no credentials or seed phrases entered, and engagement should not be reconsidered unless an accountable operator is independently established and the current external detections are withdrawn.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by external reputation, page content.
01 External reputation
- A small number of malware engines flagged this domain. On its own this is a weak signal.External reputation
rule:EXT_BLACKLIST_MEDIUM
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2a05:d014:58f:6200::258 (Amazon Data Services Ireland Ltd, Content Delivery Network), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of famous-kheer-db82b0.netlify.app.
- The request stayed on famous-kheer-db82b0.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:58f:6200::258 |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 1% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about famous-kheer-db82b0.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.