Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
first-ledgers.org shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 12 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 11% confidenceAbuseIPDB, 6 reports; shared hosting inflates reports | Clear |
| Domain age | 4 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
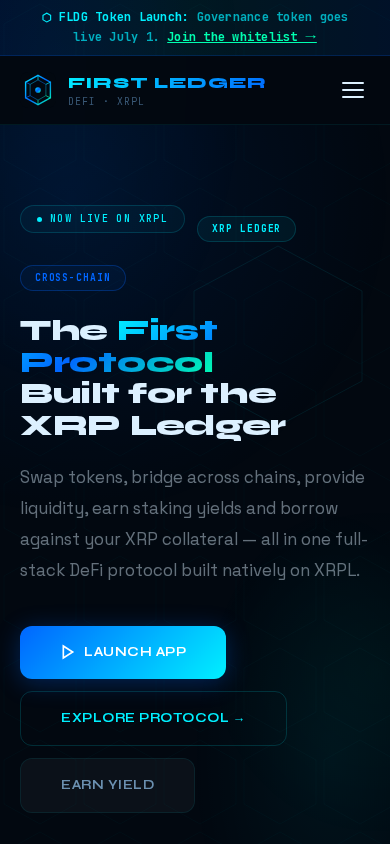
First Ledger presents itself as an "XRP DeFi protocol" on the XRP Ledger. Its homepage title advertises token swapping, cross-chain bridging, staking and lending, and the page carries a substantial amount of promotional text. The apparent business model is a self-service decentralized-finance front end that would invite visitors to move digital assets through the site's own interfaces. The domain is a recently registered .org address.
Scam/Impersonation Risk
Material contradictions are present, and they are what drive this assessment. Multiple leading security vendors currently flag the domain as malicious, and that detection is strong enough to qualify as a confirmed blacklist listing. This is a reputational finding about the domain itself, not an inference from its content. A separate set of abuse reports applies to the server address, which sits on a commercial hosting provider's shared infrastructure. Those reports are not discounted, but they are weaker evidence than the domain-level detections because they may relate to other tenants. No conflicting legal entities were observed, and no brand impersonation was confirmed. The page was captured successfully, but the site's identity could not be independently tied to any real-world organization. The product mix on the homepage (swap, bridge, staking and lending on a single ledger) is the kind of surface where phishing kits and fraudulent front ends commonly operate. A site of that type would normally be expected to appear in the established DeFi protocol directories, and it does not. In the automated browsing sessions, the site showed no wallet-drainer behavior, no clipboard tampering, no hidden credential forms and no cloaking. These are mitigating observations. They do not offset the active threat detections, and they cannot rule out malicious behavior that is gated on real user interaction. Page requests also went heavily to external destinations, and the sessions logged several script errors on the page. Evidence:
- Homepage: titled as an XRP DeFi protocol offering swap, bridge, staking and lending, with no corroborating protocol listing in a DeFi directory.
- Domain registered 2026-07-02 (about 0.3 years old), with only 1 archive snapshot, captured in 2026 (1 year tracked), so there is no meaningful independent history.
- Reputation checks: several tier-one security vendors flag the domain as malicious, and the blacklist condition is confirmed.
- Browsing sessions: three successful runs, with no wallet-drainer, clipboard-hijack or hidden-form behavior, and a high share of requests going to external hosts.
Regulatory Verification Notes
The homepage gives no verifiable operator, licensing or registration disclosure that would tie the activity of lending, staking or asset exchange to an accountable legal entity. This is a verification gap in its own right. Both ownership and governance opacity apply here, and in this case they compound the active threat detections. Domain registration is through PDR Ltd. (PublicDomainRegistry.com), and the registration record is incomplete as to ownership. No third-party broker or regulatory-database entry corresponds to this domain, which is neutral rather than positive. The valid certificate is domain-validated only, so it confirms encrypted transport and nothing about who runs the site. Evidence:
- Homepage: no named operator, regulator, license or registration number.
- Hosted on AS59692 (IQWEB – IQWeb FZ-LLC, AE).
- TLS certificate issued by YR1 (DV), valid to 2026-12-22, which gives encryption but no organizational validation.
- Registrar: PDR Ltd. d/b/a PublicDomainRegistry.com, with an expiry of 2027-07-02.
What to Verify Next
Before any engagement, the operator's identity should be established through channels independent of this site. That means checking whether any named XRP Ledger DeFi project with this branding exists, and whether that project's officially published domain matches this one. If a legitimate project exists, its social, repository or documentation channels, reached by an independent route, should be checked for a link to this domain. Any claimed licensing should be confirmed with the relevant registry, and official support or contact channels confirmed offline. Because the security feeds list the domain, a fresh reputation re-check should be run before anyone revisits it. A clean result from a later re-check should be treated as sufficient only if the site's identity is also independently verified. Evidence:
- Homepage: the product claims (swap, bridge, staking, lending) provide the entity names to check against official project listings.
- Reputation: the current threat detections must clear before any sensitive interaction is reconsidered.
- Identity: no independent confirmation links the domain to a real-world brand or person.
Summary Verdict
The available evidence points to an elevated-risk website. Active external threat detections dominate the assessment, and the domain's very recent creation and lack of independent history leave nothing to counterbalance them. The site's identity is not verified, and the few neutral technical observations do not change the overall posture.
Infrastructure Integrity
The site resolves to a single server address in the United Arab Emirates, operated by IQWeb FZ-LLC on commodity data-center hosting. No CDN or WAF fronts it, so the origin server is directly exposed and there is no protective layer to mitigate that exposure. The hosting provider's shared address range has received abuse reports. They are attributed to shared infrastructure and are not discounted, but they are secondary to the domain-level detections. The certificate is valid and well within its lifetime, but this is a baseline hygiene feature and offers little assurance on its own.
Closing Assessment
The site should be treated as unsafe for any sensitive interaction. Read-only viewing is the only proportionate use. No logins, credentials, transaction signing or funds should be submitted to it, and nothing should be downloaded from it. Any prior interaction should be reviewed promptly, and the domain should be escalated to the organization's security team for blocking.
Written analysis generated 2026-10-25 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, history in the web archive, behaviour in a sandbox, hosting and network, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
03 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
04 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
05 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 6 reports on hosting IP 186.2.175.35 (IQWeb FZ-LLC, Data Center/Web Hosting/Transit), 11% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of first-ledgers.org.
- The request stayed on first-ledgers.org. It was not redirected to another domain. Clear
- Registration is published under PDR Ltd. d/b/a PublicDomainRegistry.com. Clear
- DNS for this domain is served by regway.com, across 4 name servers. Noted
- The registration is paid up to 2027-07-02. Noted
- The earliest public archive of this site is from 2026-07-06. Clear
- It is hosted on IQWEB, from a server in AE. Noted
Domain intelligence
| Registrar | PDR Ltd. d/b/a PublicDomainRegistry.com |
|---|---|
| Hosting | IQWEB - IQWeb FZ-LLC, AE |
| Country | AE |
| Server IP | 186.2.175.35 |
| Name servers | dns1.regway.com, dns2.regway.com, dns3.regway.com, dns4.regway.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR1 |
| SSL expiry | 2026-12-22 |
| Domain age | 0.32 years (continuous registration) |
| Domain expiry | 2027-07-02 |
| Archive first seen | 2026-07-06 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 12 flagged | AbuseIPDB: 11% confidence, 6 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about first-ledgers.org at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.