Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
flockerztokenclaim.pages.dev shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1.7 years oldRegistered history | Clear |
| Web archive | Archived since 20256 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
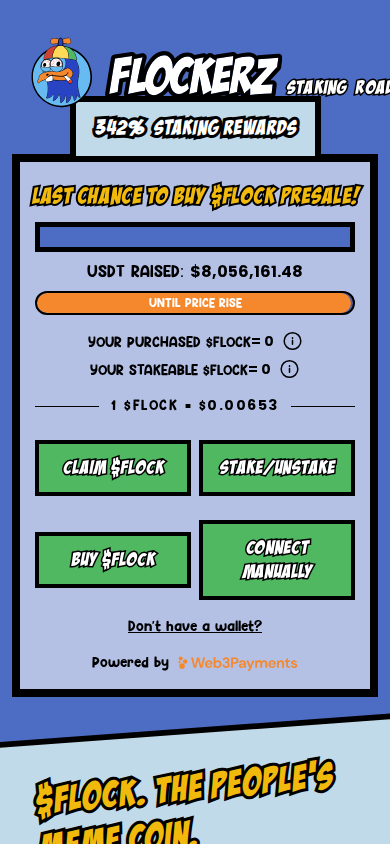
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2025.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
FLOCKERZ is a single-page cryptocurrency promotion hosted on a free subdomain of a shared web-hosting platform, with a token-claim domain name. Its homepage is titled as a "Revolutionary Vote-To-Earn Meme Coin" and a "Crypto Presale". It presents a speculative meme-token offering and appears to monetise by soliciting presale participation or token claims from visitors.
Scam/Impersonation Risk
Hard contradictions are present. The domain is blacklisted: several independent threat-intelligence engines classify it as malicious or suspicious, and a further external blacklist listing corroborates this. The domain's history also carries a recorded phishing association. No conflicting legal entities and no brand impersonation were observed, so the concern rests on reputational and threat-feed evidence rather than on identity inconsistency. The offering's mechanics increase that concern. A claim-style address combined with a presale and a vote-to-earn meme-token proposition is the pattern most often used to draw visitors into token purchases or wallet interactions they cannot reverse. The sandbox did not observe a wallet-connection prompt, a wallet-draining routine, clipboard manipulation, hidden forms or cloaked content, and these absences do not offset the blacklisting. The page did trigger several outbound data submissions, one of which went to an unrecognised third-party destination. It also produced an abnormally large volume of browser errors, which points to an unstable or poorly built front end. Ownership of the domain is opaque, but this is an ownership-visibility limitation and not an identity contradiction. Evidence:
- Homepage: titled as a vote-to-earn meme coin and crypto presale, with about 6,900 characters of promotional text.
- Domain provenance: the domain is ~1.7 years old, with only 6 archive snapshots over a single tracked year (2025-01-30 to 2025-03-25), so the site has a short, thin history.
- Behavioural sandbox: 9 external data-submission requests, 1 to a non-whitelisted destination, and about 75,000 console errors across the capture; no wallet-drainer, clipboard-hijack or cloaking activity was detected.
- Threat intelligence: 3 engines flagged the domain as malicious and 2 as suspicious, and an additional external blacklist listing was confirmed.
Regulatory Verification Notes
No regulator, licence or registered corporate entity is associated with this token offering, and the independent identity assessment could not connect the site to any verifiable real-world operator. An unregistered presale promising returns through a "vote-to-earn" mechanism sits in an area where securities and financial-promotion rules commonly apply. The absence of a verifiable operator therefore removes any recourse for a participant. No third-party broker-reputation record matched this site, so the elevated assessment rests on the threat-intelligence findings above and not on broker reputation. The transport-layer security is technically valid but confers no regulatory or identity assurance. Evidence:
- Homepage: presents a token presale with no operator identity, registration or licensing information that could be independently tied to a legal entity.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by WE1 with domain-only (DV) validation, valid to 2026-12-07, which proves control of the hostname only.
- Decentralised-finance directories: the project is not recognised in the DeFi protocol listing used for cross-checking.
What to Verify Next
Any claim that the token or presale is genuine should be tested through the project's officially announced channels, reached independently of links on this page. The token's contract address and the claimed team should be confirmed against sources unconnected to this site. The relevant financial or securities regulator's warning lists and registers should be checked for the offering. No wallet should be connected and no funds sent while these checks are outstanding. Official support and contact channels should also be confirmed through an independent route. Evidence:
- Homepage: the presale and claim proposition is unsupported by any externally verifiable project record in the evidence reviewed.
- Reputation record: the blacklisting and phishing association should be re-checked after any remediation claim before the site is reconsidered.
- Operator identity: no verified operator exists against which licensing could be confirmed.
Summary Verdict
The site is assessed as high-risk. The blacklisting and phishing association outweigh every technical positive, including the valid certificate and the site's short but continuous archive history. Its legitimacy is unsupported, and the evidence points toward a token-promotion lure and not a verifiable business.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN and WAF, and every observed address is an edge server, so the origin host is not visible. This is a mitigating factor only. The infrastructure is mainstream and carries no abuse history of its own. However, edge-only visibility prevents independent verification of the true host and can mask rapid content changes. It does not offset the reputational findings.
Closing Assessment
Logging in, submitting credentials, connecting a wallet and making any financial transaction on this site should be avoided. At most, it should be viewed read-only, and any download or claim prompt it presents should be refused.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by governance, external reputation, behaviour in a sandbox, registration and ownership.
01 Governance
- A threat feed lists this domain as malicious, and that caps the score whatever the other checks found.Governance
rule:GOV_CRITICAL_BLACKLIST
02 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
03 Behaviour in a sandbox
- The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
04 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of flockerztokenclaim.pages.dev.
- The request stayed on flockerztokenclaim.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2025-01-30. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2fb0 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-07 |
| Domain age | 1.74 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2025-01-30 |
| Archive snapshots | 6 |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about flockerztokenclaim.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.