Verdict
Our checks found nothing pointing to fraud. Ordinary care still applies when you pay or sign in.
infosec.exchange appears legitimate.
- Not Scam: No check found a pattern TrustSniffer associates with fraud. That is a reading of the evidence, not a guarantee.
- Low Risk: The checks found few risk signals.
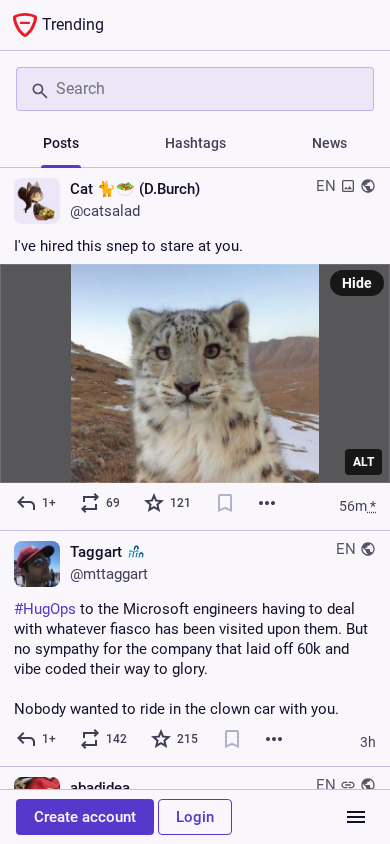
| How the site describes itself | Home page of the infosec.exchange Mastodon instance, showing a public trending feed of posts about Microsoft outage and security topics, with a named administrator, a contact email, privacy and terms pages, and optional donation links. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-13 and re-scored on 2026-11-14. The certificate, the registration age and the page content describe the site as it was on 2026-11-13.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 100/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 4% confidenceAbuseIPDB, 16 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 9.6 years oldRegistered 2017-04-05 | Clear |
| Web archive | Archived since 2022440 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
Key findings
- Automated classification: Not Scam, Low Risk.
- Domain age: 3 to 10 years at capture (registered 2017-04-05).
- Public web-archive history exists since 2022.
- VirusTotal and Google Safe Browsing had no flags for this domain; its hosting IP carries AbuseIPDB reports below the confidence level TrustSniffer treats as a flag.
Full analysis
Overview
Infosec Exchange is a Mastodon-based social network instance for information-security and cyber-security practitioners, part of the decentralised fediverse. Its public landing page shows a trending feed of user posts, here largely commentary on a major Microsoft service outage. The site says it has about 10K active users, is administered by a named individual, and offers free registration. It presents no products, deposits or returns, and the operator asks for optional donations to cover server costs.
Scam/Impersonation Risk
The analysis found no phishing, brand impersonation, confirmed threat listing or malicious-content detection, and no engine flagged the site. The pages read were the explore feed, about, privacy policy, terms, sign-up, sign-in, links directory and the administrator's profile. The site does not sell anything, take deposits, promise returns, or ask for payment data on the pages read. It carries no login or sensitive-data form on its landing page, and its behaviour showed no data going to unrecognised destinations. One soft identity-consistency flag is present. The site's own pages name an administrator and an instance name but no legal entity, and the organisation labels extracted from the pages vary because several are page-title and policy-text fragments. The site's pages do not state two conflicting legal entities, so this reads as an incompleteness in identity labelling rather than a confirmed impersonation. The feed content consists of third-party user posts, which are the posters' own statements and not the operator's claims. The site says it offers "No algorithms, ads, or clickbait", and that statement was not independently tested. The business model fits a donation-supported community instance, with optional donations through Patreon, Ko-fi, Liberapay, Buy Me A Coffee and PayPal.
- Registration record: domain registered in 2017 (about 9.6 years at capture), through the registrar 1API GmbH.
- Web archive: 440 snapshots between 2022-11-15 and 2026-11-09, a span of 1,455 days, with no repurposing detected.
- Landing page and sign-up pages: no payment form, login form or sensitive-data form observed.
- About page: donation requests only, with no pricing, products or return promises.
Regulatory Verification Notes
Infosec Exchange is a non-commercial social platform, so no financial licence is expected. The expected disclosures for this type are a legal entity and terms or privacy documentation. The terms of service and privacy policy are present and linked from the landing page. The privacy policy lists the personal data processed: email address, user ID, password, IP address and metadata. It says processing rests on user consent, and the terms say direct messages are read only for debugging, rule-violation complaints or a valid court order. On the pages read, no legal entity or postal address is named. A named administrator is the only operator identification, and that name is a claim by the site, not a verified fact. The terms also give the instance a royalty-free, perpetual licence over content that users post. This is a standard clause for such platforms, but it matters for anyone posting original work. No third-party regulatory or broker signal was matched for this domain.
- Terms of service: perpetual, royalty-free content licence and prohibitions on harmful or illegal use.
- Privacy policy: lists the categories of personal data processed and the consent basis.
- About and landing pages: administrator named; no legal entity named on the pages read.
- Technical telemetry: TLS certificate issued by YR2 (DV), valid to 2026-12-26; served from AS54113 (Fastly, US).A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "YR2" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site. "Valid to" is the date it expires.
What to Verify Next
The remaining open point is the real-world operator behind the instance. The administrator's named profile can be checked for consistent self-description across the instance's own about page and its linked wiki and status sites. Before donating, the donation destinations should be reached through links published on the instance itself and compared across the platforms listed, so that a payee name appears consistently. Anyone relying on the instance for sensitive security discussion should read the moderation rules and the data-handling terms first, since direct messages are not end-to-end private. The official support route should be confirmed through the instance's own contact page.
- About page: lists the administrator, a contact form and several donation platforms to cross-check.
- Landing page: links to a status site and a wiki that can be used to corroborate the operator.
- Privacy policy: states the conditions under which direct messages may be read.
Summary Verdict
Available evidence is consistent with an established, apparently legitimate community platform. A multi-year domain registration, continuous web-archive history, a top-tier global traffic footprint, a clean threat-intelligence record and an unremarkable content profile support that reading. The real-world operator has not been independently verified, and one soft identity-labelling flag keeps this a calibrated, not unqualified, conclusion. It does not point to scam or impersonation risk.
Infrastructure Integrity
The site sits behind the Fastly content-delivery network, and all eight observed addresses are edge servers, so the origin server was not observed. A CDN is a neutral observation and does not itself support legitimacy. The host address's abuse record was checked: it carries 16 abuse reports with a very low confidence rating. These belong to Fastly's shared provider address and reflect traffic across many unrelated customers, not behaviour specific to this site. The TLS certificate is valid and the encryption is domain-validated only, so it establishes the connection's security and not the operator's identity. The behavioural sandbox runs were stable and returned successful responses.
Closing Assessment
Ordinary use of the platform, including reading, creating an account and posting, is appropriate. Treat the donation links as an optional step to take only once the payee has been confirmed through the instance's own pages. Take the usual care with sensitive content in direct messages, and use a unique password for the account.
Written analysis generated 2026-11-14 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by page content and registration and ownership.
01 Page content
- The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
02 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Certificate and search-engine setup: 2 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 16 reports on hosting IP 2a04:4e42:400::820 (FASTLY), 4% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Trending
- contact:email
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of infosec.exchange.
- The request stayed on infosec.exchange. It was not redirected to another domain. Clear
- Registered through 1API GmbH. Noted
- DNS for this domain is served by dnsimple-edge.org, across 4 name servers. Noted
- The domain is registered until 2027-04-05. Noted
- The earliest public archive of this site is from 2022-11-15. Clear
- It is hosted on FASTLY, a network registered in US. Noted
Domain intelligence
| Registrar | 1API GmbH |
|---|---|
| Hosting | FASTLY - Fastly, Inc. |
| Network registered in | US |
| Server IP | 2a04:4e42:400::820 (a CDN edge address; the server behind it was not observed) |
| Name servers | ns4.dnsimple-edge.org, ns3.dnsimple-edge.io, ns2.dnsimple-edge.net, ns1.dnsimple-edge.com |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 8 |
| Edge IP addresses | 8 |
| Likely origin IP addresses | 0 |
| SSL issuer | YR2 |
| SSL expiry | 2026-12-26 |
| Domain age | 9.61 years (registered 2017-04-05) |
| Domain expiry | 2027-04-05 |
| Archive first seen | 2022-11-15 (4.0 years before capture) |
| Archive snapshots | 440 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 4% confidence, 16 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about infosec.exchange at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.