Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
mc-modhub.vercel.app shows high-risk / scam indicators.
| What this site appears to be | A Minecraft mod download portal (ModHub) listing client-side mods, installation instructions, mod loader guidance, and a small reporting form for users (Discord username input). Content focuses on downloads and installation rather than financial transactions. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 75 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
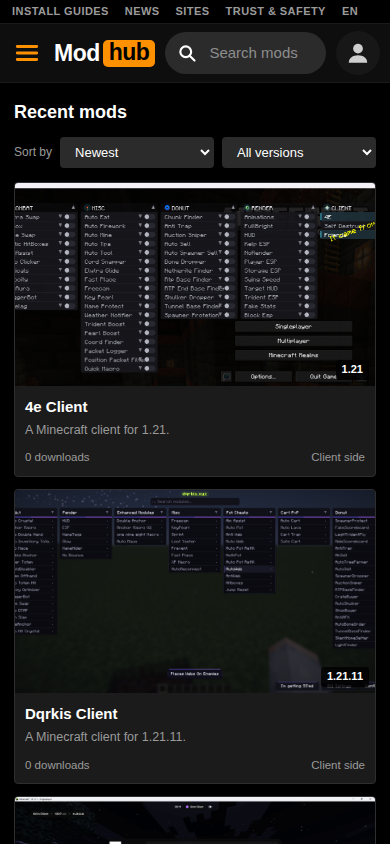
This website is a Minecraft mod download portal branded "ModHub". It presents a catalogue of ten client-side Minecraft clients (4e, Dqrkis, Grim, Krispy, Larp, Water, 67, Clarity, Goobaa and Orchard) targeting game versions 1.21, 1.21.11 and 26.1.2. It also offers installation and mod-loader guides, a Discord community link and a small problem-report form. It takes no payments. Its apparent purpose is to distribute downloadable game software to a community audience, with any revenue presumably indirect.
Scam/Impersonation Risk
The risk here is malware distribution, not deception about identity. A threat-intelligence feed currently lists this site as the actor distributing malware. That finding is decisive and is not offset by the benign appearance of the pages. The listing is corroborated by a confirmed blacklist from several independent reputation engines, three of which rate the site malicious and one suspicious. No brand impersonation, phishing behaviour or conflicting legal identities were observed, so the concern is the content served rather than a false front. This matters because the homepage's core function is to hand out executable client files. The catalogue carries almost no download history (most entries show zero downloads, the rest one), and a "more mods coming soon" notice marks it as a newly assembled, unestablished library. Several entries instruct users to press Right Shift to open an in-game GUI, which means users are asked to run third-party code inside their game. A separate set of 75 abuse reports concerns a shared content-delivery address operated by the hosting platform. Those reports are not attributable to this site and are discounted, so they do not add to the finding. The behavioural analysis of the page recorded no external requests, no wallet interaction, no hidden forms and no cloaking. That shows the landing page itself is quiet, not that the downloadable files are safe. Evidence:
- Homepage: lists ten client downloads with Right Shift GUI instructions, so the executable files are the primary risk surface.
- Threat-intelligence listing: the site is classified as a malware-distribution actor, last observed 2026-10-11, and this is the decisive finding.
- Reputation engines: three malicious and one suspicious detection, plus a confirmed external blacklist.
- Hosting-platform address: 75 abuse reports apply to a shared provider address and are discounted as shared infrastructure.
Regulatory Verification Notes
Licensing is not the issue for a free game-mod portal, so the relevant question is accountability. The site publishes no operator name, legal entity, contact page or terms, and it runs on a subdomain of a shared application-hosting platform, not a domain of its own. These are content gaps in the site itself. Real-world identity has not been independently verified, so no claim of legitimacy can be made. No third-party broker or regulator record exists for the site, and none would be expected. The "Trust & safety" and "Report a problem" navigation entries lead only to the reporting form, which collects a Discord username in a free-text box and gives no information about who reads it or how reports are handled. Evidence:
- Homepage and navigation: no operator, entity or jurisdiction is named anywhere on the page.
- Hosting: served from AS16509 (Amazon-02, Amazon.com, Inc., US) under a shared-platform subdomain.
- Transport encryption: the TLS certificate is a domain-validated one issued by WR1, valid to 2026-11-27, which confirms only an encrypted connection and not the operator's identity.
- Report form: a single textarea collecting a Discord username, with no published handling policy.
What to Verify Next
The malware listing should be checked at its source and not taken from the site's own claims. An analyst should confirm directly with the listing feed which file or path triggered it. They should also determine whether it was removed after the last observation. Any client file obtained from the site should be treated as untrusted. It should only be examined in an isolated environment, and only after comparing its hash against reputable multi-engine scanning results. Prospective users should look for the clients' source code and authors on established mod repositories. They should also confirm official support channels through the project's Discord community or another independent route, not through links on the site. Only a public, independently documented developer identity would justify revisiting this assessment. Evidence:
- Homepage download entries: each client's origin is stated only in a one-line description, with no source repository or author named.
- Navigation: the Discord link and the Requests, Guides and Mod Loaders sections give no verifiable maintainer.
- Listing record: the last-observed date is recent, so the listing is treated as current.
Summary Verdict
The site is assessed as high-risk. An active malware-distribution listing, corroborated by blacklist evidence, outweighs the otherwise unremarkable page content and clean on-page behaviour. The real-world operator remains unverified, and the evidence does not support treating the site as a trustworthy source of software.
Infrastructure Integrity
The site is served through Cloudflare and Vercel, with edge addresses in both networks and a hosting footprint on Amazon's network. Its TLS certificate is valid, with about six weeks of validity remaining. This protective infrastructure is a mitigating factor only. It secures delivery of content but says nothing about what that content is, and it cannot offset an active threat listing.
Closing Assessment
The site should be treated as unsafe for any download, installation or execution of its files. Credentials and personal details, including a Discord username in the report form, should not be submitted. Viewing the pages is the only low-risk use.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by governance, external reputation, page content.
01 Governance
- What the site offers, as described on its own pages, limits how high the score can go until more of it can be verified.Governance
rule:gov_business_model_cap - A threat-intelligence feed currently lists a file on this site as malicious, and that caps the score while the listing is live.Governance
rule:gov_active_threat_listing
02 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
03 Page content
- The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
Signals weighed against the site
- AbuseIPDB: 75 reports on hosting IP 216.198.79.67 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of mc-modhub.vercel.app.
- The request stayed on mc-modhub.vercel.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 216.198.79.67 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 0% confidence, 75 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about mc-modhub.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.