Verdict
mdp.edu.ar is moderately trusted.
Most signals looked ordinary, and some evidence was missing. Read the checks below before you pay or hand over personal details.
| What this site appears to be | Official-looking site for Universidad Nacional de Mar del Plata: institutional pages, news, academic secretary notices, scholarship and grant calls, application instructions and contact emails. Content is in Spanish and focuses on university operations and announcements. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0 reportsAbuseIPDB; shared hosting inflates this count | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
Key findings
- Automated classification: Governance Risk.
- No flags from the reputation services TrustSniffer consulted at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
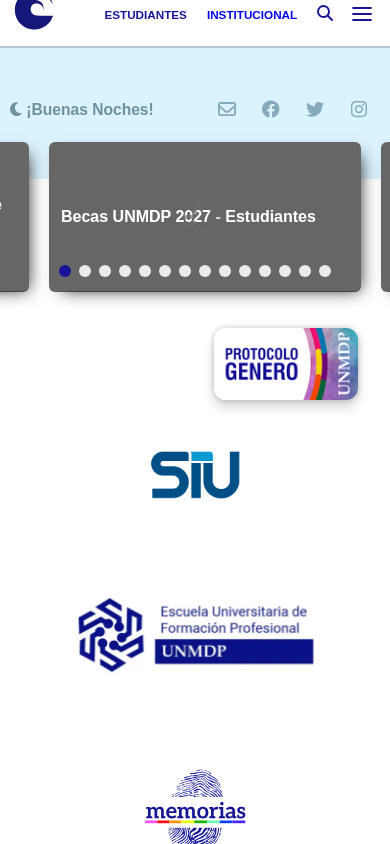
This site presents itself as the website of the Universidad Nacional de Mar del Plata, offering information about university authorities, academic programs, research, scholarships, grants, news, administrative services, and applications. Its apparent purpose is to provide public-facing educational and institutional services rather than direct commercial sales.
Scam/Impersonation Risk
No contradictions were observed, including no confirmed phishing, impersonation, or malicious-content indicators. The homepage and institutional navigation consistently present a university purpose, while the visible content contains no sensitive login form, wallet connection, payment flow, or deceptive commercial offer. External reputation checks recorded no malicious or suspicious detections, and no phishing finding was reported. These signals support an apparently legitimate institutional use case, but the identity-verification status is unverified, so the evidence does not independently establish the real-world operator’s identity. Ownership and governance remain opaque because independent operator information and the on-page disclosure state are incomplete or unclear; these are verification limitations rather than evidence of deception.
- The homepage identifies the Universidad Nacional de Mar del Plata and links to institutional, academic, research, extension, and administrative sections.
- Visible page analysis found no login form, hidden sensitive form, untrusted form destination, wallet activity, or brand-impersonation indicator.
- External reputation evaluation recorded zero malicious and zero suspicious detections, with no phishing finding.
Regulatory Verification Notes
The authorities, history, statute, strategic-plan, academic-secretariat, and administrative pages provide substantial institutional context and consistently present the university as the site’s subject. The site does not present a commercial license number or equivalent regulatory registration disclosure; for an educational institution, that is a status-verification matter rather than evidence of deception. The available identity evidence is consistent with the named university, but independent operator verification remains incomplete because identity verification is unverified. The academic “edu.ar” domain context and institution-associated hosting support continuity, but do not independently prove ownership or legal identity. The unclear on-page disclosure state and governance and ownership opacity therefore remain qualifications on the assessment, not affirmative findings of misconduct. The transport certificate confirms encrypted delivery rather than legal identity.
- The institutional pages include “Autoridades de la Universidad,” “Historia de la Universidad,” “Estatuto de la Universidad,” and “Plan Estratégico 2030.”
- The site uses the academic domain suffix “edu.ar.”
- The site is served from AS27981, Universidad Nacional de Mar del Plata, AR.
- The TLS certificate is issued by YR2, uses Domain Validation (DV), and is valid to 2026-09-30T03:10:39+00:00.
What to Verify Next
Before sensitive or high-value activity, the institution’s legal status and the relevant page-specific contact details should be cross-checked through an independently located Argentine higher-education or government source. Scholarship, grant, enrolment, and application instructions should be matched against notices obtained through an independently confirmed university channel, and any request for credentials, documents, or payment should be validated through an offline or separately sourced contact route. These checks address the unverified identity, unclear disclosure, and ownership and governance opacity noted above; those limitations should not be treated as proof of fraud.
- The site’s authorities, statute, and institutional-history pages provide the primary identity claims to cross-check externally.
- Scholarship, research, and application pages contain operational instructions whose authenticity can be confirmed through independently sourced university channels.
Summary Verdict
The website presents a moderate-trust posture with no observed scam or impersonation contradictions. Its institutional content, technical consistency, and clean external reputation findings support an apparently legitimate use case, while the unverified independent identity, unclear disclosure state, and incomplete governance and ownership picture prevent a fully verified trust conclusion.
Infrastructure Integrity
The site resolves directly to a likely origin rather than through a detected CDN or WAF edge. This means there is no identified third-party edge layer providing additional exposure mitigation, but the hosting arrangement is not itself evidence of malicious activity. The institution-associated hosting signal supports continuity only to the extent that the hosting attribution is accurate; it does not independently verify the operator.
- Infrastructure resolution identified 1 unique IP, 0 edge IPs, and 1 likely origin IP.
- No CDN or detected CDN vendor was present in the hosting configuration.
Closing Assessment
Routine informational use is proportionate, while credentials, personal documents, and high-value transactions should follow independent institutional and legal-status checks before proceeding.
Written analysis generated 2026-08-17 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
1 finding contributed to this verdict, raised by registration and ownership.
01 Governance Risk
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- Identity verified on page
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of mdp.edu.ar.
- The request stayed on mdp.edu.ar. It was not redirected to another domain. Clear
- It is hosted on AS27981, from a server in AR. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AS27981 - Universidad Nacional de Mar del Plata, AR |
| Country | AR |
| Server IP | 170.80.24.6 |
| Name servers | Not available |
| SSL issuer | YR2 |
| SSL expiry | 2026-09-30 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 0 flagged | AbuseIPDB: 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about mdp.edu.ar at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.