Verdict
Most signals looked ordinary, and some evidence was missing. Read the checks below before you pay or hand over personal details.
meme-interface.netlify.app is moderately trusted.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
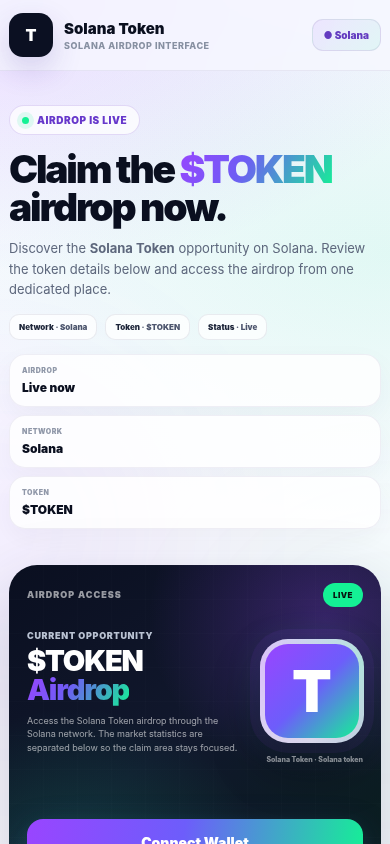
The page as captured
Key findings
- Automated classification: Not Scam.
- VirusTotal and Google Safe Browsing had no flags for this domain; its hosting IP carries AbuseIPDB reports below the confidence level TrustSniffer treats as a flag.
Full analysis
Overview
This website is a single-page Solana-themed landing page titled "Solana Token — $TOKEN Airdrop". It is published on a Netlify-hosted subdomain with an interface-style name. It presents a short block of promotional token content, and its apparent purpose is to promote a meme-token or airdrop campaign. No named operator, product suite, or commercial offering was evident from the captured content.
Scam/Impersonation Risk
No contradictions were observed. The site shows no reputation-list or phishing listing, no brand impersonation, and no conflicting legal identities. Major reputation sources report no malicious detections, and the large majority of engines returned a harmless verdict. The airdrop framing in the homepage title is a theme commonly used as a lure in token-related fraud, so it deserves attention on its own. In this case the sandboxed behavioral runs found none of the mechanics that usually accompany such lures. There were no wallet-connection prompts, no wallet-drainer behavior, and no clipboard manipulation. There were no hidden or externally posting forms, no cloaking, and no fingerprinting. The page also made no third-party requests that would route data or credentials off-site. Its name resembles its hosting platform's domain only because it is a subdomain on that platform, so this is not evidence of impersonation. The only negative signal visible in the data is a pair of abuse reports on a shared edge IP address, covered under Infrastructure Integrity. Page-level identity could not be independently tied to a real-world brand or person, and AI page analysis was unavailable, so identity is unverified. The site's apparent legitimacy is therefore only evidence-consistent, not established. Evidence:
- Homepage: titled as a Solana token airdrop, with a short body of promotional text and no further named products or yield claims captured.
- Behavioral sandbox runs on the homepage: three of three runs completed, with zero wallet-connect, wallet-drainer, clipboard-write, hidden-form, or external-POST events and no cloaking detected.
- Reputation sources: zero malicious and zero suspicious detections, with no safe-browsing flag.
Regulatory Verification Notes
The site is not presented as a regulated financial service, and no licensing or registration claims were captured. No third-party broker or regulatory record matched it, and no external reputational warning is attached to it. Disclosure on the page remains unclear: the captured content does not name an operating entity, a responsible party, or a contact route. This is a verification gap to resolve through independent channels. It is not evidence of wrongdoing, because no contradictions were found. The site's transport security is sound but reflects the hosting platform rather than the site's operator, so it cannot establish who runs the site. Evidence:
- Homepage and captured page text: no operator name, legal entity, jurisdiction, or license or registration reference is stated.
- Transport encryption: TLS certificate issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 at OV validation, with subject organization Netlify, Inc and validity to 2027-03-19.
- Hosting: served from AS16509 (AMAZON-02 - Amazon.com, Inc., US).
What to Verify Next
Before any wallet interaction, token purchase, or claim of an airdrop, the identity behind the campaign should be established independently. The project's token contract address, named team, and official channels should be confirmed through sources that do not link back to this page, such as the issuing project's verified social accounts or an on-chain explorer. Any support or contact route should be confirmed through an independent route before sensitive information is shared. If a claim or connect flow appears later, it should be re-assessed, since this analysis captured only the landing page and the sandbox saw no such flow. Evidence:
- Homepage: the airdrop framing implies a possible claim or connection step, but none was triggered during the sandbox runs.
- Homepage: no on-page token contract reference or team identification was captured to cross-check.
Summary Verdict
The available evidence supports a moderate-trust posture, with limited classification confidence. The captured evidence shows no signs of active threat, deception, or contradictory identity, and the observed behavior is clean and self-contained. The real-world operator is still unconfirmed and identity is unverified, so the site reads as apparently legitimate on the evidence available, not as verified.
Infrastructure Integrity
The site is delivered through AWS-backed edge infrastructure on a mainstream hosting platform, a trusted and well-established provider. All observed addresses are edge nodes, and no origin address was observable, which limits independent verification of the underlying host. This protective layer is a mitigating factor only and does not prove legitimacy. Two abuse reports exist against one of the shared edge addresses (2a05:d014:58f:6200::259), which belongs to Amazon Data Services Ireland Ltd and is classed as Content Delivery Network usage. The address is not whitelisted. The reports are attributed to shared infrastructure: they apply to the provider's shared network IP, not to this site. They also carry a confidence score of 0. For both reasons they have been discounted as a signal about the site. They remain visible here for transparency.
Closing Assessment
Reading the page and ordinary browsing are reasonable. Wallet connections, token purchases, and any high-value financial action should wait until the project's identity has been confirmed independently.
Written analysis generated 2026-10-22 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by behaviour in a sandbox, registration and ownership.
01 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
02 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (Amazon Data Services Ireland Ltd, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of meme-interface.netlify.app.
- The request stayed on meme-interface.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:58f:6200::259 |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 flagged | AbuseIPDB: 0% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about meme-interface.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.