Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
modhollow.netlify.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: a threat-intelligence listing limits the score; as a site on netlify.app, this address has no registration record of its own (the platform's domain is registered, not the site). The findings below give the detail.
| How the site describes itself | A small Minecraft mod database (ModHollow) listing a handful of Fabric mods with direct jar download links and minimal descriptive text. No login, payment, or credential collection present. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-10 and re-scored on 2026-11-03. The certificate, the registration age and the page content describe the site as it was on 2026-10-10.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Threat-listing ceilingA threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score. | Risk |
|---|---|---|
| Malware engines | 3 marked it maliciousVirusTotal | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 1% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
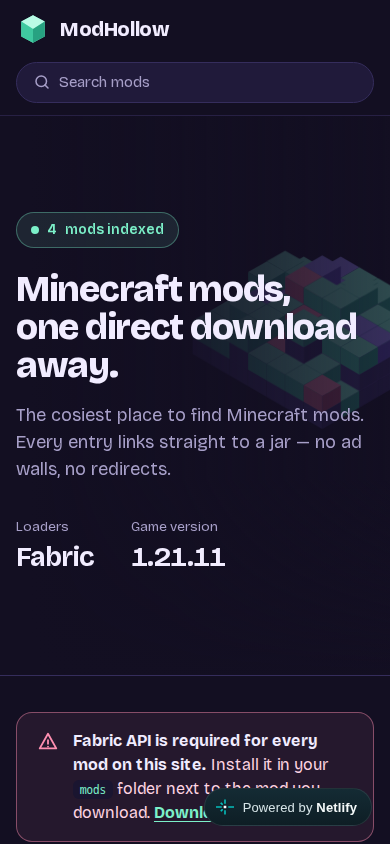
ModHollow is a small Minecraft mod catalogue published as a subdomain on a shared site-hosting platform. It presents four Fabric mods for game version 1.21.11, each with a direct jar download button, and promises "no ad walls, no redirects". It has no login, storefront, subscription or deposit flow. Its apparent purpose is free distribution of executable mod files to players, and no monetization is visible.
Scam/Impersonation Risk
The page itself shows no phishing mechanics, brand impersonation or conflicting legal identities, and a behavioral sandbox observed no external requests, hidden forms, cloaking or credential collection. The decisive concern is external. A threat-intelligence feed currently lists this site as distributing malware, and several independent reputation engines flag it as malicious or suspicious, which amounts to a confirmed blacklisting. Infrastructure protections cannot offset that listing. The product profile makes the listing credible. The site's only function is to hand visitors executable jar files that load directly into the game client. Those files include a loader credited to "Unknown", a "utility" client mod, and a mod that advertises "advanced client brand spoofing". The catalogue shows a download counter of zero and carries no code provenance, checksums or source repositories, so a visitor cannot independently confirm that a file is the genuine upstream build. A minor point on shared reputation: two abuse reports exist against an address belonging to the hosting provider's shared network. They are weak on their own and carry little weight beside the malware listing.
- Homepage: four mods indexed, each with a direct jar download. The listed sizes range from under 1 MB to about 5.6 MB, and "by Unknown" appears on one entry.
- Homepage mod descriptions: one entry advertises client brand spoofing and tracking-exploit features, and three entries state they require a separate core API to be installed alongside them.
- Behavioral sandbox, three successful runs: no external posts, no wallet or clipboard activity and no password forms, so the risk sits in the downloadable files and not in page-level deception.
- External reputation: the site is currently listed for malware distribution (last observed 2026-10-10), and three engines return a malicious verdict with one more suspicious.
Regulatory Verification Notes
The site is a subdomain of a shared hosting platform, so the domain itself says nothing about who operates it. The homepage names no operator, legal entity, contact route, terms or privacy page, and no outbound links, and the operator's real-world identity is unverified. This is ownership opacity, not an identity contradiction, because no conflicting legal names appear. No licence or registration is claimed. For a file-download site that would normally not be expected, so the point carries little weight. The legitimate-looking technical signals that are present, a valid organization-validated certificate and mainstream cloud hosting, belong to the platform and not to the site's operator. They do not offset the malware listing. No broker-reputation match was found.
- TLS certificate issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 (OV) to Netlify, Inc, valid to 2027-03-19. It identifies the platform and not the site's operator.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "DigiCert Global G2 TLS RSA SHA256 2020 CA1" is the name of the authority that issued it. OV (organization validated) means the issuer also checked the organization that runs the site. "Valid to" is the date it expires.
- Served from AS16509 (AMAZON-02, Amazon.com, Inc., US), registry ARIN.
- Homepage: no company name, contact page, legal pages or operator attribution.
What to Verify Next
Verification here is about the files, not the operator's identity. Each mod should be traced to its upstream project and author through an independent, official channel and not through this site, because the site provides no provenance. Any jar already downloaded should be scanned and compared against the upstream publisher's checksum. The game client should also be checked for unexpected mods or changed behavior. The listing status should be rechecked later, because it would only clear after the hosted files are cleaned or removed.
- Homepage: download entries show a version and size only. They give no checksum, source repository or signing information.
- Homepage: the site names upstream authors for some mods, which allows direct comparison with their official distribution points.
- External reputation: the malware listing was last observed on 2026-10-10 and remains active.
Summary Verdict
The site carries an elevated risk posture. The page looks benign and harmless on the surface, but an active malware-distribution listing and multiple malicious detections outweigh that appearance. The operator's identity is unverified and cannot be used to reassure.
Infrastructure Integrity
The site resolves to Amazon-hosted infrastructure in the United States, behind a mainstream content-delivery layer. All observed addresses are edge servers, including Cloudflare addresses, and no origin address could be observed. Edge-only visibility prevents independent confirmation of where files are actually stored and can mask a rapid swap of hosted content. This protective infrastructure is a mitigating factor only and does not reduce the reputation risk.
Closing Assessment
Nothing should be downloaded from this site, and its jar files should not be installed, until the malware listing is cleared. Mods should be obtained from the original authors' official distribution channels. Any file already obtained from here should be removed and the device scanned.
Written analysis generated 2026-11-03 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by governance, external reputation, page content, and registration and ownership.
01 Governance
- A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score.Governance
rule:gov_active_threat_listing
02 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
03 Page content
- The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
04 Registration and ownership
- As a site on netlify.app, this address has no registration record of its own (the platform's domain is registered, not the site).Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (AMAZON-02), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of modhollow.netlify.app.
- The request stayed on modhollow.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 2a05:d014:58f:6200::259 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (aws, cloudflare) |
| Resolved IP addresses | 8 |
| Edge IP addresses | 8 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on netlify.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 3 malicious | AbuseIPDB (CDN edge address, not the host): 1% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about modhollow.netlify.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.