Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
moonshot-dex.net shows high-risk / scam indicators.
| What this site appears to be | Moonshot DEX presents itself as a non-custodial Solana DEX offering token swaps, concentrated liquidity pools, cross-chain bridging, SOL/MNST staking and governance. It promotes 'real yield' and APYs, and lists five audit firms and a $10M bug bounty. The security and yield claims are not independently verifiable from the page and contain internal contradictions, so the page is rated high-risk for yield-related structural reasons rather than for fraud signals. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 9 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 12% confidenceAbuseIPDB, 5 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
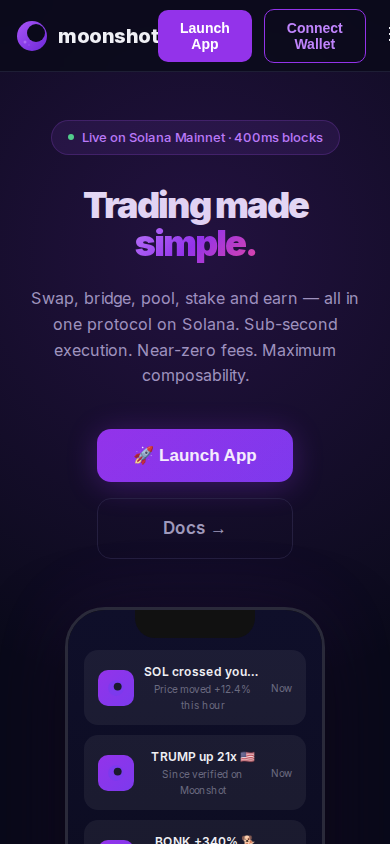
Moonshot DEX is a single-page landing site for a self-described non-custodial decentralised exchange on Solana. It markets itself as the "#1 Solana DEX" and presents token swaps, concentrated liquidity pools, a cross-chain bridge, SOL and MNST staking and vaults, and governance. Its apparent business model combines a 0.04% base swap fee and pool fee tiers of 0.01% to 0.25% with yield-bearing staking products and token-reward and referral incentives, all steered toward a wallet-connect and app-launch flow.
Scam/Impersonation Risk
The evidence shows confirmed contradictions. The domain is currently blacklisted: several major security vendors flag it as malicious or suspicious, and an external blacklist corroborates this. The hosting address also carries recent abuse reports. Those reports relate to a shared data-centre provider address, so they are weaker evidence than the domain-level detections, but they point the same way. No brand impersonation, phishing form, wallet-drainer behaviour, clipboard hijacking or cloaking was observed in the browser sandbox, and no identity conflict between legal entities was found, so the concern rests on reputation, the site's age and the promotional model. The homepage's own claims conflict with each other. It asserts "No admin keys" while describing a 5-of-7 multi-signature upgrade process. It claims "No emissions inflation" while attaching MNST token rewards to every pool. It invites visitors to "Join 2M+ users" next to a counter of 420K+ unique wallets. It also advertises $4.8B in total volume and $640M in value locked with no way to verify either figure. Staking and pool yields of 7.2%, 18.5% and 12.1% APY and a 31.4% top-pool APR are the core of the offer, which makes the site a deposit-before-service proposition built on unverifiable yield promises. Social-proof pop-ups such as "TRUMP up 21x" and "BONK +340%", plus a lineup of 13 named tokens, add engineered urgency typical of speculative crypto promotion. Evidence:
- Homepage: the "No admin keys", "No emissions inflation" and "2M+ users" claims are contradicted by the 5-of-7 multi-sig description, the per-pool MNST rewards and the 420K+ wallets counter.
- Homepage: staking and pool returns of 7.2%, 18.5%, 12.1% APY and 31.4% APR sit beside hype notification widgets and referral and reward incentives.
- Domain provenance: registered 2026-07-30 through Atak Domain (~0.22 years old), with 1 archive snapshot in 2026 (1 year tracked) and no earlier history.
- Reputation: nine malicious and three suspicious engine verdicts, plus 5 abuse reports against the shared hosting IP 186.2.175.35.
Regulatory Verification Notes
The homepage names no operating company, jurisdiction, registration number or licence, and the risk disclaimer it links to does not make up for that. Its security assurances are asserted rather than demonstrable. It lists five audit firms and a $10M bug bounty, but offers no links to audit reports, no program or contract addresses, and no bug-bounty platform reference. The "Docs" and risk-disclosure links give no verifiable evidence of who runs the protocol. Real-world operator identity therefore remains unverified, and the site's non-custodial status cannot be independently confirmed. No third-party broker or regulatory-database match was found, which leaves this as a verification gap rather than a regulatory finding. Evidence:
- Homepage: no legal entity, licence or registration details, and no audit report links or contract addresses.
- Transport layer: a domain-validated TLS certificate issued by YR1, valid to 2026-10-28, which confirms encryption only and says nothing about the operator.
- Hosting: served from AS59692 (IQWEB - IQWeb FZ-LLC, AE) under the RIPE registry, with a country and registry mismatch noted.
What to Verify Next
Any audit or bug-bounty claim should be checked directly with the named audit firms and bounty platform through channels the site does not control. The protocol's program and contract addresses should be located in an independent on-chain explorer, and checked for deployed code, upgrade authority and any admin or multi-sig control. The identity of the operating entity should be established from an independent registry or established third-party sources. The official social and community channels should be confirmed through an independent route rather than through links on this page. Because the site is blacklisted, it should not be reconsidered until the external detections are cleared by the flagging vendors. Evidence:
- Homepage: audit firms and a $10M bounty are named but not linked to any report or program.
- Homepage: the MNST token and the "veMNST" governance mechanics have no contract reference to check.
- Social presence: Twitter, Discord, Telegram and Medium are referenced without verifiable official-channel confirmation.
Summary Verdict
Available evidence supports a high-risk posture. Active third-party detections, a very young domain, unverifiable and internally inconsistent claims, and a yield-led deposit model converge on an elevated risk assessment that the absence of observed phishing mechanics does not offset. The site's operator identity remains unverified, and the technical hygiene it does show is insufficient to support trust.
Infrastructure Integrity
The site is served from a single IP at a UAE-registered hosting provider, IQWeb FZ-LLC, with no CDN or WAF in front of it, so the origin address is directly exposed and no protective layer mitigates the reputation risk. The transport certificate is valid, but it is domain-validated only and close to expiry. Heuristics flag a registry and country mismatch and a thin footprint of subdomains for such a young domain. These are unconfirmed and secondary to the confirmed external detections.
Closing Assessment
The site should be treated as read-only at most. Wallet connection, login, credential entry and any deposit, swap or staking transaction should be avoided until the external detections are cleared and the protocol's identity and contracts are independently verified.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, history in the web archive, page content, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
03 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
04 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
Signals weighed against the site
- AbuseIPDB: 5 reports on hosting IP 186.2.175.35 (IQWeb FZ-LLC, Data Center/Web Hosting/Transit), 12% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of moonshot-dex.net.
- The request stayed on moonshot-dex.net. It was not redirected to another domain. Clear
- Registration is published under Atak Domain. Clear
- DNS for this domain is served by trustname.com, across 2 name servers. Noted
- The registration is paid up to 2027-07-30. Noted
- The earliest public archive of this site is from 2026-07-31. Clear
- It is hosted on IQWEB, from a server in AE. Noted
Domain intelligence
| Registrar | Atak Domain |
|---|---|
| Hosting | IQWEB - IQWeb FZ-LLC, AE |
| Country | AE |
| Server IP | 186.2.175.35 |
| Name servers | ARES.TRUSTNAME.COM, ZEUS.TRUSTNAME.COM |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR1 |
| SSL expiry | 2026-10-28 |
| Domain age | 0.22 years (continuous registration) |
| Domain expiry | 2027-07-30 |
| Archive first seen | 2026-07-31 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 9 flagged | AbuseIPDB: 12% confidence, 5 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about moonshot-dex.net at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.