Verdict
nebula-client.org is low-trust and potentially risky.
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
| What this site appears to be | Site offering a free cracked NebulaClient (Fabric 26.2 / 1.21.11) for Hypixel SkyBlock with automation macros and an 'AURA' anti-staff detection system. Provides download links, feature descriptions, installation instructions, FAQs and user testimonials. Claims of near-100% anti-detection and guaranteed uptime are unverified and risky. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0 reportsAbuseIPDB; shared hosting inflates this count | Noted |
| Domain age | 7 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 2026Public history exists | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
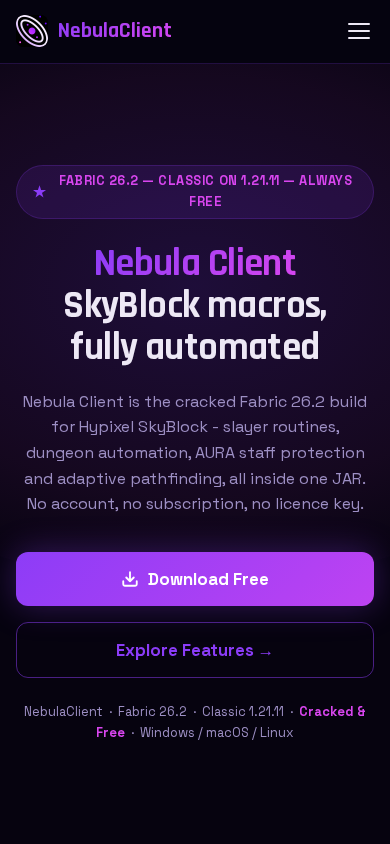
The website presents itself as a download portal for a cracked NebulaClient Fabric build for Minecraft 1.21.11 and Hypixel SkyBlock. It promotes automated gameplay functions, including slayer, dungeon, farming, mining, and fishing macros, together with an “AURA” system described as protecting users from staff detection; its apparent purpose is to distribute rule-violating software free of charge.
Scam/Impersonation Risk
The site presents a materially elevated security risk. Its homepage and download materials promote a cracked client contained in a single JAR, automated gameplay, and an “AURA” mechanism that claims a 99% detection rate, adaptive movement, and near-undetectability. These claims are unsupported by evidence on the site and are inconsistent with the nature of the software being distributed. External security assessment identified malicious and suspicious detections, including a confirmed blacklist status, which is the principal contradiction affecting the site’s trust posture. No conflicting legal-entity names or direct brand-impersonation finding were supplied, but the blacklist and malicious detections independently justify treating downloads and other sensitive interaction as unsafe.
- The homepage describes “Nebula Client Cracked,” a free Fabric 26.2 client for Minecraft 1.21.11, with automation macros and an “AURA” staff-protection feature.
- The features and download pages claim a 99% detection rate, live-generated movement, and protection against anti-cheat detection without presenting supporting validation.
- External reputation checks recorded 2 malicious detections, 1 suspicious detection, and a confirmed blacklist finding.
Regulatory Verification Notes
The legal, privacy, and terms areas do not establish a verifiable operating entity, licensing basis, or accountable commercial relationship for the software. The site’s stated model is free distribution of cracked software, with unclear monetization and no clear product ownership or legal status presented in the supplied content. This is a significant disclosure gap rather than a separate identity contradiction, but it leaves the operator and any responsibility for the distributed JAR unverified. The domain is also very recently registered, which provides little established operating history. A valid transport certificate confirms encrypted delivery only; it does not validate the operator, software safety, or legal standing.
- Domain registration records show creation on 2026-09-17, with an age of 0.02 years, through Internet Domain Service BS Corp.
- Historical records show 11 archive snapshots spanning 2026–2026, with 1 year tracked.
- The site is served through AS214351, identified with FEMOIT - FEMO IT SOLUTIONS LIMITED, GB; the technical registry is AFRINIC and the network country is SC.
- The site uses a DV TLS certificate issued by YR1, valid until 2026-12-23.
What to Verify Next
Before any interaction beyond passive review, an enterprise or individual should independently confirm whether the software has an identifiable publisher, obtain the file only through a trusted and independently authenticated channel, and submit any downloaded artifact to organizational malware and sandbox controls. The legal, privacy, and terms pages should be checked for a responsible entity and enforceable contact route; where those details are absent, the software should not be introduced into an enterprise environment. Any claimed relationship with Minecraft, Fabric, Hypixel, or other named services should be confirmed through those services’ official channels rather than through links or testimonials on this site.
- The download page provides installation instructions for a JAR-based client and promotes operation on Windows, macOS, and Linux.
- The legal, privacy, terms, FAQ, and version-archive pages are linked from the site but do not, in the supplied evidence, establish a verifiable operator.
- The site contains no login form or sensitive web form, but its principal interaction is the delivery of downloadable software.
Summary Verdict
The website has a low-trust posture with a high likelihood of unsafe interaction involving downloaded software. The available evidence does not independently verify the operator and contains converging content, reputation, and provenance concerns that outweigh the site’s basic technical availability. Sensitive interaction, credential use, and financial engagement are not appropriate.
Infrastructure Integrity
Cloudflare CDN and WAF protection are present, and the observed address is a CDN edge address rather than an independently verified origin. This provides a measure of exposure reduction at the network edge, but it does not establish legitimacy or offset the site’s external security detections.
- Cloudflare is identified as the CDN/WAF provider, with 1 observed edge address and 0 identified origin candidates.
- The observed edge address is 196.251.107.204 on AS214351.
Closing Assessment
The proportionate action is to restrict the site to controlled, read-only review and prevent downloads or execution of its software on production, personal, or organizational systems. Any required investigation should use isolated analysis infrastructure and independently sourced verification.
Written analysis generated 2026-09-25 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by registration and ownership, analysis engine.
01 Governance Risk
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
02 Sensitive Interaction Risk
- The analysis matched a pattern TrustSniffer treats as a direct threat to a visitor.Analysis engine
signal:direct_threat
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of nebula-client.org.
- The request stayed on nebula-client.org. It was not redirected to another domain. Clear
- Registration is published under Internet Domain Service BS Corp. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-17. Noted
- The earliest public archive of this site is from 2026-09-18. Clear
- It is hosted on FEMOIT, from a server in SC. Noted
Domain intelligence
| Registrar | Internet Domain Service BS Corp |
|---|---|
| Hosting | FEMOIT - FEMO IT SOLUTIONS LIMITED, GB |
| Country | SC |
| Server IP | 196.251.107.204 |
| Name servers | andy.ns.cloudflare.com, brenna.ns.cloudflare.com |
| SSL issuer | YR1 |
| SSL expiry | 2026-12-23 |
| Domain age | 0.02 years (continuous registration) |
| Domain expiry | 2027-09-17 |
| Archive first seen | 2026-09-18 |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about nebula-client.org at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.