Verdict
nginx.org appears legitimate.
Our checks found nothing pointing to fraud. Ordinary care still applies when you pay or sign in.
| What this site appears to be | Official NGINX project page providing news, release notes, documentation and links to related projects; mentions enterprise distributions and F5 commercial support. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0 reportsAbuseIPDB; shared hosting inflates this count | Noted |
| Domain age | 22 years oldRegistered history | Clear |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
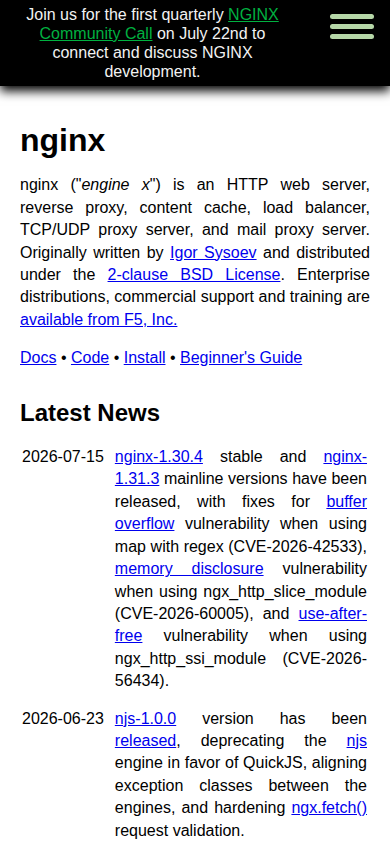
Key findings
- Automated classification: Not Scam.
- Domain age: more than 10 years (registration continuity).
- No flags from the reputation services TrustSniffer consulted at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
The website is the NGINX project site, presenting an open-source HTTP web server and related projects through release information, security notices, documentation, downloads, community resources, and links to enterprise support and training. Its apparent business model is informational and project-oriented, with commercial services associated with F5 rather than direct consumer transactions.
Scam/Impersonation Risk
No contradictions were observed: there are no reported phishing, impersonation, malicious-content, or blacklist indicators in the supplied evidence. The homepage content is technically specific and consistent with an established open-source project, describing NGINX as a web server, reverse proxy, cache, load balancer, TCP/UDP proxy, and mail proxy, while also presenting release and vulnerability-fix information. A dynamic assessment did record hidden form elements in both test runs; however, the rendered page showed no login form, no sensitive form, and no external password submission. This is a limited implementation anomaly rather than evidence of impersonation, particularly because the page otherwise presents a coherent documentation and project profile. The real-world operator linkage remains independently unverified, so the apparent legitimacy of the site should not be treated as proof of a specific legal operator.
- Domain registration: nginx.org was registered on 2004-12-23 and is approximately 21.66 years old.
- External reputation checks recorded 0 malicious and 0 suspicious detections, with no phishing or blacklist finding; the domain’s traffic position was 84.
- The homepage is labelled “nginx” and contains project-specific documentation, release, security, and community content; dynamic testing recorded hidden forms in 2 of 2 runs but 0 external password forms.
Regulatory Verification Notes
The site’s disclosed activity is an open-source software project rather than a financial, investment, or other regulated consumer service. The homepage states that NGINX is distributed under the 2-clause BSD License and that enterprise distributions, commercial support, and training are available from F5, Inc. These statements provide a coherent commercial and technical context, but the available evidence does not independently verify the real-world operator or the corporate relationship beyond the site’s own presentation. No separate regulatory licensing conclusion is warranted from this website profile; any commercial engagement should therefore be assessed as a software-service relationship rather than assumed to carry a regulated-service status. The high page-authority and established traffic signals support the site’s apparent maturity but do not independently establish legal ownership.
- Homepage: identifies the NGINX project, describes the 2-clause BSD License, and attributes enterprise distributions, commercial support, and training to F5, Inc.
- Transport security: TLS certificate issued by YE2 using Domain Validation (DV), valid to 2026-10-17T09:12:13+00:00.
- Hosting telemetry: served from AS16509, Amazon.com, Inc. (AMAZON-02 - Amazon.com, Inc., US).
What to Verify Next
Before any credential or payment interaction associated with a commercial service, independently confirm the responsible legal entity and the applicable support or purchasing channel through an established corporate route. For enterprise procurement, verify the stated F5 relationship, contractual counterparty, service terms, refund or cancellation provisions where applicable, and payment protections before committing funds. Security-sensitive downloads should be obtained through the project’s documented download and security pages and checked against the project’s published release information.
- About, enterprise, and project pages: use the site’s stated project and commercial-service descriptions as the basis for independent corporate-identity confirmation.
- Download and security pages: compare software obtained there with the corresponding release and security information before deployment.
- Any future account or payment workflow: perform an independent merchant-identity, service-terms, and payment-protection check before submission of credentials or funds.
Summary Verdict
Available evidence is consistent with an established, apparently legitimate website and supports a high-trust, low-risk posture for its stated project and documentation purpose. The conclusion is strong at the site-risk level, while independent verification of the real-world operator remains incomplete.
Infrastructure Integrity
The website is protected by AWS CDN/WAF infrastructure, with all observed addresses associated with CDN edge service and no origin candidates identified in the analysis. This reduces direct exposure of the underlying service and is a meaningful mitigating control, but protective infrastructure alone is not proof of legitimacy.
Closing Assessment
Normal browsing and project-documentation use is proportionate to the assessed posture; ordinary independent identity, service-term, and payment-protection checks should be completed before any credentialed or paid interaction.
Written analysis generated 2026-08-16 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
No rule findings contributed to this verdict.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of nginx.org.
- The request stayed on nginx.org. It was not redirected to another domain. Clear
- Registration is published under CSC Corporate Domains, Inc.. Clear
- DNS for this domain is served by f5clouddns.com, across 2 name servers. Noted
- The registration is paid up to 2026-12-23. Noted
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | CSC Corporate Domains, Inc. |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:5c0:2601::6 |
| Name servers | ns1.f5clouddns.com, ns2.f5clouddns.com |
| SSL issuer | YE2 |
| SSL expiry | 2026-10-17 |
| Domain age | 21.66 years (continuous registration) |
| Domain expiry | 2026-12-23 |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 0 flagged | AbuseIPDB: 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about nginx.org at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.