Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
ozakaipresale.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site) and a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
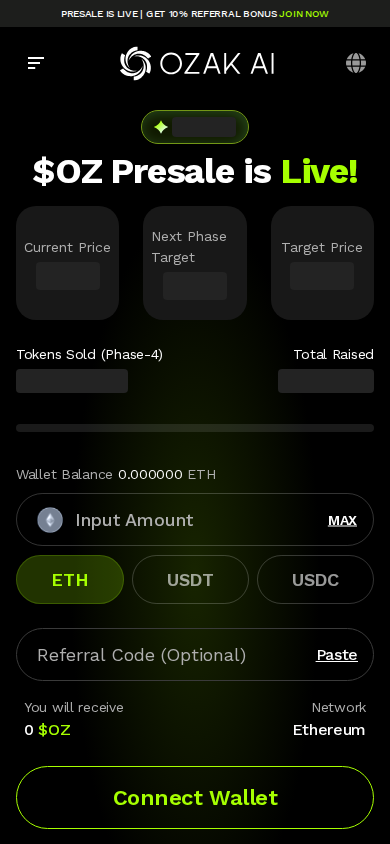
| How the site describes itself | OZAK AI promotes a presale of its $OZ token on Ethereum, paid in ETH, USDT or USDC through a connected wallet, with a 10% referral bonus, early-bird return claims, and a claimed but contradictory CertiK audit. The page provides no verifiable legal identity or company address and urges immediate purchase. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-04 and re-scored on 2026-11-05. The certificate, the registration age and the page content describe the site as it was on 2026-11-04.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 13 months before captureWeb archive; a site on pages.dev has no registration of its own | Risk |
| Web archive | Archived since 20254 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: less than 1 year before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2025.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
The website is a single-page token presale landing page for "OZAK AI", branded as "Your Intelligent Investment Assistant". It invites visitors to buy a token called $OZ on the Ethereum network, paying in ETH, USDT or USDC through a connected crypto wallet. Its apparent business model is raising funds from retail buyers ahead of a token launch, supplemented by a referral scheme that pays existing buyers a bonus for recruiting new ones.
Scam/Impersonation Risk
The assessment is high risk, with confirmed contradictions. Several independent threat-intelligence sources currently flag the site, and the site is blacklisted by external reputation sources. This is a hard reputational signal rather than an inference from content. The page content reinforces it. The homepage promises "early-bird returns" ("Early birds make most of the returns"), advertises staking yield and a 10% referral bonus, and pushes urgency with "Presale is ending soon. Don't miss." The page says a security audit by a named auditor is complete while also stating it is still in progress, and that internal contradiction undermines the credibility of the main assurance offered to buyers. The page also tells visitors to bookmark the "official" site to avoid phishing copies. Nothing independent corroborates that the site is the official project, and it runs on a free subdomain of a hosting platform rather than a dedicated, project-owned domain. The purchase form, which collects the wallet connection and payment amount, was assessed as posting to a destination outside the trusted set. The sandbox also recorded a large volume of third-party requests, including several posts to non-whitelisted endpoints, and repeated script errors. No wallet-draining, clipboard-hijacking or hidden-form behaviour was observed in the sandbox runs, and no brand impersonation or conflicting legal identities were established. These absences do not offset the blacklist signal or the structure of the offer, which asks for crypto payment up front in exchange for a token that does not yet exist on-chain.
- Homepage: presale panel accepting ETH, USDT and USDC on Ethereum, with "Connect Wallet", "Claim $OZ" and "Claim Rewards" controls and a "Refer & Earn 10%" section.
- Homepage: the audit statement contradicts itself, claiming completion and in-progress status at the same time. The "Presale is ending soon. Don't miss." call to action creates purchase pressure.
- Sandbox behaviour: 45 external XHR calls and 24 external POSTs, of which 3 POSTs went to non-whitelisted destinations. 18 console errors were logged and no wallet-drainer activity was detected.An XHR request is a request the page sends in the background while it is open, to load or send data without reloading. "External" means it went to a different website than the one you opened. A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- External reputation: two threat-intelligence engines rated the site malicious and one rated it suspicious, which produces the confirmed blacklist signal.
Regulatory Verification Notes
The site names no legal entity, company address, registration number or licence. For a product marketed as an "investment assistant" and a token sale to the public, this is a material disclosure gap. The terms, user consent agreement and disclaimers are referenced only as links in the purchase flow, and the page offers no operator identity behind them. Ownership and governance are opaque, so the operator cannot be tied to any accountable real-world party. The site claims no regulatory authorisation, and no regulated status was found. The domain is very young, and its limited web-archive history began only shortly before the analysis. The TLS certificate is valid but is only a basic domain-validated one, which proves control of the domain and not the identity of the operator.
- Homepage: no company name, registered address, regulator reference or licence number appears anywhere on the page.
- Domain provenance: registered about 153 days earlier (~0.4 years old), with 4 archive snapshots spanning 2025–2026 (first seen 2025-09-22, last seen 2026-06-16).
- Transport security: TLS certificate issued by WE1 (DV level), valid to 2027-01-20.
- Hosting: served from AS13335 (Cloudflare, Inc., US). DeFi protocol directories do not list the project.
What to Verify Next
Before any interaction, the project's existence and claims should be checked through channels the page does not control. The audit should be confirmed on the named auditor's own published reports, not through the site's badge or text. Any claim of a token contract address should be checked on a public blockchain explorer after launch. The offering's legal status should also be checked with the securities or financial regulator in the buyer's jurisdiction. The official project channels should be located independently, and an offline route should be used to confirm they actually point to this site.
- Homepage: the token contract is described as not deployed until the token generation event, so no on-chain contract can currently be inspected.
- Homepage: the referral section shows "Your Referral Code: NA" and ties rewards to recruiting further buyers.
- Homepage: no outbound links to social channels, documentation or an auditor's report were detected, so no independent path to the project is offered.
Summary Verdict
The available evidence places this site in a high-risk, untrusted category. Confirmed external threat flags, an unaccountable operator and a prepayment token-sale model combine into a pattern consistent with advance-fee crypto fundraising schemes. Neither the apparent technical hygiene of the page nor the sandbox's failure to detect wallet-draining code is enough to support any positive assessment.
Infrastructure Integrity
The site is served behind Cloudflare's CDN and WAF, and all four observed addresses are edge servers. The origin server was not observable, so hosting cannot be independently verified, and content can be changed quickly without any visible change in hosting. The platform-level protection and a valid certificate are only mitigating factors. They do not offset the external threat detections or the risks in the offer.
Closing Assessment
Wallet connections, token purchases, credential entry and any transfer of funds should be avoided entirely, and the page should be treated as a browse-only resource. A wallet that has already interacted with the site should have its token approvals reviewed and revoked.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation and page content.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of ozakaipresale.pages.dev.
- The request stayed on ozakaipresale.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2025-09-22. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2fb1 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-20 |
| First seen (web archive) | 0.42 years before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2025-09-22 (1.1 years before capture) |
| Archive snapshots | 4 |
| Reputation | VirusTotal: 2 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about ozakaipresale.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.