Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
polksvo.vercel.app shows high-risk / scam indicators.
| What this site appears to be | Russian-language page claiming to be an official Ministry of Defense registry for missing persons / service members. Provides search UI copy and explicit step-by-step instructions to download and install a file (including enabling installations from unknown sources). No contact details, provenance, or verifiable credentials are present in the provided content. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 6 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 57 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
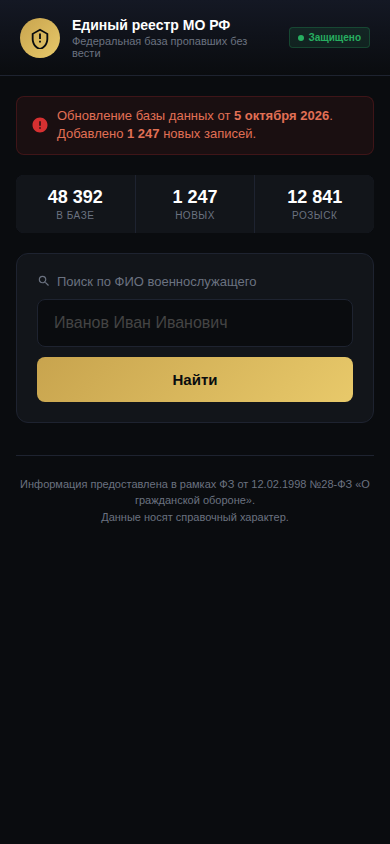
This website presents itself in Russian as the "Unified Registry" of the Russian Ministry of Defense, a federal database of missing persons and service members, with a search-by-name box. Its practical function is to walk visitors through downloading and installing a file, so it reads as a software-distribution lure dressed up as an official public registry. It shows no monetization model.
Scam/Impersonation Risk
Confirmed contradictory signals are present. Multiple independent security engines, including several top-tier vendors, currently flag the site as malicious, and this is a confirmed blacklist condition. No brand-impersonation or phishing-form behaviour was detected, and no conflicting legal identities appear. The risk comes from the combination of an authoritative-sounding state identity and an installer prompt. The homepage asserts a federal registry status, cites a federal civil-defense law, and shows precise statistics: 48,392 records in the database, 1,247 new entries, 12,841 persons "wanted", and a database update dated 5 October 2026. None of this is backed by verifiable provenance. The subject matter (missing soldiers and their relatives) is emotionally high-stakes, which is a typical pressure point for social engineering. The page then instructs the visitor to accept a download despite browser warnings ("download anyway"), open the file, and enable installation "from this source", which bypasses the platform's built-in protections. The search interface is cosmetic: the "processing request" and "connecting to database" text sits next to a repeat-download button. The conclusion is that the page uses the registry theme to induce installation of an unvetted file, a pattern consistent with malware delivery. Evidence:
- Homepage: claims to be the Ministry of Defense unified registry and federal missing-persons database, with specific record counts and a dated update, but gives no source, contact route or credential.
- Homepage: four-step instructions tell the visitor to dismiss download warnings and allow installation from an unknown source.
- Homepage: the search field and "connecting to database" status text appear alongside a "download again" control, with no working search results shown.
- Reputation: several major security vendors currently flag the site as malicious, and the content analysis independently marks the download prompt as a potential malware risk.
Regulatory Verification Notes
The site claims official state status but offers no licence, legal-entity disclosure, legal notice, privacy policy or official contact channel. The only legal reference is a statute cited in a footnote as the basis for the data. A genuine government service would be expected to operate from an official government domain. This one is served from a free subdomain on a general-purpose application-hosting platform, which anyone can create. Ownership and governance are not disclosed, and the real-world operator is unverified. No third-party regulatory or broker record matches the site. The statutory citation is a claim only and does not establish authority. Evidence:
- Homepage: the cited federal law and "reference only" disclaimer are the sole legal content, and no operator name or registration details appear.
- Hosting: the site is served from AS16509 (Amazon-02, Amazon.com, Inc., US), as a subdomain of a shared platform rather than a government domain.
- Transport encryption: TLS certificate issued by WR1 (DV, domain validation only), valid to 2026-11-27. This confirms an encrypted connection but says nothing about the operator's identity.
What to Verify Next
Authenticity should be tested outside the site. The Ministry's official public channels and the government's official web portals should be checked for any "unified registry" application or download of this kind. Any relative-search or missing-person enquiry should go through officially published hotlines or in-person offices. Any file already downloaded should be treated as untrusted. It should not be opened, and a device that has installed it should be scanned and, if necessary, cleaned. If the page was reached through a message, advertisement or social post, the sender should be asked through a separate channel whether they actually shared it. Evidence:
- Homepage: the stated authority (Ministry of Defense registry) can be checked against official government listings, and none is cited on the page.
- Homepage: the download and install flow is the item to treat as hazardous, rather than the search interface.
- Contact: no on-page contact route exists, so official channels must be found independently.
Summary Verdict
The assessment is critical and cautionary. Active security-vendor detections, a government-registry claim that cannot be substantiated, and a prompt to bypass installation safeguards converge into a coherent high-risk profile. The site is not evaluated as a legitimate public service.
Infrastructure Integrity
The site is fronted by Cloudflare CDN/WAF and hosted on the Vercel platform, with all observed addresses being edge servers on Cloudflare and Amazon infrastructure. This is a recognised, reputable delivery stack, but it only mitigates availability and exposure risk and carries no weight as evidence of legitimacy. It cannot offset the active threat detections. Abuse reports (57) against a Vercel address are attributed to shared provider infrastructure, carry no individual confidence, and are discounted as evidence against this site specifically.
Closing Assessment
The site should not be used for anything beyond viewing. Nothing should be downloaded or installed from it, no installation permissions should be changed in response to it, and no credentials, personal data or payments should be provided. Organisations should block access to it and warn any users who may have encountered it.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by external reputation, page content.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
Signals weighed against the site
- AbuseIPDB: 57 reports on hosting IP 64.29.17.131 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of polksvo.vercel.app.
- The request stayed on polksvo.vercel.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 64.29.17.131 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 6 flagged | AbuseIPDB: 0% confidence, 57 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about polksvo.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.