Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
pomorutecvo.vercel.app shows high-risk / scam indicators.
| What this site appears to be | Russian-language page claiming to be a unified registry (MO RF) and a federal missing persons database. Encourages downloading a file and instructs the user to allow installation from unknown sources; contains step-by-step install prompts. High risk for malware; lacks verifiable legal identity or contact information. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 6 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 78 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
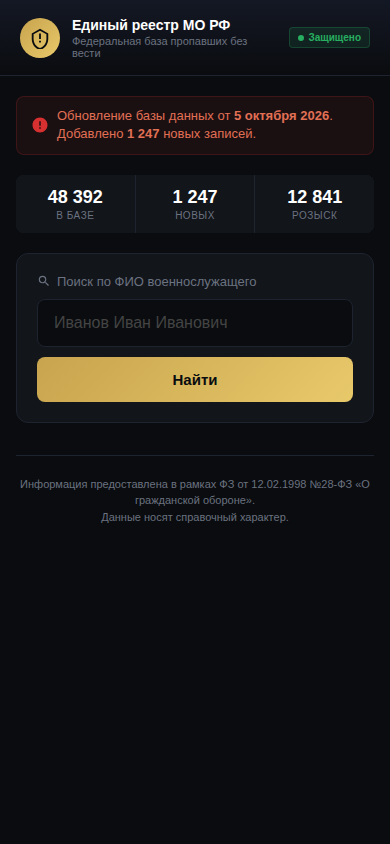
This is a Russian-language single-page website presented as a "Unified Registry" of the Russian Ministry of Defence and a federal database of missing persons. It offers a search box for servicemen by full name. After the search, the page prompts the visitor to download a file and walks them through installing it. It states no product, service or revenue model, and its apparent purpose is to deliver an installer to visitors, not to provide any registry service.
Scam/Impersonation Risk
Contradictory signals are present, and the posture is cautionary. The site is blacklisted through confirmed external threat detections: several independent reputation engines, including major endpoint-security vendors, classify it as malicious. The page content matches that classification. The homepage dresses a download lure in government authority. It claims a freshly updated registry with tens of thousands of records, a "wanted" counter, a "Protected" badge and a citation of a federal civil-defence law. It then shows a fake "Processing request… connecting to the database" state in place of any result. The visitor is told to dismiss the browser's download warning with "Download anyway", open the file, and enable installation "from this source". That sequence is the standard way to bypass operating-system safeguards for sideloaded malware. The subject matter, missing servicemen, is emotionally charged and likely aimed at relatives seeking urgent information. The page has no search results, forms, contact details, social links or legal identity, so the registry claims have no evidence behind them. Separately, a high volume of abuse reports exists against an address belonging to the shared hosting platform. Those reports are attributed to the platform's multi-tenant infrastructure, not to this site, and are discounted. They do not drive the conclusion. No conflicting legal entities appear, but the malicious-detection and installer evidence is decisive on its own. Evidence:
- Homepage: reputation engines return 6 malicious and 1 suspicious verdicts, including three leading endpoint-security vendors.
- Homepage: a four-step install guide instructs the visitor to bypass the download warning and enable installation from an unknown source.
- Homepage: counters (48,392 records, 1,247 new, 12,841 wanted) and a "database update of 5 October 2026" appear beside a search that never returns results, which indicates fabricated activity.
- Hosting-platform address: 78 abuse reports are recorded but attributed to shared infrastructure and discounted.
Regulatory Verification Notes
The site claims the standing of a state registry but names no operating body, ministry department, legal entity, registration number or official contact route. The only legal reference is a citation of a federal civil-defence law, which cannot establish that a government body operates the page. The domain is a free subdomain on a general-purpose application-hosting platform, not an official government domain. That is inconsistent with an authentic federal service. No licensing claim is made, so there is nothing to validate. The absence of identity here is part of the lure's design and is not a mere disclosure lapse. No broker or financial-regulator reputation data applies to this site. Evidence:
- Homepage: the registry claim carries no operator name, address, telephone number, email or legal notice.
- Homepage: the only legal reference is a statute citation labelled "reference data", with no issuing authority.
- Hosting infrastructure: served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
- Transport encryption: TLS certificate issued by WR1 (DV, domain validation only), valid to 2026-11-27. Encryption protects the connection but says nothing about who runs the site.
What to Verify Next
No one should download or run the file offered by this page. A person seeking information on a missing serviceman should use official Ministry of Defence or government channels. They should find those channels through independent means, such as printed notices or official sources, and not through this page. If a file from the site has already been downloaded or installed, the device should be disconnected from sensitive accounts and scanned with a reputable security product. Passwords and financial credentials used on that device should then be changed from a clean device. Any request to enable installation from unknown sources, received in connection with this site, should be reported to the relevant national cyber-incident authority. Evidence:
- Homepage: the install guide asks the visitor to change the device's source-installation settings, which is a persistent risk if followed.
- Homepage: no contact or support channel is published, so no route exists to confirm the page's claims through the site itself.
- Page behaviour: the page prompts a download and install action on load, which makes any downloaded file a priority for scanning if it is already on a device.
Summary Verdict
The site is assessed as high-risk and untrustworthy. Confirmed external threat detections combine with a page whose only function is to push an installer under a false claim of government authority. No legitimate product, operator or service is evident, and the available evidence is consistent with a malware-distribution lure.
Infrastructure Integrity
The site is served through Cloudflare and Vercel edge infrastructure, and the origin server address could not be observed. This protective layer offers minor mitigation of exposure, but it only protects the delivery path. Reputable infrastructure cannot offset the external threat detections or the behaviour of the page content.
Closing Assessment
The site should not be used for login, credential entry, financial activity or file downloads. At most, it may be viewed passively for analysis in an isolated environment, and its link should not be shared further.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Signals weighed against the site
- AbuseIPDB: 78 reports on hosting IP 216.198.79.195 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of pomorutecvo.vercel.app.
- The request stayed on pomorutecvo.vercel.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 216.198.79.195 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 6 flagged | AbuseIPDB: 0% confidence, 78 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about pomorutecvo.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.