Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
presale-sat0.com shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A SATO token presale on Base that takes ETH or USDC from users before listing, promising a 40% discount to a $0.0020 listing price. It gives no verifiable team, legal entity, audit, or contact details, uses a placeholder zero-address contract, and presents internally inconsistent sale figures, so it is rated CRITICAL risk. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-04 and re-scored on 2026-11-05. The certificate, the registration age and the page content describe the site as it was on 2026-11-04.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 15 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 6 months oldRegistered 2026-05-14 | Risk |
| Web archive | Archived since 20263 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
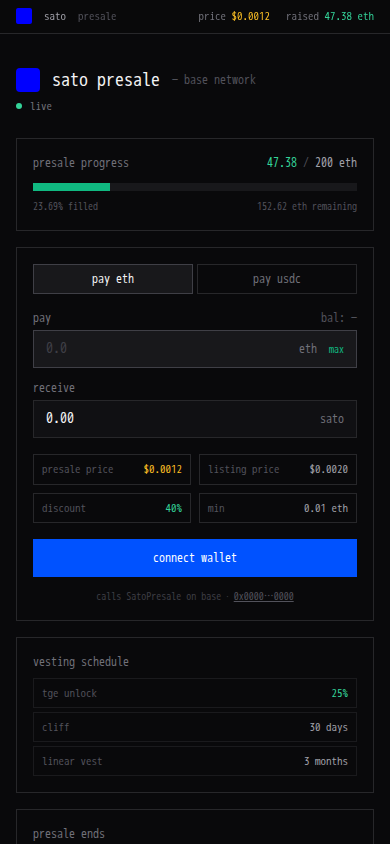
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-05-14).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
This website is a single-page presale portal for a crypto token called SATO on the Base network. It invites visitors to connect a wallet and pay in ETH or USDC to receive tokens at a stated 40% discount to a promised later listing price. It presents itself as a time-limited token sale, with a live progress meter, a countdown timer, and a vesting schedule. Its apparent business model is collecting cryptocurrency deposits from the public ahead of any token listing or delivery.
Scam/Impersonation Risk
Confirmed contradictions are present, and the site is blacklisted. A large cluster of security engines, including several major vendors, currently classify the domain as malicious, and an external blacklist feed confirms the listing. Reputation is the decisive negative here, and it is reinforced by the content. The homepage asks visitors to deposit funds before anything is delivered, at a presale price of $0.0012 against a promised $0.0020 listing price. It also adds a countdown timer showing about two hours remaining. The sale figures do not reconcile. The page states a total allocation of 2,000,000 SATO but reports 122,447,020 as sold, leaving a negative remaining balance of -120,447,020. The payment contract is shown as the placeholder zero address, 0x0000…0000, so the page does not identify where deposits would go. It also claims a soft-cap automatic refund, "no admin keys" and "no team multisig". None of these can be checked from the page, and the page itself concedes the contract is unaudited and tells participants to proceed "at your own risk". The headline figures of 47.40 ETH raised and 312 participants are likewise unsupported by any verifiable on-chain reference. No brand impersonation and no conflicting legal identities were observed. The risk therefore rests on the external detections and the structure of the offer, not on identity confusion.
- Homepage: the sale panel reports 122,447,020 SATO sold against a 2,000,000 total allocation, with "remaining" shown as -120,447,020.
- Homepage: the payment contract is displayed as 0x0000…0000, with a self-declared "contract unaudited" notice.
- Domain registered 2026-05-14 (~0.47 years old), with 3 archive snapshots, all captured on 2026-05-14 (1 year tracked), so the domain has no meaningful operating history.
- External reputation: 15 security engines flagged the domain as malicious and 2 as suspicious, enough to trigger a blacklist-level override.
Regulatory Verification Notes
The homepage names no legal entity, operating company, team member, registered address, or license, and it publishes no verifiable contact details. A token sale of this kind collecting public funds would ordinarily be expected to disclose its issuer and the regulatory basis on which it is offered. None is claimed, so no licensing status can be assessed and none can be presumed. This is a disclosure gap, and on its own it would not prove fraud. Here it sits alongside the confirmed external detections, which removes any benefit of the doubt. The tokenomics (10% presale, 40% liquidity, 35% community, 15% team locked for one year) are asserted without any supporting document, audit, or on-chain proof. No third-party broker or regulatory-register reputation signal was matched to this site, so nothing outside the page supports its claims.
- Homepage: no legal entity, team, audit report, license, or contact channel is presented anywhere on the page.
- Homepage: the stated 25% unlock at token generation, 30-day cliff, and 3-month linear vest are unsupported by any contract or documentation.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by YE1 (domain-validated only), valid to 2026-12-08.
What to Verify Next
No part of this site should be treated as verified. The SATO project's existence, its token contract, and its team should be confirmed through channels independent of this page. Examples are the project's officially published announcements or an exchange listing the user already trusts. The actual deployed contract address should be checked on a public block explorer. That check should confirm that a contract exists, who deployed it, and whether it matches the claimed refund and no-admin-key behavior, and it should be done before any funds are considered. Any listed support or contact channel should be confirmed through an independent, offline route. If the site was reached through a link, message, or advertisement, that referral source should be treated as suspect and reported.
- Homepage: the only interactive element is a wallet-payment form that automated analysis flagged as sending to an untrusted destination.
- Homepage: a wallet-connect prompt and an urgency countdown are the only active behaviors triggered on the page.
- Behavioral testing across 3 runs found no external network calls, clipboard manipulation, or wallet-drainer activity. Even so, this does not offset the external detections or the deposit-first structure.
Summary Verdict
The overall posture is critical. Strong external threat detections converge with a deposit-first, unaudited, internally inconsistent token sale from a very recently created domain. No operator is identifiable, and nothing on the site offsets these signals. The site should be regarded as a high-risk destination for any financial or credential-related interaction.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and WAF. Every observed address belongs to the provider's edge network, and the origin server is not observable. This is a mitigating factor only. It shows the site is competently hosted, but it says nothing about who operates it, and it cannot offset the reputation risk. Edge-only visibility also prevents independent hosting verification and can mask rapid content changes.
Closing Assessment
Wallets should not be connected to this site, and no ETH, USDC, or other assets should be sent to it. Any interaction beyond passive viewing should be avoided. Anyone who has already interacted with it should stop, review and revoke any wallet permissions granted, and report the domain to their security team or the relevant abuse channels.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content and several checks together.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of presale-sat0.com.
- The request stayed on presale-sat0.com. It was not redirected to another domain. Clear
- Registered through PDR Ltd. d/b/a PublicDomainRegistry.com. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-05-14. Noted
- The earliest public archive of this site is from 2026-05-14. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | PDR Ltd. d/b/a PublicDomainRegistry.com |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3036::6815:3fa2 (a CDN edge address; the server behind it was not observed) |
| Name servers | kay.ns.cloudflare.com, ray.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-08 |
| Domain age | 174 days (registered 2026-05-14) |
| Domain expiry | 2027-05-14 |
| Archive first seen | 2026-05-14 (174 days before capture) |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 15 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about presale-sat0.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.