Verdict
sigmaclient.net shows high-risk / scam indicators.
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
| What this site appears to be | A product page for 'Sigma Client', a free Minecraft Fabric 26.3 utility/cheat mod offering 200+ modules and direct download .jar files. Includes feature descriptions, installation steps, FAQ, and download links. Non-financial and claims to be open-source and free. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 11 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0 reportsAbuseIPDB; shared hosting inflates this count | Noted |
| Domain age | 5 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 2021Public history exists | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
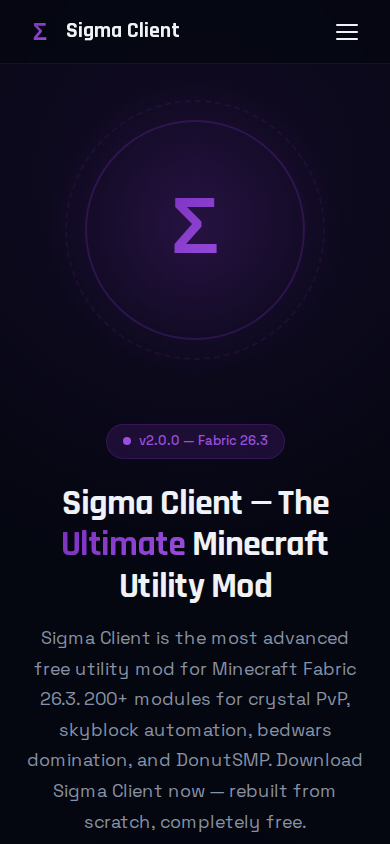
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2021.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Sigma Client is a software-download website presenting a free Minecraft Fabric 26.3 utility and cheat client, with more than 200 advertised modules, installation guidance, feature descriptions, FAQs, and direct Java archive downloads. Its apparent model is community or direct-download distribution rather than paid transactions, with the site claiming that the software is open-source, free, and without subscriptions.
Scam/Impersonation Risk
Confirmed external contradiction signals materially outweigh the site’s benign presentation. The domain is reported as blacklisted by two external sources, with 11 malicious and 2 suspicious detections in the evaluated reputation results; Fortinet and Kaspersky were among the flagged vendors. The site itself does not present a login form, credential-collection workflow, wallet connection, or observed external network activity, and its page-level content contains no explicit phishing or brand-impersonation indicators. Nevertheless, direct distribution of executable `.jar` files, combined with the external malicious detections, creates a significant software-integrity and sensitive-interaction risk. No distinct legal-entity identity contradiction was observed, but the operator’s real-world identity remains unverified.
- The homepage presents “Sigma Client” as a free Minecraft Fabric 26.3 mod with 200+ modules, including combat, movement, automation, anti-cheat bypass profiles, and direct download links.
- The reputation assessment records a confirmed blacklist, 11 malicious detections, 2 suspicious detections, and threat detections associated with Fortinet and Kaspersky.
- Behavioral inspection recorded no login form, no hidden sensitive form, zero external requests, zero wallet activity, and no clipboard-write activity.
- Domain-history telemetry records 0 archive snapshots, first seen on 2021-12-24, last seen on 2023-04-08, and 3 years tracked.
Regulatory Verification Notes
The site is a software-download service rather than an identified financial or regulated service, and no financial licensing claim is presented in the supplied page evidence. The available material does not independently establish the operator’s legal identity, corporate affiliation, or software-distribution authority; on-page disclosure is therefore unclear. This is a verification gap rather than a separate allegation of fraud, but it is important because the principal user interaction is downloading executable software. The domain registration record identifies Web Commerce Communications Limited dba WebNic.cc as registrar. Transport security is present, but a domain-validated certificate authenticates the domain connection, not the operator or the downloaded files.
- The page presents no license authority or license number and does not independently identify a verified operating entity.
- WHOIS telemetry records creation on 2026-04-12, an age of 0.44 years, and expiration on 2027-04-12; the registrar is Web Commerce Communications Limited dba WebNic.cc.
- The site is served through AS214351, identified as FEMOIT - FEMO IT SOLUTIONS LIMITED, GB.
- The TLS certificate is issued by YR1 using domain validation and is valid through 2026-12-20.
What to Verify Next
Before any download or installation, the file should be obtained only from an independently authenticated project release channel and inspected in an isolated environment with current endpoint and malware-scanning controls. The claimed open-source status should be matched to a publicly accessible source repository and reproducible release history rather than accepted from the site alone. An independent route should also be used to confirm the project’s official support and contact channels, and any reported detection should be reviewed with the relevant security vendors before execution.
- The homepage claims the client is open-source and free but supplies no independently verified repository or organizational identity in the supplied evidence.
- The download page distributes executable `.jar` files and provides installation instructions.
- The site’s FAQ and feature sections make operational claims about anti-cheat bypass profiles and automated gameplay modules that should be assessed against the software’s actual contents.
- The page-level analysis found no sensitive form or payment workflow, so the principal immediate verification task concerns file provenance and execution safety.
Summary Verdict
The website has a critical trust posture for sensitive interaction. Its clear product presentation and absence of observed credential-harvesting behavior do not offset the confirmed blacklist status and concentrated external malicious detections. The operator identity is unverified, so the site cannot be treated as an authenticated or dependable software source.
Infrastructure Integrity
The website is protected by Cloudflare CDN/WAF infrastructure, which is a mitigating control against direct exposure and can help absorb or filter traffic. The observed address was an edge address, and the origin server was not observable in this analysis; this limits independent verification of the underlying host and permits the possibility of rapid content changes. The infrastructure therefore provides defensive protection but does not establish legitimacy.
Closing Assessment
Prospective users should refrain from executing downloaded files unless provenance, contents, and security-vendor findings have been independently resolved in a controlled environment. Account credentials, sensitive data, and other high-impact interactions should not be exposed to the site.
Written analysis generated 2026-09-22 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by registration and ownership, analysis engine, external reputation.
01 Governance Risk
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
02 Sensitive Interaction Risk
- The analysis matched a pattern TrustSniffer treats as a direct threat to a visitor.Analysis engine
signal:direct_threat - An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of sigmaclient.net.
- The request stayed on sigmaclient.net. It was not redirected to another domain. Clear
- Registration is published under Web Commerce Communications Limited dba WebNic.cc. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-04-12. Noted
- The earliest public archive of this site is from 2021-12-24. Clear
- It is hosted on FEMOIT, from a server in SC. Noted
Domain intelligence
| Registrar | Web Commerce Communications Limited dba WebNic.cc |
|---|---|
| Hosting | FEMOIT - FEMO IT SOLUTIONS LIMITED, GB |
| Country | SC |
| Server IP | 196.251.107.204 |
| Name servers | ANDY.NS.CLOUDFLARE.COM, BRENNA.NS.CLOUDFLARE.COM |
| SSL issuer | YR1 |
| SSL expiry | 2026-12-20 |
| Domain age | 0.44 years (continuous registration) |
| Domain expiry | 2027-04-12 |
| Archive first seen | 2021-12-24 |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 11 flagged | AbuseIPDB: 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about sigmaclient.net at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.