Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
snapshots-kamino-102.pages.dev shows high-risk / scam indicators.
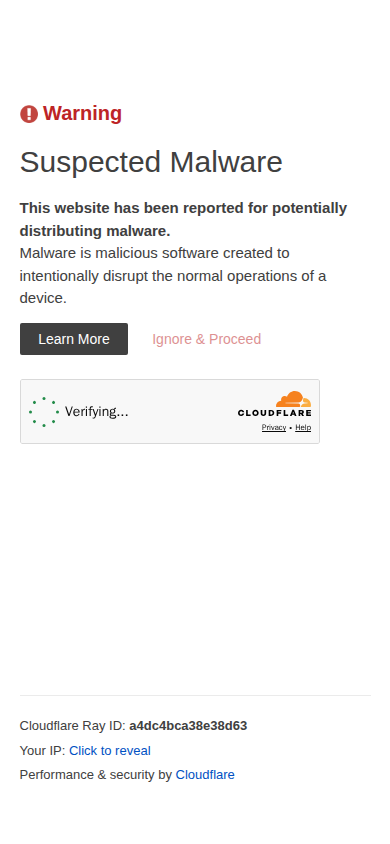
| What this site appears to be | The captured page is a Cloudflare interstitial warning that the requested website has been reported for potentially distributing malware. It offers a 'Learn More' link and an 'Ignore & Proceed' option. No underlying site content, forms, or claims are visible. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a numbered subdomain on a free, shared web-hosting platform. When the analysis system tried to load it, the visitor saw only a security interstitial, not any site content. The interstitial states that the site "has been reported for potentially distributing malware" and offers an "Ignore & Proceed" button. No products, services, forms, legal pages or business claims were visible. The site's apparent purpose and business model therefore cannot be determined, and the only observable function of the page is to warn visitors away.
Scam/Impersonation Risk
The contradictions here are hard and come from reputation, not from conflicting identity claims. Several independent threat-intelligence engines classify the domain as malicious or suspicious, including at least one top-tier network-security vendor. This convergence is why the domain is treated as blacklisted. The visitor-facing warning matches those listings, so the two sources corroborate each other. No conflicting legal entities were found, and no phishing page or brand impersonation was confirmed. The danger is the possible distribution of malicious software, not a confirmed impersonation. Because the underlying content was never visible, the specific payload or lure cannot be described. The hosting platform allows anyone to publish disposable sites on free subdomains. That makes the reported behaviour harder to attribute to an accountable operator and easier to repeat under a new address. Behavioural testing also showed heavy third-party request activity and repeated console errors on the captured page. The traffic went to recognised destinations, so it is a minor observation next to the reputation findings. Evidence:
- The homepage capture is a security interstitial warning of suspected malware distribution, with a bypass option, and no site content behind it.
- Four threat-intelligence engines flagged the domain as malicious and one as suspicious, and an external blacklist confirmation is recorded.
- The sandbox saw 21 external XHR requests and 9 external POSTs across three runs, none to non-whitelisted destinations, plus 18 console errors.
- The page showed no login form, no hidden forms and no wallet-connection behaviour.
Regulatory Verification Notes
No legal, about, terms or licensing pages were reachable, because the only content captured was the warning interstitial. The site claims no licence or registration, so there is no regulatory status to assess. No third-party broker or regulatory-database record exists for this site. A licence check would have no basis here and cannot offset the reputational findings above. The site presents no operator name, jurisdiction or accountable entity, so its real-world identity remains unverified. The site's TLS certificate is valid and issued by a recognised authority. This confirms an encrypted connection only. Domain-validated certificates are issued automatically and say nothing about the operator's legitimacy. Evidence:
- The site's hosting infrastructure is on AS13335 (Cloudflare, Inc., US).
- The TLS certificate was issued by YE2 at domain-validation (DV) level and is valid to 2027-01-04.
- No licence, regulator, company name or registration number appears anywhere in the captured content.
- No third-party broker-reputation match was found.
What to Verify Next
Do not interact with the site beyond viewing the warning. Confirm whether the warning has been cleared by checking the same address in the hosting platform's abuse-reporting channel and in independent reputation checkers. If someone sent the address as a link or download, ask the sender to confirm through a separate, trusted channel that it is legitimate. Scan any device that has already opened the page or downloaded anything from it with up-to-date endpoint security. If the site is claimed to belong to a known organisation, confirm that its official address matches by navigating from that organisation's own channels. Do not rely on this address. Evidence:
- The captured page itself says the site is reported for potential malware distribution.
- The address sits on a shared free-hosting platform, so ownership is not implied by the platform.
- Browser behaviour flags recorded a malware-warning page with a proceed-anyway option.
Summary Verdict
The evidence supports a clearly cautionary, high-risk posture. External threat detections are decisive, and the site cannot be treated as safe for credentials, financial activity or downloads. The only favourable signals are technical hygiene, such as a working encrypted connection. They do not offset the reputational findings and do not establish who runs the site.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and WAF. All four observed addresses are Cloudflare edge servers, and no origin server was observable. This is protective infrastructure and a mitigating factor only. It does not make the content safe, and it limits independent verification of where the content is actually hosted. The warning page appears to come from this layer and is consistent with the external reports.
Closing Assessment
Treat the address as unsafe. Do not log in, enter credentials, make payments or download files from it, and limit any contact to viewing the warning. If the page has already been opened and anything was downloaded or entered, run a security scan and change any exposed credentials.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of snapshots-kamino-102.pages.dev.
- The request stayed on snapshots-kamino-102.pages.dev. It was not redirected to another domain. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2c50 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2027-01-04 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about snapshots-kamino-102.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.