Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
the-robo.web.app is low-trust and potentially risky.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 3% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | 2 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20263 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WR4 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
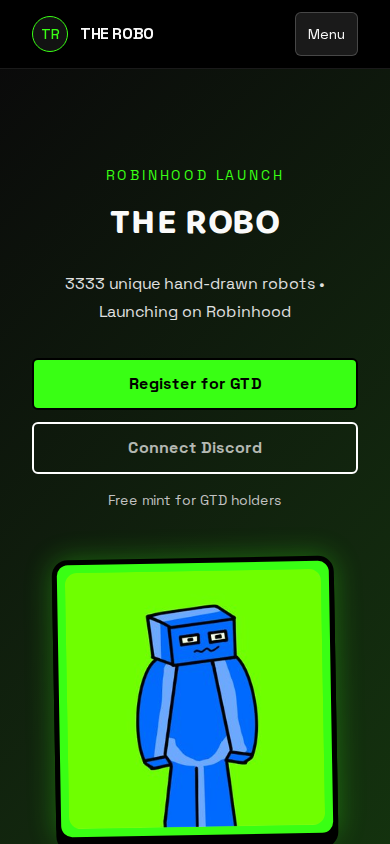
The-robo.web.app is a single-page promotional site for "THE ROBO NFT Collection", which advertises 3,333 hand-drawn robot artworks. Its captured homepage carries only a short block of text. It appears to be a digital-collectible launch or showcase page, and its apparent business model is selling or promoting NFT artwork to retail buyers.
Scam/Impersonation Risk
Contradictory signals are present, and this section is the main reason for the cautionary posture. The domain appears on an external blacklist: one security engine rates it malicious and another rates it suspicious. This is a confirmed adverse reputational hit, not a mere broker opinion. It is compounded by the site's extreme youth. The domain was created only weeks before the assessment, and its web-archive footprint is thin. A page selling a numbered NFT collection on a freshly created domain, with a blacklist hit, matches a recognisable pattern for short-lived collectible promotions, so the combination warrants treating the site as elevated risk. Four abuse reports exist against one of the site's edge addresses. These relate to shared provider infrastructure and carry a very low confidence rating, so they are weak corroboration and not an accusation against the site itself. Behavioural testing did not reinforce the blacklist hit. Across three sandbox runs, the page returned stable responses and showed no wallet-connection prompts, clipboard tampering, hidden forms, cloaking, or credential posts to external destinations. Its background traffic to third-party services was heavy but went entirely to recognised destinations. No brand impersonation or conflicting legal identities were observed. These observations narrow the threat picture but do not offset the blacklist hit. Evidence:
- Homepage domain: one security engine flags it as malicious and one as suspicious, producing an external blacklist match.
- Domain is about 47 days old (~0.13 years).
- Web archive holds only 3 snapshots, spanning 2026-09-08 to 2026-09-22 (1 year tracked).
- Sandbox runs on the homepage: 3 of 3 successful, 0 console errors, 0 wallet-connect or drainer behaviours, and 0 external form posts of passwords.
Regulatory Verification Notes
The site is not shown to be regulated or registered anywhere. The homepage text gives no clear indication of who operates the collection or under what legal entity. Real-world operator identity therefore remains unestablished, and on-site claims cannot be treated as proof of legitimacy. For an NFT sales page, the lack of a named issuer, terms or a stated jurisdiction matters most. Buyers would have no obvious route to recourse. This is a verification gap and not evidence of wrongdoing by itself. In this case it adds weight to the separate blacklist hit. No third-party broker record matched the site. The technical transport layer is sound, but this shows only baseline hygiene and says nothing about the operator. Evidence:
- Homepage: the captured text identifies no operating entity, licence, registration number or jurisdiction.
- Served from AS54113 (Fastly, Inc., US).
- TLS certificate issued by WR4 (DV, domain-validated only), valid to 2026-12-22, with 57 days remaining.
What to Verify Next
Before any engagement, the operator behind the collection should be identified through independent, off-site sources, such as a named team with a verifiable track record. Any claimed mint or smart contract should be matched against a public blockchain explorer and a recognised marketplace listing, not against links on this page. Official social accounts and support channels should be confirmed through an offline or independent route. The blacklist status should be rechecked later, because a listing on a very young domain may change. A site owner that was compromised and then cleaned would be delisted. A listing that persists would reinforce the concern. Evidence:
- Homepage title advertises a 3,333-piece hand-drawn collection, but the captured text does not establish who issues it.
- The domain's youth and thin archive history leave no long-run track record to rely on.
- The external blacklist hit on the homepage domain is current and unresolved.
Summary Verdict
The available evidence supports an elevated-risk assessment. A confirmed external blacklist hit on a very new domain outweighs the site's sound technical hygiene and clean behavioural testing. Apparent legitimacy cannot be concluded, and real-world identity is unverified. The site should be treated as unsafe for sensitive or financial interactions.
Infrastructure Integrity
The site is delivered through Fastly, a mainstream CDN and WAF, and both observed addresses are edge servers. The origin host was not observable, so hosting cannot be independently verified through this layer. The CDN provides a valid, properly issued TLS channel and mitigates some exposure, but it is protective infrastructure only. It does not vouch for the content or operator, and it cannot offset the reputation risk.
Closing Assessment
The site should be treated as read-only. No wallet should be connected, no credentials entered, and no payment or minting transaction made through it until the operator is independently identified and the blacklist status is cleared.
Written analysis generated 2026-10-25 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, hosting and network, history in the web archive, behaviour in a sandbox, registration and ownership.
01 External reputation
- A small number of malware engines flagged this domain. On its own this is a weak signal.External reputation
rule:EXT_BLACKLIST_MEDIUM
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
05 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (Google LLC, Content Delivery Network), 3% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of the-robo.web.app.
- The request stayed on the-robo.web.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-09-08. Clear
- It is hosted on FASTLY, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc., US |
| Country | US |
| Server IP | 2620:0:890::100 |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| Domain age | 0.13 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-09-08 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 3% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about the-robo.web.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.