Verdict
This assessment found strong scam indicators on the site itself. Do not pay, sign in, or share personal details with this site.
thefullz.shop shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: a form asks for sensitive details and sends them to a destination that could not be verified. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A marketplace advertising stolen identity packages, payment card data, bank logins, P2P cash-out and Western Union transfers, payable only in BTC or USDT with orders handled via Telegram. The page describes fraud-enabling services, so it is a critical-risk, untrusted site with no verifiable legal identity or lawful product. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- 8 VirusTotal engines (Fortinet, Sophos among the engines that flagged it) marked this site as malicious when the evidence was captured on 2026-11-13, which meets TrustSniffer's bar for a confirmed listing. On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain registration record (WHOIS), name servers (DNS).
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) also applies, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 8 marked it malicious, 1 suspiciousVirusTotal; Fortinet, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 56% confidenceAbuseIPDB, 1374 reports; shared hosting inflates reports | Risk |
| First seen | 2.6 years before captureWeb archive; no registration record was returned | Clear |
| Web archive | Archived since 202418 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: 1 to 3 years before capture (web archive; no registration record was returned).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
8 VirusTotal engines, including Fortinet, Sophos, marked this site as malicious; this meets TrustSniffer's bar for a confirmed listing.
Overview
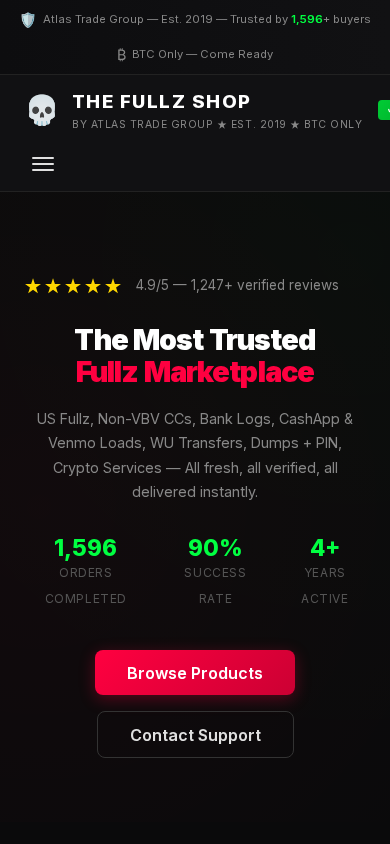
A marketplace presenting itself as The Fullz Shop, run by a group calling itself Atlas Trade Group, that sells stolen personal and financial data and cash-out services. The homepage advertises "complete identity packages", described as SSN, date of birth, driver's licence, address and bank information, from $80. It also lists card data from $50, bank-login batches, CashApp and Venmo balance loads from $100, and Western Union transfers with a tracking code promised "in 2hrs". Payment is accepted only in Bitcoin or USDT, and orders and support are routed through Telegram. The apparent business model is per-item sales plus fees on laundering-style transfers and exchange-account "off-ramp" services. The pages offer no lawful product.
Scam/Impersonation Risk
The site's own offering is the core finding. It sells credentials and identity data that belong to other people. It also advertises 30+ banks across the US, UK and Canada with "full login + email access", and a bank-log batch described as "Chase $47k, Wells $124k, BOA $238k". Its tagline is "We move product. Discreetly.", and the order flow demands "BTC ONLY — Come ready or don't come at all". The urgency language and the crypto-only payment to a generated address mean a buyer would pay irreversibly, with no recourse. The "replacement within 48 hours" guarantee is an unenforceable promise from an anonymous counterparty. The page also names major exchanges (Binance, Coinbase, Kraken) only as "verified exchange accounts" it claims to sell. It does not pose as those brands, and no brand impersonation was detected. No conflicting legal-entity names appeared on the pages read. The critical-risk assessment therefore rests on what the site sells, its scored technical findings and a confirmed external listing, not on a mimicked identity. That listing meets TrustSniffer's bar for a confirmed listing: eight engines, including leading vendors Fortinet and Sophos, flagged the site as malicious, and one further engine flagged it as suspicious. The site's trust theatre also does not hold together. It shows "trusted by 1,092+ buyers", "17 buyers online now" and a 4.9/5 rating from 1,247 "verified buyer reviews", which is more reviews than the completed orders it reports. The site's own pages also give different totals for orders, success rate and replacement window. The "Est. 2019" claim is not supported by the web-archive history, which first shows the domain in 2024.
- Homepage: the title says "Since 2022", the banner says "Est. 2019" and the body says "4+ years active". The shop and group may differ, but none of the dates is independently supported.
- Homepage and the Western Union page: order totals (2,505 versus 2,479), success rate (90% versus 97.8%) and buyer counts (1,092 versus 996) differ between the pages.
- Web archive: the domain was first seen on 2024-04-15 (942 days before capture), with 18 snapshots between 2024-04-15 and 2026-03-07 (a 691-day span, largest gap 235 days).
- VirusTotal: 8 engines malicious and 1 suspicious, including Fortinet and Sophos.
Regulatory Verification Notes
On the pages read (the homepage and the Western Union page), the site makes none of the disclosures expected of a financial-services business. Neither a registration or licence number nor a regulator is stated. The only legal-entity reference is a footer line crediting Atlas Trade Group and the shop's Telegram handle. A Privacy & Security link and a refund and replacement policy are present. The "refund" is a free replacement of "dead fullz and CCs". It is a sales guarantee for stolen data, not a consumer-protection term. The homepage withholds its email contact. Contact is available only through Telegram and a free webmail address, so no postal address, company registration or named individual could be tied to the site. The on-site name is a self-description, and no outside check ties it to a real-world operator. No third-party broker or regulatory record matched the site. A licence would not alter the assessment, because the goods offered are unlawful.
- Homepage: the footer credits Atlas Trade Group and the shop's Telegram handle, and the contact line is withheld.
- Homepage: Privacy & Security, FAQ, Refund & Replacement Policy and Shipping & Delivery pages are linked. The pages read state no licence, registration number or regulator.
- Hosting infrastructure: served from AS16509 (AMAZON-02, Amazon.com, Inc.), US registry.
- Transport encryption: a DV TLS certificate from issuer YE1, seen valid to 2027-01-10. It only encrypts traffic and says nothing about the operator.
What to Verify Next
Verifying the operator is not meaningful here, because the offering itself is the problem. The useful steps concern containment and reporting. An organisation that finds this site linked from an email, advert or message should route it to its security or fraud team and block the domain. Banks or card programmes that suspect their customers' data is being sold can pass the matter to their fraud and threat-intelligence functions. Reports can also go to the hosting provider's abuse desk and the national cybercrime reporting channel. The official support channels of any institution named in the site's listings should be confirmed through that institution's own published route, not through anything on this site.
- Homepage: the bank-log batch listing names specific institutions and balances, which gives affected institutions a concrete reference for escalation.
- Homepage: the order form takes crypto payment to a generated address and sends orders to Telegram, so no recoverable payment path exists.
- Western Union page: the "pick up cash worldwide" transfer service gives a second concrete item for reporting.
Summary Verdict
The site is assessed as critical risk. It is a marketplace for fraud-enabling goods and services, and its own content, its scored technical behaviour and external threat detections all point the same way. Its on-site identity is a self-description that has not been independently verified, and nothing observed offers a mitigating counterweight.
Infrastructure Integrity
The site was served from Amazon's hosting network, with two IP addresses and no CDN detected. A CDN or its absence is neutral. Nothing in the hosting arrangement offsets the findings above. A check of the host address's abuse record found 1,374 abuse reports, attached to a shared provider address in the same hosting network. Those reports are not attributed to the site specifically. In the sandbox, the page sent 9 requests to destinations TrustSniffer does not recognise, six of them POSTs. 61.9% of the files it loaded came from other domains, and a large structural change followed interaction. These behaviours are scored findings. The sensitive payment-and-order form also posts to an untrusted destination.
Closing Assessment
The site should not be used. No orders should be placed, no cryptocurrency sent and no data entered into its order form. Its Telegram channel should not be contacted. Anyone who encounters it should treat it as hostile and report it through the channels above.
Written analysis generated 2026-11-13 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
19 findings contributed to this verdict, raised by external reputation, page content, several checks together, behaviour in a sandbox, and registration and ownership.
01 External reputation
- 8 VirusTotal engines, including a leading vendor (Fortinet, Sophos), marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL - The server address behind this site has a strong record of abuse reports.External reputation
rule:EXT_ABUSEIP_SEVERE - An external threat signal for this site is backed up by something the analysis observed on its own.External reputation
rule:EXT_THREAT_CORROBORATED
02 Page content
- A form on the page submits to a destination TrustSniffer could not verify.Page content
rule:PAGE_FORM_UNTRUSTED_DEST - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS - The page asks visitors for sensitive information.Page content
rule:PAGE_FORM_SENSITIVE - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Behaviour in a sandbox
- The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - A large share of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE - The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS - An automated reading of the page's network activity judged some requests unusual for this kind of page.Behaviour in a sandbox
- The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
05 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY
Signals weighed against the site
- AbuseIPDB: 1374 reports on hosting IP 63.176.8.218 (AMAZON-02), 56% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Third-party connections: 4 findings share one limit, because they all measure one fact: the page loads files from other hosts. The limit applied, so together they counted for less than their sum.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
- Certificate and search-engine setup: 3 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Thefullz Shop
- contact:email
- on_site_identity
- Phone number shown on the page: +1 220 212 1351 (not checked)
- Email address shown on the page: a free-mail address at gmail.com (not checked)
What TrustSniffer observed
First-party facts recorded during the assessment of thefullz.shop.
- The request stayed on thefullz.shop. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-04-15. Clear
- It is hosted on AMAZON-02, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 63.176.8.218 |
| Name servers | Not available |
| CDN / edge network | Not detected |
| Resolved IP addresses | 2 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 2 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-10 |
| First seen (web archive) | 2.58 years before capture; no registration record was returned |
| Domain expiry | Not available |
| Archive first seen | 2024-04-15 (2.6 years before capture) |
| Archive snapshots | 18 |
| Reputation | VirusTotal: 8 malicious, 1 suspicious | AbuseIPDB: 56% confidence, 1374 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about thefullz.shop at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.